Category: Defense

  • BAE Systems Completes Live Trials of BATS Integrated Counter-Drone System in Scotland

    BAE Systems Completes Live Trials of BATS Integrated Counter-Drone System in Scotland

    BAE Systems has completed a two-week series of live trials in Scotland of its Anti Threat System (BATS), an integrated counter-drone capability that links detection, operator decision-making and engagement through a single command-and-control architecture, the company reported.

    Three Test Scenarios

    The trials exercised BATS across three operational scenarios. The first assessed whether data from multiple sensors could be fused into a common operational picture, letting operators detect, identify and track airborne objects while distinguishing drones from non-threatening activity. The second scenario tested integration of electronic warfare and software-defined radio technology, with operators applying non-kinetic countermeasures to confirmed targets in near-real time. A third scenario ran a full detection-to-engagement sequence in a more complex tactical setting, including an integrated gun system, with operators confirming drone categories and selecting an appropriate effector for each threat.

    Open, Scalable Architecture

    BATS is built by BAE Systems’ Digital Intelligence business as a software-driven, open-architecture system intended to let customers plug in existing and future sensors and effectors rather than relying solely on expensive missile-based interceptors. The Scottish trials follow earlier integration and deployment testing completed in July 2026, which took the system from concept to field trial in about eight months. Human operators retained decision authority throughout the exercises, with BAE Systems stating the tests demonstrated the full “sense, decide, effect” mission chain against uncrewed aerial threats.

    BAE Systems has not disclosed a customer, contract value or procurement timeline tied to the trials. More counter-UAS developments are tracked in the SectechMedia Technology News archive.

    Sources

  • Pentagon Personnel Agency Data Breach Exposes Records of About Three Million People

    Pentagon Personnel Agency Data Breach Exposes Records of About Three Million People

    The US Defense Manpower Data Center has begun notifying people that unauthorized users accessed files containing personal information on one of its file-sharing servers. Reporting based on the agency’s notification and a Defense Department official places the affected population at roughly three million living and deceased individuals.

    The exposed server held unencrypted personnel data

    The notification says a vulnerability discovered on July 16, 2026 allowed unauthorized access to files. Investigators found that a small number of users had accessed the server between October 2025 and discovery. The center patched the file-sharing system and restored service after identifying the weakness.

    Records varied by person and could include names, Social Security numbers, dates of birth, contact details, demographic information and military occupational specialties. The agency said it had not identified misuse when notices were issued.

    Long exposure windows increase investigation demands

    Incident teams must determine which files were reached, which identities were exposed and whether access persisted across credential or server changes. Sensitive government repositories require encryption, least privilege and alerting on abnormal file access. SectechMedia follows related controls in its cybersecurity coverage.

    Sources

  • United States and China Agree to Create AI Incident Communication Channel

    United States and China Agree to Create AI Incident Communication Channel

    The United States and China have agreed to establish a communication mechanism for incidents involving artificial intelligence. The step was announced alongside plans to strengthen military crisis communications following bilateral talks in Washington.

    The channel is intended to contain escalation risk

    Public statements describe a mechanism for discussing AI-related incidents, risks and benefits, with a dedicated dialogue expected to follow. The available details do not define reporting thresholds, technical interfaces or whether private-sector incidents will be included.

    Even a limited government-to-government channel can be relevant when an AI failure affects critical infrastructure, defense systems, information operations or cross-border digital services. Rapid attribution is difficult, and incomplete information can turn a technical event into a political crisis.

    Operational value will depend on implementation

    A useful channel needs authenticated points of contact, evidence-handling rules, escalation levels and procedures for preserving sensitive information. Exercises can reveal whether notifications reach the right technical and policy teams during a time-critical incident.

    The agreement does not replace domestic incident response or vendor accountability. It adds a diplomatic layer for events with international consequences. SectechMedia covers the overlap between technology and national resilience in its Defense section.

    Sources

  • Japan Disrupts North Korean Laptop Farm as Allies Detail WaterPlum Campaign

    Japan Disrupts North Korean Laptop Farm as Allies Detail WaterPlum Campaign

    Japanese authorities have dismantled what security reporting describes as the country’s first identified North Korean laptop farm, an operation designed to support overseas information-technology workers while concealing their actual location. The action follows a joint advisory from agencies in Japan, the United States, Australia and Germany on the North Korean activity cluster known as WaterPlum, also widely called Contagious Interview.

    Remote work as an access channel

    The allied advisory says the campaign targets technology professionals and organizations through fraudulent recruitment, fake interviews and malicious software. Separate laptop-farm arrangements can allow remote workers to appear as if they are connecting from an approved country, while local devices and facilitators obscure the operator’s real location. That combination creates both insider-risk and endpoint-security concerns for employers.

    Organizations should verify applicants beyond documents and video calls, compare claimed location with network and device telemetry, and restrict access until employment checks are complete. Unexpected remote-management tools, inconsistent working hours, unusual payment arrangements and repeated identity anomalies deserve coordinated review by human resources, security and legal teams.

    Security relevance

    The case shows why remote-work controls belong inside a broader cyber-physical security program. Identity checks, managed endpoints, least privilege and continuous monitoring reduce the chance that a fraudulent worker can become a persistent route into sensitive systems.

    Sources

  • US Air Force Seeks Deployable Counter-UAS Package

    US Air Force Seeks Deployable Counter-UAS Package

    The U.S. Air Force is seeking a deployable counter-UAS package intended to address gaps in the protection of operating locations. A federal opportunity notice identified by Unmanned Airspace points to demand for a capability that can be moved, established and integrated without relying on a permanent site architecture.

    What deployability changes

    A transportable system must balance coverage with logistics. Sensors, command equipment, power, communications and any authorized effectors have to fit the deployment concept and become operational within a useful period. Equipment that performs well at a fixed test range may behave differently when terrain, electromagnetic conditions and local air traffic are unfamiliar.

    The requirement also highlights the importance of interoperability. Counter-UAS packages need to exchange tracks and alerts with base-defense teams while preserving evidence for later review. Identification and escalation procedures must account for friendly drones, contractors and civilian activity near the protected area.

    Evaluation priorities

    Field testing should examine false alerts, setup repeatability, track continuity and operator workload, not merely maximum detection range. Sustainment, software updates and training can determine whether a deployable system remains useful after the initial exercise. The solicitation adds another procurement signal in the expanding counter-UAS market.

    Sources

  • Denmark Buys Weibel Radars for Military Counter-Drone Operations

    Denmark Buys Weibel Radars for Military Counter-Drone Operations

    Denmark’s defense acquisition organization is purchasing radars from Danish manufacturer Weibel Scientific for military counter-uncrewed-aircraft operations. The procurement reflects the growing emphasis on dedicated detection as armed forces respond to small and fast-moving aerial threats.

    Detection before engagement

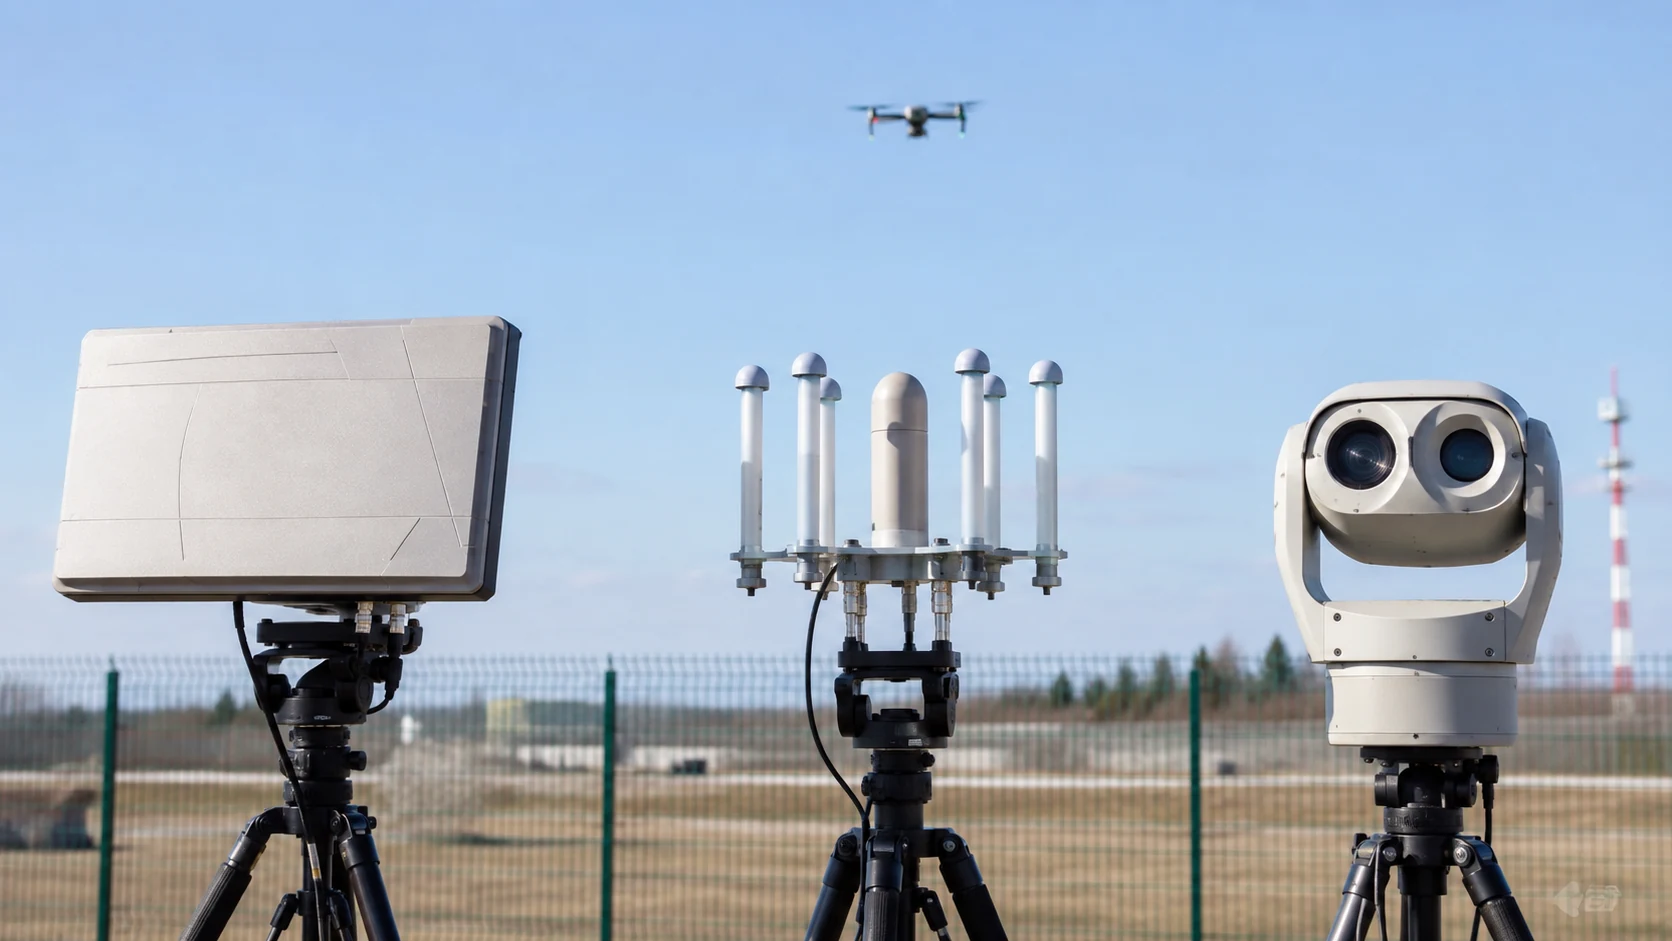
    Unmanned Airspace reported the purchase on 21 September, citing Denmark’s defense procurement authority. Radar is one part of a counter-UAS chain that may also include radio-frequency sensing, electro-optical confirmation, command-and-control software and an authorized mitigation method. The sensors must provide tracks that operators can classify and correlate before any response is selected.

    Small aircraft create difficult conditions because terrain, buildings, birds and legitimate aviation can generate clutter or competing tracks. Performance therefore depends on siting, calibration and integration as much as on the sensor specification. Military deployments also need clear procedures for transferring tracks among local units and wider air-defense networks.

    Integration is the central test

    The acquisition should be judged by field acceptance, data quality and operational fit rather than radar count alone. Track continuity, false-alert handling and identification workflows are particularly important near bases and civilian airspace. Denmark’s purchase adds to European investment in counter-UAS and airspace security amid concern about both hostile drones and ambiguous incursions.

    Sources

  • Honeywell Modernizes Access Management Across U.S. Marine Corps Barracks

    Honeywell Modernizes Access Management Across U.S. Marine Corps Barracks

    Honeywell Technologies has announced a modernized access-management program for U.S. Marine Corps barracks worldwide. The deployment is intended to replace fragmented mechanical-key and local access processes with connected electronic controls and centralized management.

    The program is designed to give authorized personnel a consistent way to issue, revoke and audit access across geographically distributed facilities. A centralized model can reduce the delay between a change in authorization and enforcement at the door, while producing records that support investigations and compliance reviews.

    Neither the company announcement nor secondary reporting provides a complete public architecture, device count or cybersecurity assessment. Those details matter because a global access platform must protect credentials, administrative privileges, network paths and offline operation as carefully as it protects doors. Local emergency procedures must remain workable during network or power disruption, including reliable override, accountability and recovery controls.

    Why it matters

    Barracks access is an identity-lifecycle problem as much as a lock problem. The program highlights the value of centralized governance while reinforcing the need for resilient local operation, auditable credential changes and disciplined key and credential management.

    Sources

  • Northrop Grumman Advances 50mm Proximity-Fuzed Round for Raid Hunter Air Defense

    Northrop Grumman Advances 50mm Proximity-Fuzed Round for Raid Hunter Air Defense

    Northrop Grumman says it has completed an aeroballistic test of a new 50mm projectile for Raid Hunter, the company’s gun-based air-defense system. The test used an XM913 Chain Gun and generated flight data intended to support development of a guided, proximity-fuzed round.

    The company said the rounds produced high-fidelity data for nearly every shot and broadly matched pre-test predictions. Raid Hunter is being positioned as a short-range option for engaging mixed raids that can include low-cost uncrewed aircraft. Northrop Grumman has not published enough test data for independent assessment of accuracy, engagement envelope or cost effectiveness.

    Proximity fuzing is intended to improve the probability of effect without requiring a direct projectile impact. In a counter-UAS role, however, overall performance also depends on sensor quality, target classification, fire-control integration and the safety constraints surrounding the defended area. Follow-on testing will need to demonstrate the complete engagement chain.

    Why it matters

    Gun-based systems are attracting attention as operators look for repeatable defenses against larger drone salvos. The test is a development milestone, not proof of field performance, and should be assessed as one element in a layered airspace-security architecture.

    Sources

  • JIATF-401 Awards More Than $25 Million for Southern Command Counter-UAS Capabilities

    JIATF-401 Awards More Than $25 Million for Southern Command Counter-UAS Capabilities

    The U.S. Department of Defense has awarded more than $25 million in multiple procurements to expand counter-uncrewed aircraft capabilities supporting U.S. Southern Command. The package includes interceptors and electronic-warfare systems intended to provide layered detection, tracking and defeat options against small drones.

    The awards were made through Joint Interagency Task Force 401. The task force said its accelerated acquisition process moved the selected capabilities from an operational requirement to fielding in less than a month. Officials described the work as an effort to improve air-domain awareness and precision defeat options across Southern Command’s area of responsibility.

    The announcement did not provide a complete public list of vendors, quantities or performance specifications. That limits direct technical comparison, but the combination of electronic-warfare and interceptor procurements indicates an emphasis on layered response rather than reliance on a single defeat mechanism. Sustainment, spectrum coordination and operator certification will also influence operational value.

    Why it matters

    Rapid acquisition can shorten the gap between a changing drone threat and deployed defenses. It also increases the importance of integration testing, rules of engagement, operator training and evidence-based evaluation across the full counter-UAS chain.

    Sources

  • Indra Unveils DRIZZLE Interceptor and Mother-Drone Concept for Mass C-UAS Defense

    Indra Unveils DRIZZLE Interceptor and Mother-Drone Concept for Mass C-UAS Defense

    Indra has introduced DRIZZLE, a family of autonomous effectors intended to counter mass drone attacks. The Spanish technology group presented the system at the UNVEX unmanned-systems event and described it as a compact, disposable interceptor that can operate as a hard-kill effector within a wider counter-UAS architecture.

    According to Indra and reporting by Unmanned Airspace, the interceptor is designed to exceed 400 kilometers per hour and has an approximate standalone range of 80 kilometers. The company also showed a mother-drone concept that carries several interceptors before releasing them closer to a threat area, extending the combined mission range to about 130 kilometers. These figures are vendor claims and have not been independently operationally validated.

    Indra said the interceptor uses a company-developed search and detection system to distinguish and lock onto threats. The proposed architecture allows multiple carrier aircraft and disposable effectors to be used against larger raids, while also permitting installation as a self-protection option for selected vehicles or helicopters.

    Why it matters

    The design illustrates a shift from single-target counter-drone tools toward layered systems intended for coordinated raids. Procurement teams will still need evidence on identification performance, command-and-control integration, safety constraints and cost per engagement before comparing it with other counter-UAS technologies.

    Sources