Category: News

Current, event-driven reporting, announcements and industry developments.

  • Army Laser Weapon Downs Cartel-Linked Drones on Texas Border in System’s First Confirmed Use

    Army Laser Weapon Downs Cartel-Linked Drones on Texas Border in System’s First Confirmed Use

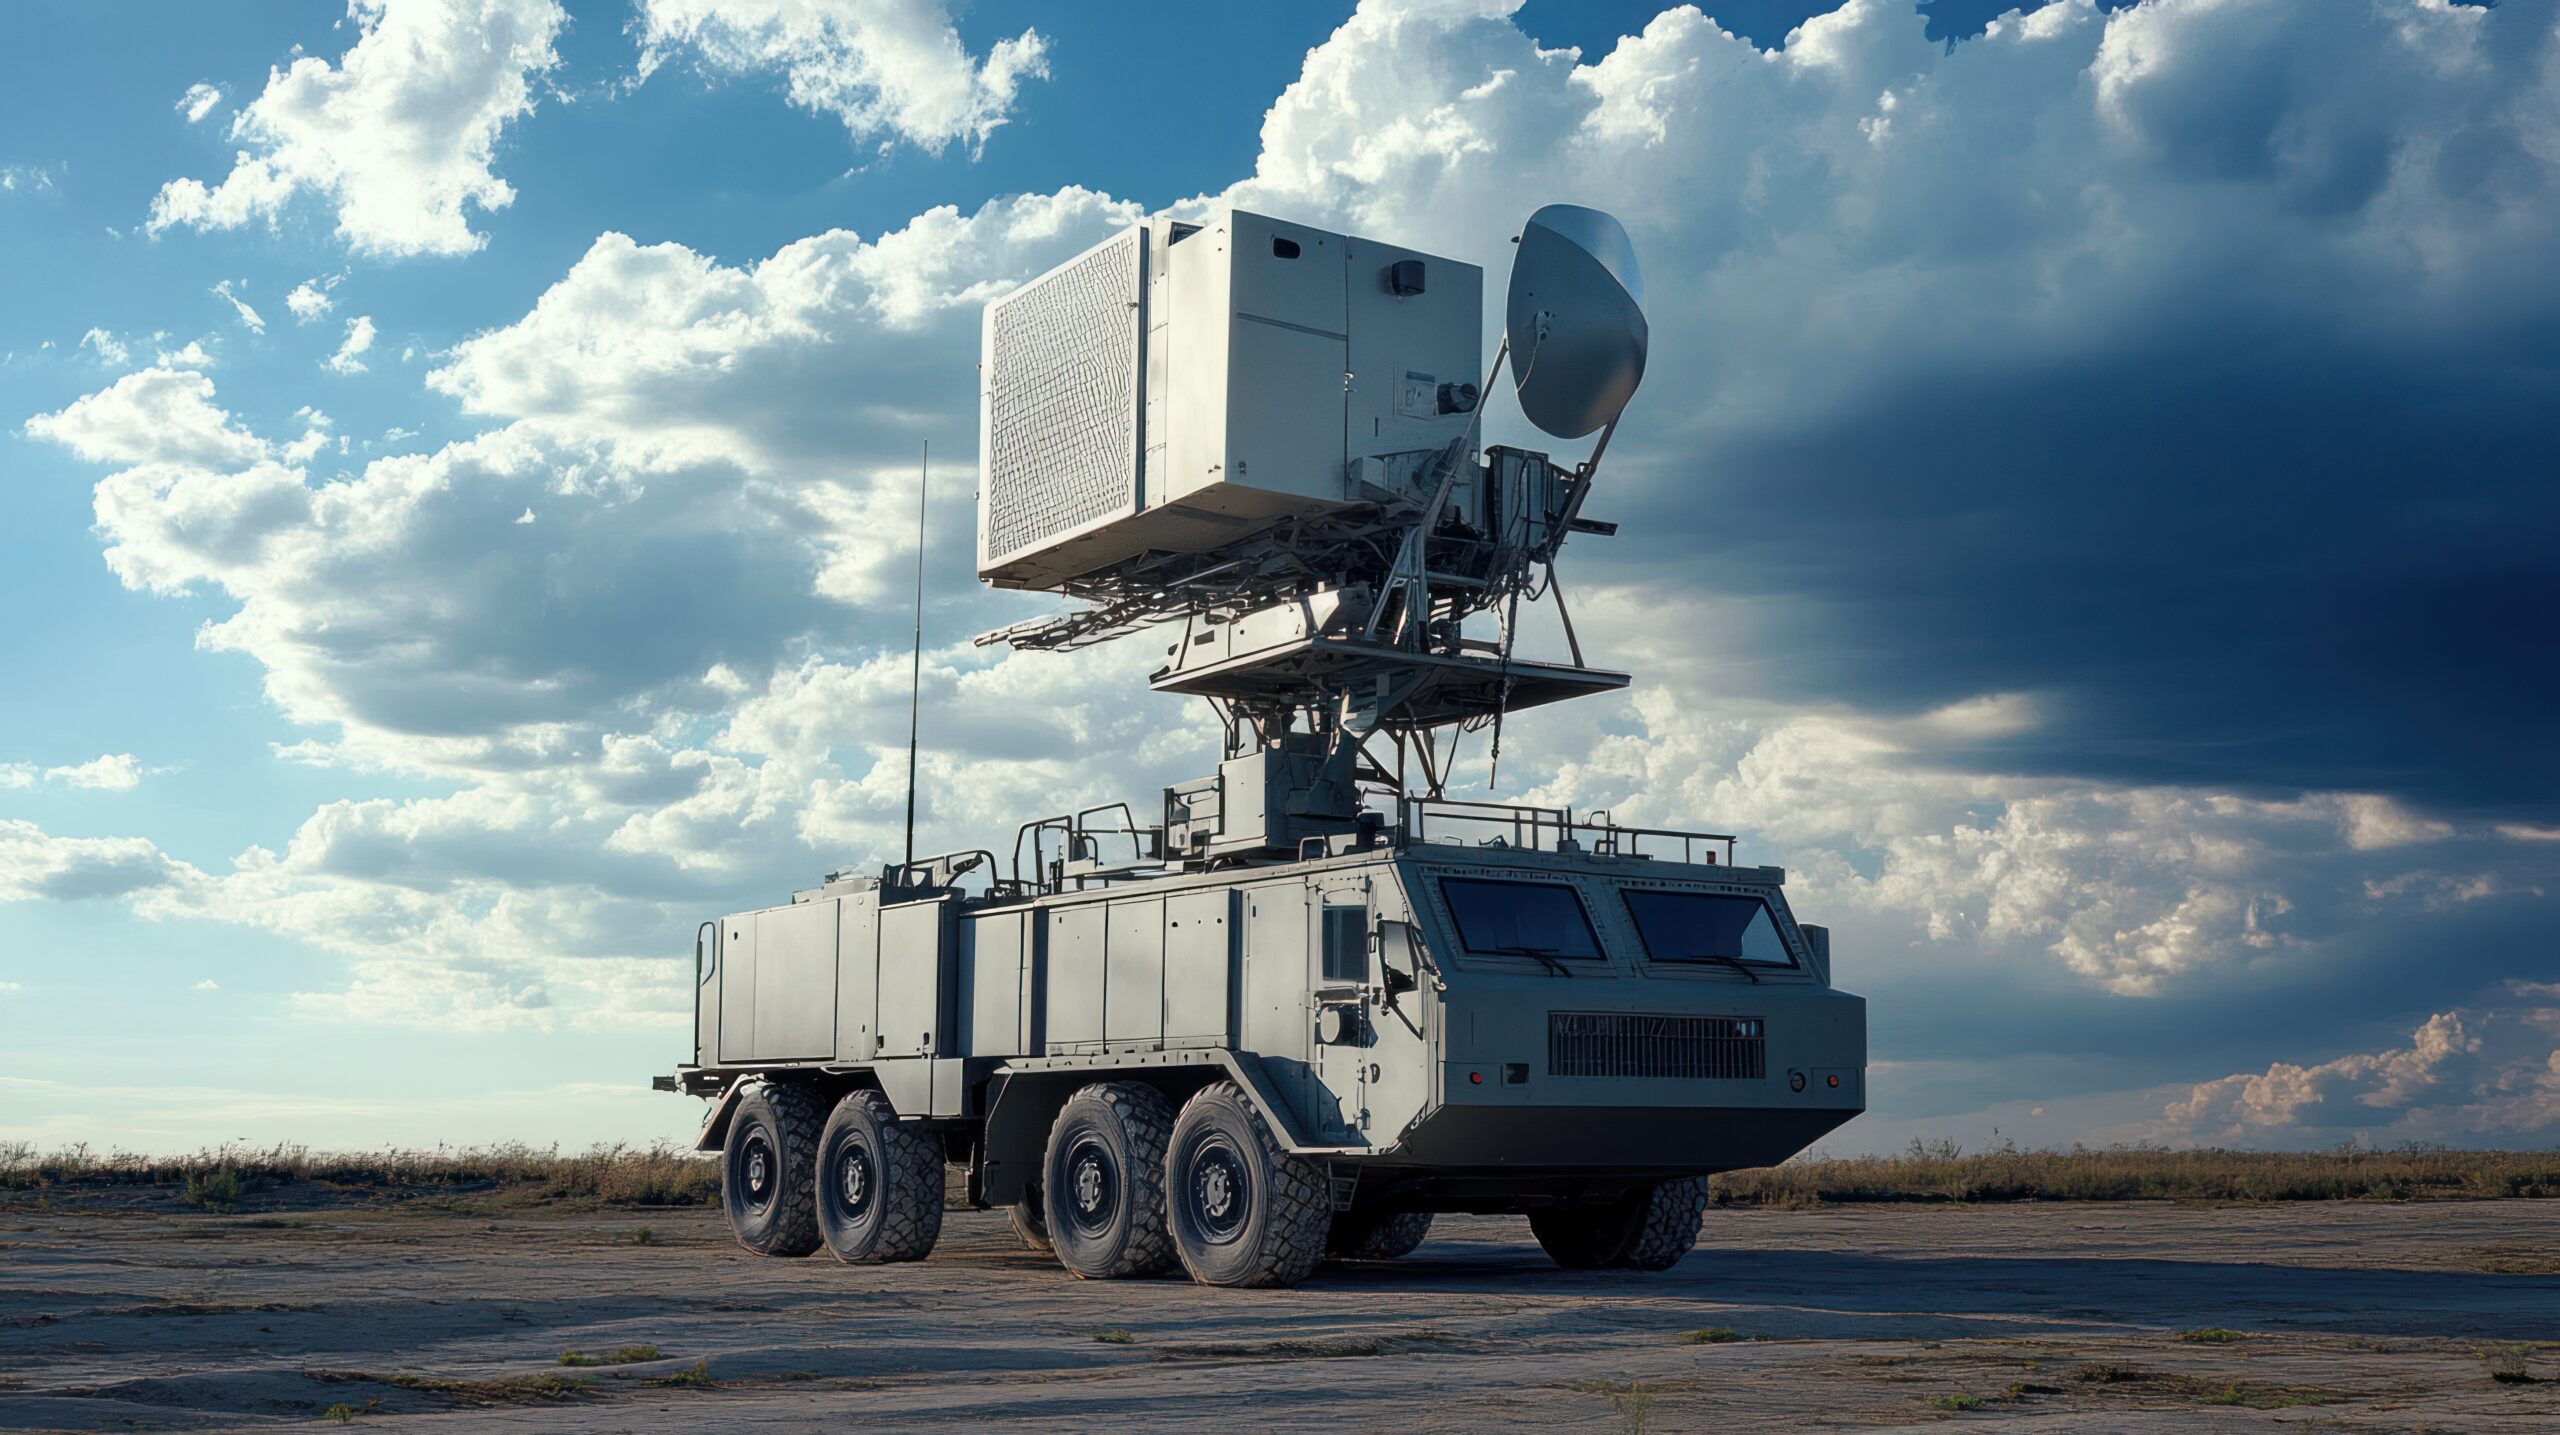
    The US Army’s Multipurpose High Energy Laser destroyed three cartel-linked drones along the Texas border over two nights, August 25 and 26, 2026, in what officials describe as the system’s first confirmed operational engagement, according to reporting from DroneXL, Unmanned Airspace, and NORTHCOM’s own statement, corroborated by AeroVironment, which confirmed one of its AMP-HEL units was involved.

    The engagements took place in airspace over or near the Rio Grande Valley in southern Texas and were carried out by Joint Task Force-Southern Border, a roughly 8,000-strong US Northern Command unit. The drones were assessed as hostile because they were operating in direct support of activity posing a physical threat to US military personnel and Customs and Border Protection partners working the area.

    Vehicle-Mounted System Produces 20 Kilowatts of Laser Power

    AMP-HEL is a vehicle-mounted directed-energy weapon capable of producing 20 kilowatts of laser power, designed for precision engagement of small unmanned aerial threats at a fraction of the cost of a traditional interceptor missile. The military did not specify the exact model variant used in the border engagements.

    The successful engagement marks a turnaround for the program, which drew criticism in February after an AMP-HEL unit mistakenly targeted the wrong drone and briefly froze operations at a commercial airport. Border-area counter-drone activity has intensified this year as cartel organizations increasingly use small unmanned aircraft for smuggling and surveillance, prompting expanded federal investment in counter-UAS testing and detection infrastructure.

  • Asheville City Council Votes to End Flock Safety Camera Contract, Remove All 11 License-Plate Readers

    Asheville City Council Votes to End Flock Safety Camera Contract, Remove All 11 License-Plate Readers

    The Asheville, North Carolina City Council voted on Tuesday, August 25, 2026, to terminate the city’s contract with license-plate reader vendor Flock Safety and remove all 11 of its cameras from city streets, according to local reporting from WLOS.

    Mayor Esther Manheimer said the decision reflected growing concerns about how Flock manages the data its cameras collect and who can access it, framing the vote as an attempt to balance public-safety utility against privacy risk. Rondell Lance, president of the local Fraternal Order of Police chapter, opposed the removal, arguing the system had given investigators an efficient way to narrow suspect vehicles by characteristics rather than manually checking every potential match.

    Part of a Wider Pattern of Contract Reviews

    Asheville’s vote follows a period of intensifying scrutiny of automated license-plate reader networks nationally, after Flock Safety itself cut its default data-retention window to seven days earlier this month in response to similar pressure. Other jurisdictions, including communities in the Chicago suburbs, have faced comparable public fights over whether to keep, expand, or cancel Flock deployments amid concerns that plate-reader data could be accessed for purposes such as immigration enforcement or unauthorized personal tracking by officers.

    Asheville’s existing contract with rival vendor Axon includes provisions for stationary license-plate readers, though none are currently installed; city officials said any future deployment would require new privacy policies to be established first.

  • TSA Unveils Horizon 25 Strategy to Modernize Checkpoints and Expand Counter-Drone Capabilities

    TSA Unveils Horizon 25 Strategy to Modernize Checkpoints and Expand Counter-Drone Capabilities

    The Transportation Security Administration launched a new strategic plan called Horizon 25 on August 24, 2026, timed to the agency’s 25th anniversary, outlining three priorities: modernizing checkpoint technology, improving the traveler experience, and hardening security across multiple transportation modes, according to TSA’s own press release and reporting from International Airport Review and Federal News Network.

    TSA Administrator David P. Cummins said the plan is intended to streamline how the agency acquires new screening technology, including next-generation scanners and biometric identity-verification systems, as well as expand TSA’s capability to detect and respond to unmanned aircraft near airports and other transportation facilities. The agency has been steadily rolling out Credential Authentication Technology 2 units, which pair document scanning with live facial comparison, as part of a broader $781 million technology-modernization program already underway.

    Gold+ Program to Be Replaced

    As part of Horizon 25, TSA said it will retire its existing Gold+ program and replace it with an evolved Screening Partnership Program, expanding the role private security contractors play in airport checkpoint operations under federal oversight. The agency framed the changes as part of a longer-term effort to reduce checkpoint friction for low-risk travelers while concentrating resources on higher-risk threats, including the small-drone threat vector that has drawn increasing federal attention this year.

    TSA said further implementation details will be worked out with field and headquarters staff in September, with the counter-UAS and technology-acquisition components expected to roll out in phases rather than all at once.

  • IBM Completes Acquisition of HRL Laboratories to Bolster Quantum Hardware Roadmap

    IBM Completes Acquisition of HRL Laboratories to Bolster Quantum Hardware Roadmap

    IBM announced on August 26, 2026, that it has completed its acquisition of HRL Laboratories, a research institution previously jointly owned by Boeing and General Motors, adding capabilities in silicon-spin qubits, quantum sensing, cryogenics, and advanced packaging to IBM’s quantum computing program, according to IBM’s own newsroom announcement and corroborating coverage from The Quantum Insider and Quantum Computing Report.

    HRL’s expertise in silicon-spin qubit fabrication is intended to complement IBM’s existing leadership in superconducting quantum computing, giving the company a second qubit modality to draw on as it pursues a multi-modality hardware roadmap. HRL’s silicon fabrication processes are expected to be integrated into Anderon, IBM’s dedicated quantum wafer foundry established earlier this year.

    Boeing and GM Retain a Role in Quantum Applications

    Boeing and General Motors, HRL’s former joint owners, will continue to partner with IBM and HRL on quantum applications and advanced technology development following the deal’s close, according to IBM’s announcement. The acquisition adds to a broader wave of consolidation and infrastructure investment in quantum computing this year, as government agencies and large technology firms compete to move quantum systems from research labs toward practical, fault-tolerant deployment.

    Financial terms of the acquisition were not disclosed. IBM said HRL’s quantum-sensing and materials-science capabilities, beyond qubit fabrication, are also expected to strengthen its broader hardware development pipeline.

  • Critical Gitea Flaw Under Active Exploitation as Thousands of Servers Remain Unpatched

    Critical Gitea Flaw Under Active Exploitation as Thousands of Servers Remain Unpatched

    A critical vulnerability in Gitea, a widely used self-hosted Git service, is being actively exploited to plant cryptocurrency-mining malware on unpatched servers, according to reporting from The Hacker News and BleepingComputer published August 26 and 28, 2026, and confirmed by vulnerability-tracking service Shadowserver.

    The flaw, tracked as CVE-2026-60004 and carrying a CVSS score of 9.8, allows an attacker with ordinary write access to a repository to execute arbitrary shell commands as the Gitea service account by submitting a malicious patch through the platform’s diffpatch API endpoint. Because Gitea’s default configuration permits open account registration, an unauthenticated attacker can obtain the necessary write access simply by creating an account and a repository, then trigger code execution — researcher Shai Rod (NightRang3r), who is credited with the discovery, described exploitation as achievable in seconds on a default install with zero prior credentials.

    Cryptominer Payloads Observed, CISA Deadline Already Passed

    Shadowserver identified more than 8,300 internet-exposed, vulnerable Gitea instances as of August 27, 2026. The US Cybersecurity and Infrastructure Security Agency added the flaw to its Known Exploited Vulnerabilities catalog on August 25 and ordered Federal Civilian Executive Branch agencies to patch by August 28. In at least one documented case, a developer’s Gitea instance was compromised by a dropper that cleared environment variables, killed competing processes, and fetched an architecture-specific cryptominer payload before deleting itself — consistent with opportunistic, automated scanning rather than a targeted campaign.

    The vulnerability affects all Gitea versions from 1.17 onward and is fixed in version 1.27.1. Organizations running self-hosted Gitea instances, particularly those with open registration enabled, are advised to patch immediately and review recent repository and account activity for signs of compromise.

  • Waymo Names Munich as Its Third City Outside the US for Driverless Ride-Hailing

    Waymo Names Munich as Its Third City Outside the US for Driverless Ride-Hailing

    Waymo announced on August 28, 2026, that Munich will become its third international city for autonomous ride-hailing, following earlier expansions to London and Tokyo, according to reporting from Euronews. The company said it is laying the operational and regulatory groundwork for a driverless service in the German city but has not set a specific public launch date.

    Waymo pointed to safety data from its US operations to make the case for expansion, citing internal analysis suggesting its autonomous vehicles are involved in significantly fewer serious-injury and fatal crashes per mile than human-driven taxis in the same markets. The company noted that Europe records roughly 20,000 road fatalities annually, with driver error cited as a factor in a majority of crashes, as part of its rationale for prioritizing European expansion.

    Part of a Broader European Push for Autonomous Driving

    The Munich announcement comes as European regulators show growing openness to autonomous and driver-assistance systems more broadly; a recent Dutch approval of Tesla’s Full Self-Driving Supervised system has been followed by similar regulatory movement in Denmark, Lithuania, and Estonia. Waymo already operates fully driverless commercial service across ten US cities, where the company has said it now completes more than half a million paid trips per week.

    Munich’s position as a major automotive-engineering hub, home to BMW and a dense supplier base, is likely to shape how quickly Waymo can secure local regulatory approval and testing partnerships. The company has not disclosed which German authorities it is engaging with or a target timeline for public rides to begin.

  • Hasbro Notifies Employees That Social Security and Financial Data Was Exposed in Cyberattack

    Hasbro Notifies Employees That Social Security and Financial Data Was Exposed in Cyberattack

    Toy and game maker Hasbro has begun notifying current and former employees that a cyberattack exposed their personal and financial information, according to breach notification letters filed with state regulators, including the Massachusetts Attorney General’s Office on August 28, 2026, and reported by BleepingComputer.

    The exposed data varied by individual but could include Social Security numbers, financial account information, credit and debit card numbers, driver’s license details, names, email addresses, and phone numbers. The Massachusetts filing alone identifies 436 affected employees in that state; the total number of individuals notified nationwide was not disclosed in the filing reviewed by BleepingComputer.

    Response and Unresolved Questions on Scope

    Hasbro said it “implemented containment and remediation measures, including disabling the compromised employee account, terminating unauthorized access, and deploying additional safeguards,” and is offering affected individuals complimentary identity-protection services. The company said it has “no indication” the exposed information has been misused.

    Hasbro separately disclosed a cyberattack detected on March 28, 2026, that forced systems offline and contributed to an estimated $25 million in lost revenue during the resulting disruption; the company’s current employee-data notification does not formally confirm whether the two incidents are connected, and BleepingComputer’s reporting treats the link as unconfirmed. The disclosure adds Hasbro to a lengthening list of large employers notifying staff of breach exposure this year, following similar notifications from healthcare and logistics firms including McKesson’s disclosure of a ShinyHunters-linked breach earlier this week.

  • Virginia Tech Opens Counter-UAS Testing and Research Center Backed by $5 Million Army Futures Command Award

    Virginia Tech Opens Counter-UAS Testing and Research Center Backed by $5 Million Army Futures Command Award

    Virginia Tech held a ribbon-cutting ceremony on August 28, 2026, for a new Counter-UAS Testing and Research Center at its Kentland Farms property in Blacksburg, Virginia, a facility the university’s National Security Institute says will support development of drone-defense technology for both the US Army and civilian critical-infrastructure operators, according to Virginia Tech News and local coverage from WSLS.

    The outdoor site is backed by a $5 million award from the US Army Futures Command’s Combat Capabilities Development Command C5ISR Center and gives researchers a real-world, open-air environment to test detection, tracking, and identification systems against unmanned aircraft — complementing indoor and virtual test environments the university already operates. University President Tim Sands, US Senator Mark Warner, and 9th District Congressman Morgan Griffith attended the opening.

    Officials Cite a Capability Gap

    “This is an area where we have to catch up, where America is behind,” Warner said at the ceremony. Austin Phoenix, director of mission systems at the Virginia Tech National Security Institute, said unmanned aircraft present a distinct detection challenge “because they’re just much smaller” than the aerial threats legacy air-defense systems were designed around.

    The center is intended to provide independent verification and validation testing for both government and private-industry counter-UAS systems, adding to a small number of dedicated outdoor test ranges nationally as drone incursions over military installations, airports, and other sensitive sites continue to draw federal attention. Virginia was one of seven states granted early federal UAS test-site designation roughly twelve years ago, giving the university a long-running base of aviation-research infrastructure to build on. The opening follows a string of counter-drone contract awards this year, including DHS’s department-wide counter-drone contracts.

  • ServiceNow Patches Three Maximum-Severity Flaws That Allowed Unauthenticated Code Execution

    ServiceNow Patches Three Maximum-Severity Flaws That Allowed Unauthenticated Code Execution

    ServiceNow disclosed and patched three maximum-severity vulnerabilities in its Now Platform and AI Platform on August 28, 2026, each exploitable by an unauthenticated attacker with low complexity and no user interaction, according to the company’s own security advisories and reporting from BleepingComputer and The Hacker News.

    Two of the flaws, CVE-2026-18885 and CVE-2026-18886, are code-injection vulnerabilities in the ServiceNow AI Platform that could let an attacker execute arbitrary code, access or modify instance data beyond intended permissions, or escalate privileges. A third, CVE-2026-74820, is a SQL-injection flaw in the same platform that could allow an unauthenticated user to run arbitrary SQL statements against the underlying database and alter instance data. A separate, high-severity sandbox-escape bug, CVE-2026-6876, was disclosed alongside the three critical issues.

    No Confirmed Exploitation, but a Pattern of Prior Abuse

    ServiceNow said it is “not currently aware of malicious exploitation against ServiceNow instances” tied to the newly disclosed flaws. The company has hosted-instance customers already patched, while partners and self-hosted customers running on-premises deployments are responsible for applying fixes themselves across the affected Xanadu, Yokohama, Zurich, and Aspen release families.

    The disclosure follows a related ServiceNow flaw, CVE-2026-6875, that researchers confirmed was actively exploited in July 2026, and echoes a pattern from 2024 in which several ServiceNow vulnerabilities were chained together in attacks against government and private-sector targets. Given ServiceNow’s widespread use for enterprise workflow and identity-adjacent processes, security teams are advised to prioritize patching self-hosted instances even in the absence of confirmed in-the-wild exploitation.

  • Iran-Linked Hackers Disable UK Power Plant for Four Days as US Water Utilities Report Coordinated Attacks

    Iran-Linked Hackers Disable UK Power Plant for Four Days as US Water Utilities Report Coordinated Attacks

    A small power generation facility in the United Kingdom was disabled for four days after a suspected Iran-linked cyberattack, in a window that overlapped with a wider wave of intrusions against wastewater treatment plants across roughly a dozen US states, according to reporting from Security Affairs and The Register published August 23–24, 2026, citing UK government and industry sources.

    The UK facility, not named publicly for security reasons, was small enough that its outage did not affect the wider national power supply, and staff were able to restore operations without formal notification thresholds being triggered. A UK government source told reporters the plant fell below the legal reporting threshold for “important generators,” while the National Cyber Security Centre declined to comment on the specific incident. NCSC chief Richard Horne said in June that the agency had handled more than 200 attacks on UK critical national infrastructure over the preceding year.

    US Wastewater Plants Hit Across Multiple States

    In parallel, US authorities traced a separate series of intrusions affecting dozens of wastewater treatment facilities, with the earliest reports emerging from Minnesota on July 26 and subsequent incidents confirmed in Michigan, Georgia, South Dakota, New Jersey, and Alabama. Several affected utilities reported flooding and loss of water pressure, and some jurisdictions issued boil-water advisories as a precaution. The FBI has attributed the water-sector intrusions to “malicious cyber actors,” and US government sources cited by Security Affairs indicated the activity likely originated in Iran.

    Researchers characterize both incidents as capability demonstrations rather than attempts to cause lasting damage, consistent with a broader pattern of suspected Iranian probing reported in recent months against infrastructure operators in Germany, Poland, Finland, Belgium, and Albania. UK officials have said the activity has accelerated since February airstrikes involving the United States and Israel against Iranian targets.

    The incidents add to a year in which operational technology at water and wastewater facilities has faced sustained scrutiny, and follow a separate US executive action restricting foreign-made equipment in bulk-power systems over cybersecurity concerns.