Biometric access control has moved from a specialist technology into a mainstream option for offices, data centers, airports and critical infrastructure sites. But “biometrics” is not one technology — fingerprint, iris, facial and vein-pattern recognition each rely on different physical traits, different sensors and different deployment trade-offs. Choosing the right modality, or combination of modalities, depends heavily on the environment, the threat model and how the system will be used day to day.
Fingerprint Recognition
Fingerprint readers remain the most widely deployed biometric modality because the sensors are inexpensive, compact and familiar to users from consumer smartphones. Most systems capture a digital image of the fingerprint ridge pattern and extract minutiae points — the specific locations where ridges end or split — to build a template for matching, rather than storing the raw image. Fingerprint readers perform well in controlled indoor environments but can struggle with dirty, wet, gloved or worn fingertips, which is a common consideration for industrial and outdoor sites.
Iris Recognition
Iris recognition captures the intricate pattern in the colored ring around the pupil using a near-infrared camera, converting the pattern into a mathematical template. Because the iris pattern is highly detailed and stable over a person’s lifetime, iris systems are often used where very high assurance is required, such as border control, data centers and other high-security facilities. Iris cameras typically require the user to look toward the sensor within a defined distance, which makes enrollment and enforcement more deliberate than a simple badge tap.
Facial Recognition
Facial recognition systems map geometric features of the face, or increasingly use deep-learning models to generate a numerical embedding of the face, and compare that embedding against enrolled templates. The major advantage of facial recognition for access control is speed and convenience: many systems can identify an authorized person without requiring them to touch a sensor or stop moving, which supports high-traffic entrances and touchless access goals. Accuracy can be affected by lighting conditions, camera angle, face coverings and image quality, and the technology has also drawn regulatory and public scrutiny over data protection and consent, which organizations need to factor into deployment plans.
Vein Pattern Recognition
Vein recognition, most commonly implemented as finger-vein or palm-vein scanning, uses near-infrared light to image the pattern of veins beneath the skin’s surface, since deoxygenated blood in veins absorbs infrared light differently than surrounding tissue. Because the vein pattern sits inside the body rather than on an exposed surface, it is difficult to capture or replicate without the cooperation of a live subject, which makes vein recognition attractive for high-security financial and data center environments concerned about spoofing. The trade-off is that vein scanners are typically more expensive than fingerprint or facial recognition hardware and are less commonly integrated into general-purpose access control platforms.
Choosing the Right Modality
In practice, the choice between modalities usually comes down to a handful of operational questions: How much throughput does the entrance need to support? Will users wear gloves, masks or personal protective equipment on site? Is the environment indoors and climate-controlled, or exposed to dirt, moisture and temperature swings? And what level of assurance does the asset being protected actually require? Many organizations end up deploying more than one modality across a site — for example, facial recognition for high-traffic general entrances and iris or vein recognition for a smaller number of high-security zones such as server rooms or vaults.
Privacy and Data Protection Considerations
Because biometric data is permanently tied to an individual and cannot be reset the way a password or badge can, organizations deploying any of these modalities need a clear policy for how templates are stored, encrypted, and eventually deleted, along with a legal basis for collecting biometric data that satisfies applicable regional privacy laws. Storing a mathematical template rather than a raw image, and keeping that template on a secure local device rather than in a shared cloud database, are common practices for reducing the impact of a potential breach.
The National Highway Traffic Safety Administration (NHTSA) has opened an Audit Query, numbered AQ26002, into the technical data and process Tesla used to self-certify that its new Cybercab complies with all applicable Federal Motor Vehicle Safety Standards (FMVSS), according to an NHTSA press release and reporting by the New York Times and Electrek. The investigation, opened September 3, 2026, covers an estimated 1,000 Cybercab vehicles and was prompted by public information, according to the filing.
A Vehicle With No Manual Controls
Cybercab has no steering wheel or pedals, and Tesla began putting paying passengers in the vehicles in Austin, Texas the same day the audit was opened. NHTSA said it will examine “the extent to which Tesla’s certification depended on determinations that certain FMVSS are inapplicable to the Cybercab,” according to Electrek, focusing on whether standards written for vehicles with traditional human controls can be validly waived for a fully autonomous design.
How Self-Certification Works
Under the US system, automakers certify their own compliance with federal safety standards rather than obtaining pre-approval from regulators, with NHTSA auditing that certification after the fact. The audit will assess the technical data and processes underlying Tesla’s compliance determination and how occupant protection is addressed in a vehicle operating without a human driver behind physical controls, according to NHTSA.
Stakes for Tesla’s Robotaxi Rollout
Tesla has said it plans to gradually expand Cybercab deployment to more vehicles and locations. The outcome of the audit could influence the pace of that expansion and is being closely watched as a test case for how federal vehicle safety standards, largely written around human-operated cars, apply to commercially deployed vehicles with no manual controls at all.
Nvidia has agreed to acquire open-source artificial intelligence platform Hugging Face for approximately $12.9 billion, according to CNBC, the Wall Street Journal and the BBC. The deal, confirmed on September 3, 2026, is Nvidia’s second-largest acquisition after its roughly $20 billion purchase of Groq’s assets late last year, and marks one of the chipmaker’s biggest moves yet to expand beyond hardware and further up the AI software stack.
Deal Terms and Scale
Under the agreement, Nvidia will pay about $11.9 billion to Hugging Face investors and offer up to $1 billion in stock-based incentives to employees who join the company, according to the BBC. Hugging Face is used by more than 18 million developers and hosts more than three million AI models, with over 200,000 companies using the platform to discover and deploy AI, the companies said.
Nvidia Pledges to Keep the Platform Open
Nvidia CEO Jensen Huang said in a blog post that the companies will “scale Hugging Face’s platform, strengthen its infrastructure and expand access to AI for developers and institutions worldwide,” and that Hugging Face will remain an open platform for the broader AI ecosystem rather than being tied exclusively to Nvidia chips or services, according to CNBC.
Why It Matters for the AI Ecosystem
The acquisition comes as Nvidia works to counter the rapid rise of open-weight models developed in China, which pose a growing competitive challenge to leading US AI companies, according to the Wall Street Journal. Industry observers noted the deal could be read either as a consolidation risk for an independent hub of open AI development, or, if Nvidia keeps its commitment to openness, as a boost to smaller developers and startups that rely on Hugging Face’s tooling and model hosting.
A federal rule that would give trained state, local, tribal and territorial (SLTT) law enforcement and correctional agencies formal authority to detect, track, disable or seize threatening drones closes for public comment on September 6, 2026, according to DRONELIFE. The Interim Final Rule, published by the Department of Homeland Security (DHS) and Department of Justice (DOJ), is the first detailed implementing regulation for counter-unmanned aircraft system (C-UAS) powers created under the SAFER SKIES Act, part of the FY2026 National Defense Authorization Act.
Certification, Training and Two Approved-Systems Lists
The rule sets out training and certification requirements, reporting procedures and operational safeguards for agencies seeking to conduct counter-drone operations against credible threats to public safety, critical infrastructure, correctional facilities or major public events. It also establishes an Authorized Technologies List and a more specific Authorized Systems List, both to be maintained through the FBI’s Law Enforcement Enterprise Portal, identifying which categories and specific counter-UAS products agencies may lawfully deploy.
FCC Actions Address Spectrum and Legal Liability
Alongside the DHS/DOJ rule, the Federal Communications Commission issued four coordinated actions intended to remove practical barriers to deployment. These include a 180-day blanket Special Temporary Authority letting eligible agencies operate approved counter-UAS systems while longer-term licensing is developed, an equipment-authorization waiver allowing manufacturers to sell approved radio-frequency systems to qualified agencies sooner, and declaratory rulings clarifying that SLTT personnel acting under the Act’s oversight can receive derivative immunity from Section 333 of the Communications Act, which otherwise prohibits interference with licensed radio communications.
Guardrails Remain in Place
The frameworks do not authorize unrestricted counter-drone activity. Agencies must still meet federal certification requirements, use only systems on the Authorized Systems List, follow operational restrictions written into the SAFER SKIES Act, and report qualifying mitigation actions to federal authorities. With the comment period closing today, stakeholders across the public safety, drone and counter-UAS industries have had a final opportunity to weigh in before the rule is finalized.
German video security specialist Geutebrück is entering a new corporate phase after receiving a majority investment from IBEX Wachstumspartner, alongside European AI group Merantix Momentum, according to Security Info Watch and confirmed by law firm Schmitz Knoth, which advised Geutebrück’s shareholders on the transaction. The deal closed on August 31, 2026.
New Leadership and International Ambitions
As part of the transition, Tobias Huemmerich will take over management of the company, with plans to further internationalize the business and expand its customer offering, according to Security Middle East. Geutebrück has operated in the video security market for more than 55 years and has built a reputation as a provider of video management software and hardware for public-sector and highly critical infrastructure clients.
Merantix Momentum Brings AI Expertise
Merantix Momentum, described as Europe’s leading AI group, is joining the investment specifically to help Geutebrück develop new AI-based applications, according to the companies. Geutebrück has said it sees opportunities to extend its video management platform beyond traditional security use cases, including the potential use of anonymized video data to identify workflow efficiencies and improve occupational safety.
Part of a Broader Consolidation Trend
The investment adds to a string of ownership changes across the video surveillance sector as manufacturers seek capital and AI expertise to keep pace with larger competitors. IBEX Wachstumspartner, an owner-managed investment firm focused on succession situations at German medium-sized businesses, said the deal reflects its strategy of pairing growth capital with digitalization expertise for established technology companies entering a generational transition.
OpenAI is committing $1 billion to subsidize access to its cyber-capable AI models for critical infrastructure defenders and launching a center to train security professionals in the U.S. public sector, as part of an expansion of its Daybreak program, the company said.
What’s New
The Daybreak Defense Network will provide subsidized AI cyber capabilities, training and technical assistance, though OpenAI has disclosed few details about specific costs or eligibility criteria. The company has selected HackerOne as one of a limited group of cybersecurity vendors with early access to its frontier cyber capabilities through the network. OpenAI co-founder Greg Brockman has separately published a blog post describing the use of AI agents to find and fix security vulnerabilities.
Why It Matters
“There are a large amount of people and organizations that want to uplevel their security, but they don’t know how,” Brockman said, adding that without broader adoption of AI-assisted defense, “it’s possible we can expect critical infrastructure outages as part of normal life.” The pledge follows a separate letter signed by OpenAI, Anthropic, Google, Microsoft and more than 100 other companies calling for coordinated industry defense against AI-driven cyber threats, and reflects a wider push by frontier AI labs to position their models as tools for under-resourced defenders in sectors like water, energy and healthcare.
September 4, 2026 — NAPCO Security Technologies has released Prima v8, a redesigned mobile app for its Prima self-contained smart security systems. The update adds revised security controls, biometric authentication, expanded notification settings and an Apple Watch companion app.
What Changed in Prima v8
The new version reorganizes navigation and rebuilds core workflows for arming, device control and account management. Security screens provide clearer entry and exit countdowns, alarm details and sensor status information. Users can also manage connected lights, locks, garage doors, water valves and thermostats from the app.
NAPCO says existing users can install the update without creating a new account or re-pairing their system devices. Credentials, configurations and device pairings are intended to carry over. The Apple Watch companion app supports arming and disarming from the watch, while revised settings give users more control over push, email and SMS notifications.
Why It Matters
Residential and small-commercial security platforms increasingly combine alarm status, connected-device control and account administration in one mobile interface. A clearer workflow can reduce routine friction for users and installers, but app convenience does not replace professional system design, reliable communications or an appropriate alarm-response plan.
The release follows the wider shift toward software-led management of intrusion and connected-building systems. For background on the underlying sensors and control architecture, see SectechMedia’s guide to intrusion detection and alarm systems.
A September 2 webinar hosted by the Fiber Optic Sensing Association (FOSA) put a spotlight on a shift already underway in how Distributed Temperature Sensing (DTS) is used across energy infrastructure: from a technology that simply reports temperature to one that feeds directly into decisions about capacity, maintenance, and risk.
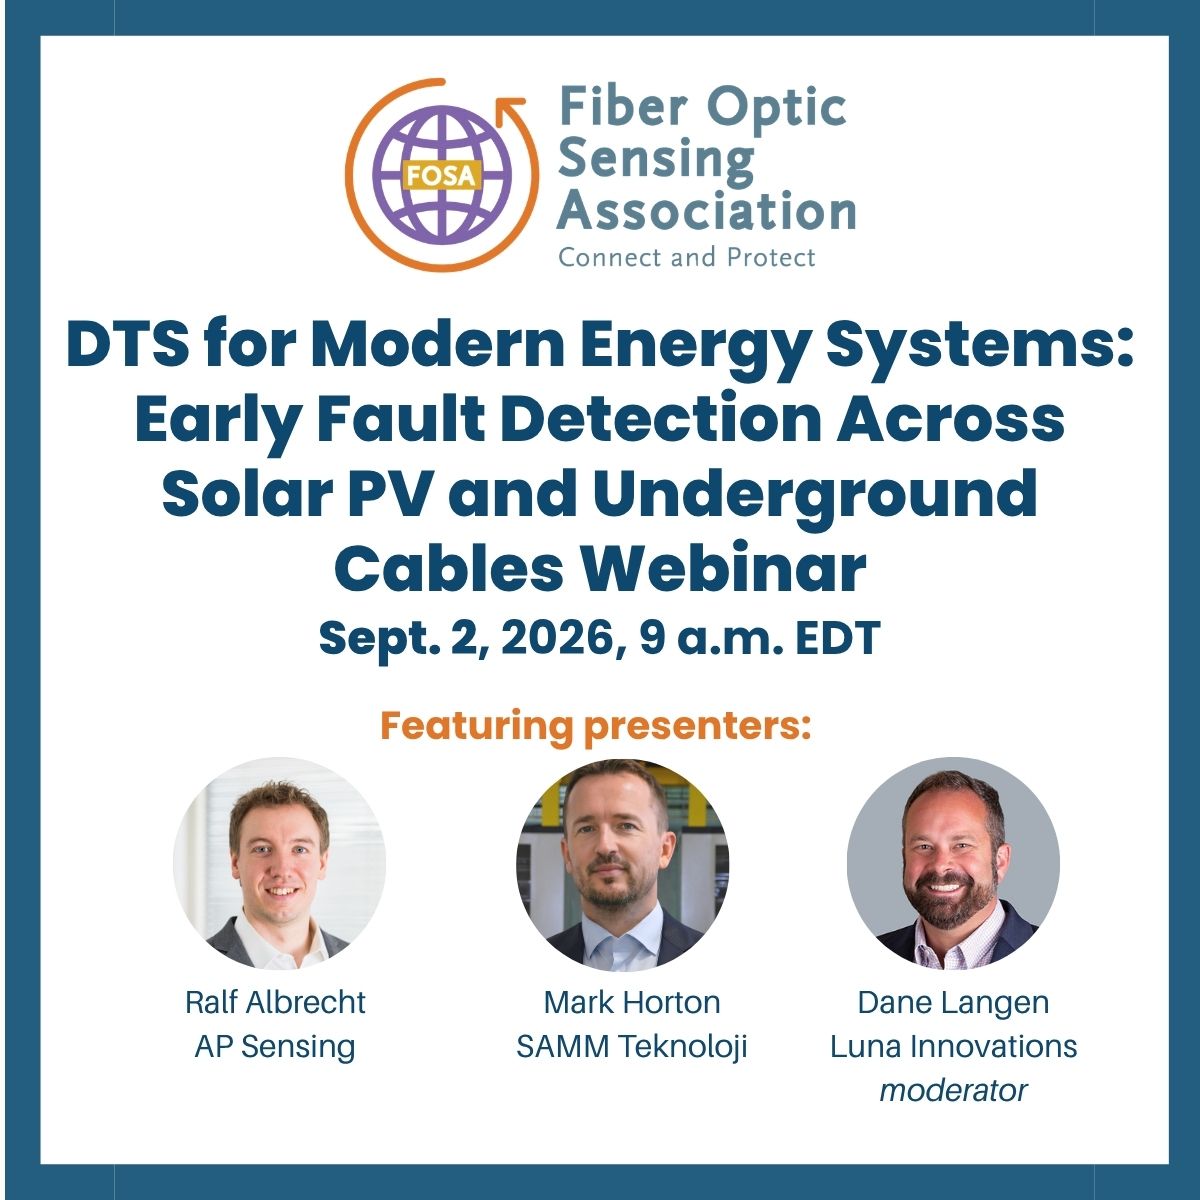
Titled “DTS for Modern Energy Systems: Early Fault Detection Across Solar PV and Underground Cables,” the session paired two speakers working on opposite ends of the power system. Ralf Albrecht of AP Sensing covered underground transmission and distribution cables, focusing on how DTS data can support dynamic cable ratings. Mark Horton, International Operations Director at SAMM Technology, addressed solar PV and battery energy storage systems (BESS), where the priority is catching abnormal heating before it becomes a fire or an outage. Dane Langen of Luna Innovations moderated on FOSA’s behalf.
The premise both speakers returned to: the energy transition isn’t just adding renewable capacity, it’s changing how that capacity behaves. More solar generation, larger installations, high-capacity underground cable runs, and a growing base of BESS assets all add variability that traditional inspection methods struggle to track continuously.
Thermal cameras, drone surveys, and periodic site visits remain useful, but each one captures a single moment in time. A loosening connector or a slowly warming cable section can develop in the days between inspections and go unnoticed until the next scheduled check.
DTS addresses that gap differently: instead of a handful of fixed sensors, the optical fiber itself becomes the sensing element along its entire length. Laser pulses sent through the fiber generate backscattered light that, when analyzed, yields a temperature reading roughly every meter, over distances up to about 50 kilometers on a single system. The practical effect is a continuous thermal map of an asset rather than scattered data points.
Underground Cables: From Fixed Limits to Real-Time Capacity
Albrecht’s presentation reframed DTS as more than a fault-detection tool for buried cables — it’s also a lever for getting more usable capacity out of existing infrastructure.
Cable operators set maximum current limits based on conductor temperature, since excess heat accelerates insulation aging and raises failure risk. The issue, as Albrecht explained, is that standard Static Cable Rating calculations tend to assume worst-case conditions — high soil thermal resistivity and similar conservative inputs — baked in at the design stage. Real operating conditions are frequently better than those assumptions, meaning a cable’s actual safe capacity can exceed its official rating.
Real-Time Thermal Rating (RTTR), also called Dynamic Cable Rating (DCR), replaces some of those fixed assumptions with live data. DTS temperature readings are combined with current electrical load, soil conditions, and thermal models built on IEC and CIGRE methodologies to estimate actual conductor temperature — not just the temperature around the cable — and from that, how much current it can carry safely right now. Albrecht described systems that go a step further, projecting dynamic or emergency ratings 24, 48, or 72 hours out.
That turns a static design question (“what was this cable rated for?”) into an operational one (“what can it carry today?”) — a distinction Albrecht suggested matters more as renewable-driven load patterns become less predictable. In some cases, unlocking that extra headroom on existing cable routes could reduce or delay the need for new transmission builds.
One technical wrinkle Albrecht flagged: the sensing fiber isn’t always physically adjacent to the conductor. It may sit within the cable structure, be strapped to it, or run through a nearby duct, and heat takes time to travel from the conductor to wherever the fiber actually measures. He pointed to field examples — including 33 kV double-circuit installations with fiber positioned at varying distances from the cable — to illustrate why DCR systems need thermal modeling layered on top of raw DTS readings, rather than treating the fiber’s temperature as a direct stand-in for the conductor’s.
Albrecht also touched on overhead lines, where wind cooling — not soil conditions — governs safe current limits. Fiber inside an Optical Ground Wire (OPGW) can’t read conductor temperature directly, but he noted that Distributed Acoustic Sensing (DAS) can analyze vibration patterns in the same fiber to infer wind conditions relevant to Dynamic Line Rating (DLR) calculations — a reminder that DTS and DAS running on infrastructure that already carries fiber can extend well beyond their original design purpose.
Solar PV: Catching the Problem Before the Fire
Horton’s presentation shifted the discussion to a different failure mode. In solar PV and BESS installations, the goal isn’t optimizing capacity — it’s catching abnormal heat before it turns into equipment damage, downtime, or fire.
He listed several common hotspot sources: loose electrical connectors, damaged DC cabling, installation defects, rodent damage, aging components, and rising resistance at connections over time. Left undetected, any of these can escalate from a minor thermal anomaly into a serious failure. The core distinction Horton drew was between detecting a fire and detecting the conditions that lead to one — the earlier the anomaly surfaces, the more room maintenance teams have to intervene.
Drone thermography, he noted, has real value but the same limitation as underground-cable inspections: it’s a snapshot. A connector that starts failing a week after a drone flight stays invisible until the next flight. Routing sensing fiber across a site — from the backs of modules to combiner boxes, inverters, transformers, AC/DC cabling, BESS units, and grid-connection equipment — turns that into continuous coverage instead. Because fiber doesn’t carry current or pick up electromagnetic interference, it’s also well suited to sitting close to high-voltage equipment.
Solar sites present their own complication for alarm design: normal temperatures already swing widely with sun angle, ambient conditions, cloud cover, and season, so a single fixed threshold generates excessive false alarms. Horton described layering three approaches instead — absolute maximum-temperature thresholds, rate-of-rise detection for unusually fast heating, and trend/baseline comparisons that flag when a specific asset starts behaving differently from its own historical pattern. That combination is what turns DTS from a long thermometer into an actual condition-monitoring input.
He also addressed a less glamorous but practical question: fiber survives decades of module swaps, repairs, and maintenance work by being secured behind panels with UV-resistant ties (movable when a module is replaced) and by leaving service loops of spare fiber for future splicing. Depending on a system’s optical budget, a single channel can typically absorb somewhere around 10 to 15 splices before a longer section needs replacing outright — a detail that matters for a sensing system expected to remain functional for the life of the asset.
Two Problems, One Underlying Shift
Albrecht and Horton were solving different problems — maximizing safe throughput on kilometers of buried cable versus catching a localized hotspot on a solar module or battery unit — but both talks pointed to the same underlying change: replacing periodic, point-based checks with continuous, distributed measurement.
The broader theme of the session was that DTS data is increasingly being wired into other systems — thermal models, DCR platforms, SCADA, alarm logic, and maintenance workflows — rather than reviewed in isolation. In cable networks, that can mean determining whether extra transmission capacity is genuinely available. In solar and storage assets, it can mean flagging a developing problem early enough to act on it. Across both applications, the fiber itself is being asked to do more than sense temperature — it’s becoming an input to real operating decisions.
This article is based on a summary account of FOSA’s September 2, 2026 webinar “DTS for Modern Energy Systems: Early Fault Detection Across Solar PV and Underground Cables,” featuring presentations from Ralf Albrecht (AP Sensing) and Mark Horton (SAMM Technology), moderated by Dane Langen (Luna Innovations). FOSA typically posts recordings of its webinars to its public archive after the fact; readers seeking the full session, including technical Q&A, should check FOSA’s website directly.
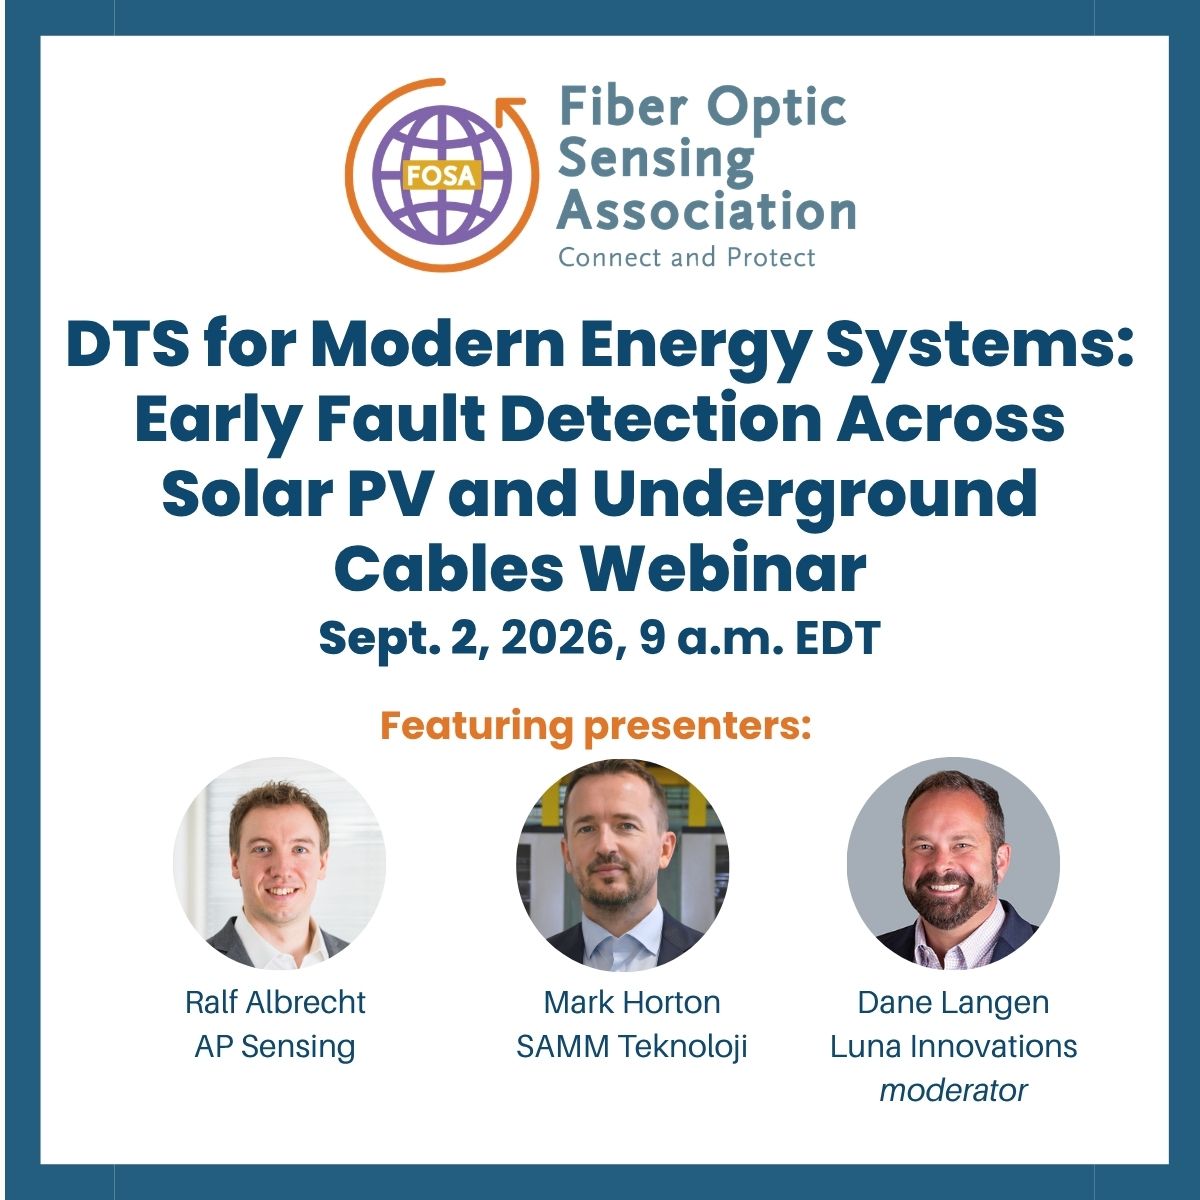
SAMM Technology (SAMM Teknoloji İletişim A.Ş.) is taking part in an upcoming webinar hosted by the Fiber Optic Sensing Association (FOSA), addressing how Distributed Temperature Sensing (DTS) can support early fault detection across solar photovoltaic (PV) installations and underground power cable networks.
The webinar, titled “DTS for Modern Energy Systems: Early Fault Detection Across Solar PV and Underground Cables,” takes place on September 2, 2026, at 9:00 AM EDT (13:00 UTC), hosted online via Zoom by FOSA, the US-based non-profit industry association focused on advancing distributed and quasi-distributed fiber optic sensing technologies.
SAMM Technology on the Panel
Representing SAMM Technology, Mark Horton, the company’s International Operations Director, joins the session alongside Ralf Albrecht of AP Sensing, with Dane Langen of Luna Innovations moderating. According to FOSA’s own event announcement, the panel will discuss how DTS technology is being applied to monitor modern energy infrastructure, with a focus on practical approaches to early fault detection in solar PV installations and underground power cable networks.
In its own announcement of the participation, SAMM Technology said the webinar “provides an excellent opportunity to share knowledge, discuss emerging trends, and demonstrate how innovative monitoring technologies are supporting the future of energy systems,” adding that it was “proud to see Mark Horton representing SAMM Technology on this distinguished panel.”
Why DTS for Solar PV and Underground Cables
Distributed Temperature Sensing turns a standard optical fiber into a continuous string of temperature sensors along its full length, without the need for external power at the sensing points. For underground and solar PV power infrastructure, that capability is particularly relevant: temperature anomalies along a cable route or within a PV installation can be early indicators of developing faults, hotspots, or degrading connections — issues that are otherwise difficult to catch before they cause an outage or safety incident. Panel discussions on this topic typically cover how real-time DTS monitoring data feeds into asset reliability programs, operational efficiency, and system safety practices for energy operators.
How to Attend
The FOSA webinar is scheduled for September 2, 2026, 9:00 AM EDT (13:00 UTC), and will be held online via Zoom. Registration details are available through FOSA’s website.
This article is based on SAMM Technology’s own announcement of its webinar participation (dated August 5, 2026) and FOSA’s official event promotional graphic and public webinar listing.
Meta is piloting robots from three vendors, Watney Robotics, Kinova and ABB, to handle physical maintenance tasks inside its data centers, including swapping network cables, power-cycling servers, reseating components and inspecting equipment, according to an August 31, 2026 report from WIRED based on current and former employees familiar with the trials.
What the Robots Are Doing
At Meta’s Altoona, Iowa campus, a pair of dual-armed Watney robots has been tested on cabling work since June 2025, supervised by human operators and still slower than a person, per the report. At the Prometheus campus in New Albany, Ohio, four-wheel ABB robots equipped with a scissor-lift riser and a six-axis arm are being used to reseat hardware components, and Meta is separately evaluating a Kinova Gen3 robotic arm for power-cycling servers. Meta has also deployed simpler robots that remotely restart devices by physically pressing power buttons. Kinova and ABB declined to comment to WIRED, and Watney did not respond to the outlet’s requests for comment.
Why It Matters
One Meta data-center worker told WIRED that a working cable-swapping system could eventually take on as much as 80% of some technicians’ current workload, though that figure is an employee estimate rather than a company-published target, and the robots still struggle with dense cabling, tight corners and tasks that require sustained autonomy. As AI-driven data center buildouts accelerate, the trials point to facility operations and physical security converging with the same automation trends reshaping server hardware itself.