Author: Osiris

  • ATF Confirms Data Breach After Ransomware Group Claims Access to Investigation Data

    ATF Confirms Data Breach After Ransomware Group Claims Access to Investigation Data

    The Bureau of Alcohol, Tobacco, Firearms and Explosives (ATF) has confirmed a cyberattack affected a system containing information about the targets of its investigations, following claims by a ransomware group that it had gained access to the agency’s data, Reuters reported.

    What’s New

    According to court documents and public reporting, the ransomware group gained access to a computer system holding information related to ATF investigative targets. The agency confirmed the breach but has not disclosed the full scope of the data involved or attributed the intrusion to a specific threat actor.

    Why It Matters

    A breach touching active investigation data raises risks beyond typical data-exposure incidents, potentially compromising ongoing law enforcement operations and the safety of investigative targets and personnel if the information is misused or leaked. The incident adds to a string of confirmed breaches at U.S. federal agencies this year and comes weeks after the Justice Department and FBI moved to disrupt state-sponsored hacking infrastructure targeting other parts of the federal government.

  • Australian Police Charge Two Men Over TeamPCP Hacking Group Linked to Open-Source Supply Chain Breaches

    Australian Police Charge Two Men Over TeamPCP Hacking Group Linked to Open-Source Supply Chain Breaches

    The Australian Federal Police, working with the FBI and the Western Australia Police Force, arrested and charged two Perth-area men on August 26, 2026 over their alleged roles in TeamPCP, a cybercrime group blamed for a string of high-profile breaches this year. Louis Michael Gaebler, 23, of Mandurah, and Ruben Ian Thomson, 21, of Cottesloe, appeared in Perth Magistrates Court on August 27 facing a combined 14 charges, according to the AFP and reporting from TechCrunch, The Hacker News and Help Net Security.

    Investigators allege the pair were principal participants in a syndicate that planted malicious code in popular open-source software projects, which was then unwittingly incorporated by developers and organizations worldwide, according to the AFP statement cited by ABC News Australia. The Hacker News reported that TeamPCP has been tied to the March 2026 compromise of the open-source security scanners Trivy and Checkmarx KICS, as well as the AI gateway LiteLLM, while TechCrunch reported the group has also been blamed for hacks affecting Mercor and OpenAI.

    According to Help Net Security’s account of the charges, the Cottesloe man faces eight offenses including possessing and supplying data for use in computer offenses, unauthorized modification of data, failing to comply with a data-access order, and dealing with proceeds of crime worth more than AU$100,000; the maximum penalties involved range from three to twenty years’ imprisonment. Investigators searched properties in Cottesloe, Hamilton Hill and Mandurah, seizing electronic devices now undergoing forensic examination.

    The AFP said the investigation began in April 2026 after it and the FBI received tips about a syndicate inserting malicious code into open-source packages used by other developers, and that “further arrests and charges have not been ruled out” as the forensic review of seized data continues, per SecurityWeek’s reporting.

    The case highlights the continuing risk that open-source software supply chains pose as a vector for widescale compromise: a single tampered dependency or scanning tool can propagate into the environments of every organization that pulls it into a build pipeline, a dynamic security teams have increasingly had to account for in software composition analysis and dependency-vetting programs.

  • Banking and Financial Institution Security Technology

    Banking and Financial Institution Security Technology

    Financial institutions protect a mix of physical assets, sensitive data and public-facing customer environments, which means bank security spans branch design, vault protection, ATM networks and increasingly the cybersecurity of connected physical-security devices themselves.

    Branch video surveillance

    Branch camera systems cover teller lines, entrances, vaults and parking areas, supporting both robbery response and everyday operational and liability needs. Many institutions pair cameras with silent alarm capability at teller stations so staff can signal a robbery without alerting the person committing it.

    Vault and safe-deposit protection

    Vaults and safe-deposit areas typically combine reinforced construction with time-delay locks, dual-custody procedures and dedicated alarm and access-control zones. These measures are designed to resist both external attack and unauthorized access by an individual employee acting alone, reflecting the dual-custody principle common in financial-security design.

    ATM and self-service security

    ATMs and self-service kiosks operate outside normal branch hours and in some cases outside the branch itself, which creates distinct risks including physical attacks on the machine, card-skimming devices and network-based fraud. Financial institutions typically combine physical hardening, camera coverage, skimmer-detection technology and transaction monitoring to address these different attack types.

    Access control for staff and cash-handling areas

    Access control governs movement between public branch space and restricted areas such as cash rooms, IT closets and back-office operations. Role-based permissions and detailed audit trails support both security and the compliance requirements that apply to financial institutions in most jurisdictions.

    Cyber-physical convergence

    Modern branch security systems, including cameras, access controllers and alarm panels, are networked devices connected to the same infrastructure as core banking systems. That makes cybersecurity hygiene, including network segmentation, credential management and patching, a core part of physical-security design rather than a separate concern, particularly given how attractive financial institutions are as targets.

    Risk varies by institution type and location

    A large urban branch, a rural branch and a data center or operations facility carry different risk profiles, and security programs at most institutions are tailored accordingly rather than using a single standard branch design everywhere.

    Conclusion

    Banking and financial-institution security depends on a combination of branch video and alarm systems, vault and ATM-specific protections, disciplined access control, and cybersecurity practices applied to the physical-security network itself, reflecting the dual role of financial institutions as both cash-handling and data-handling environments.

  • Prison and Correctional Facility Security Technology

    Prison and Correctional Facility Security Technology

    Correctional facilities operate under security requirements that differ from almost any other building type: the population inside is confined rather than free to leave, staff safety and inmate safety must both be protected, and a security failure can have immediate, serious consequences.

    Perimeter detection

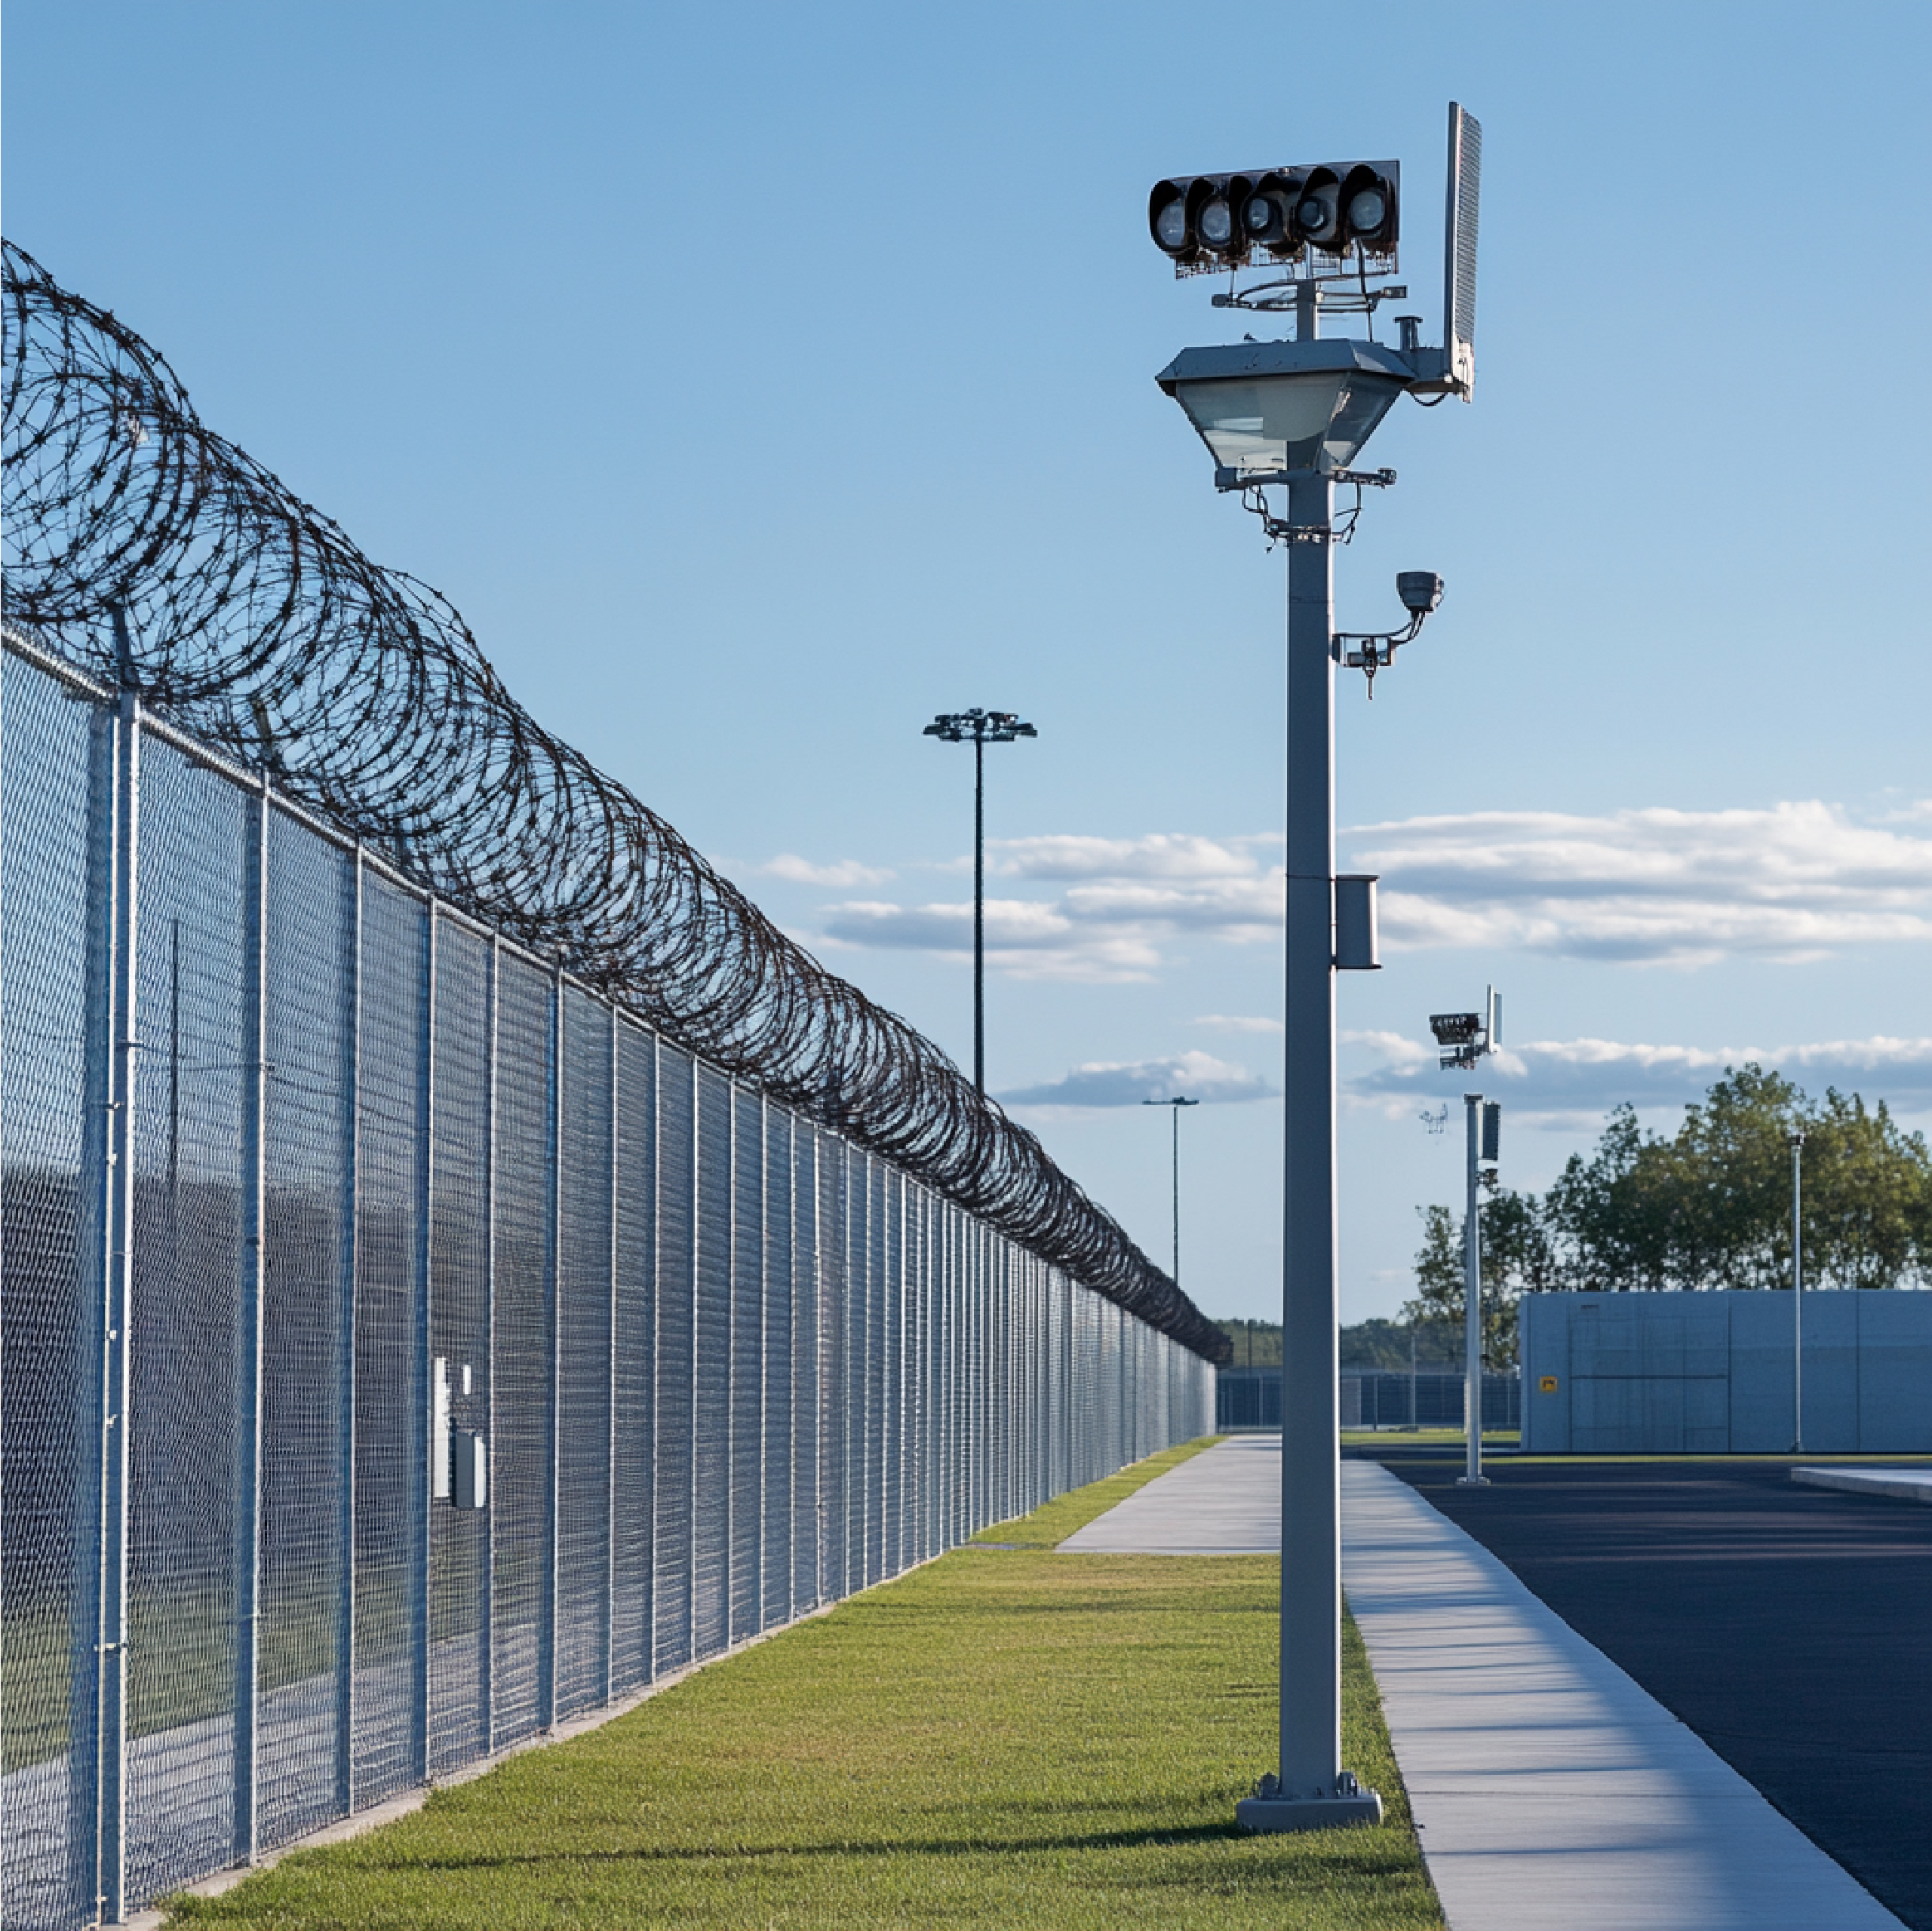
    Correctional perimeters typically combine physical barriers such as double fencing, razor wire and clear zones with electronic detection, including fence-mounted sensors, buried cable systems, microwave or radar detection, and camera coverage. Layered detection is intended to give staff advance warning of an escape attempt or unauthorized approach before a physical breach occurs.

    Video surveillance across a closed environment

    Comprehensive camera coverage of housing units, corridors, yards, visitation areas and perimeter zones supports both incident investigation and day-to-day supervision. Because correctional facilities operate continuously, video systems are typically designed for extended retention and rapid search, since incidents may not be reported or discovered until well after they occur.

    Access control and movement management

    Correctional access control governs not just entry to the facility but internal movement between housing units, program areas and secure zones. Interlocking door systems, sally ports and centrally controlled locking are common design features intended to prevent an inmate or unauthorized individual from moving freely between security zones.

    Contraband and weapons detection

    Screening technology at entry points, including walkthrough and handheld metal detectors, body scanners and mail-screening systems, is used to reduce the introduction of weapons, drugs and unauthorized devices such as cell phones. Contraband detection is an ongoing operational challenge for correctional agencies, and facilities generally combine technology with staff search procedures rather than relying on any single method.

    Duress alarms and staff safety

    Personal duress alarms that allow staff to summon help discreetly, combined with fixed panic buttons in high-risk areas, are a standard feature of correctional security design. Rapid, reliable location information is particularly important in a correctional setting given the potential for an incident to escalate quickly.

    Command and control integration

    Correctional security operations centers typically integrate video, access control, intercom and alarm systems into a single monitoring environment, allowing control-room staff to observe and respond across the facility rather than managing separate systems independently.

    Conclusion

    Correctional facility security depends on layered perimeter detection, comprehensive video coverage, tightly controlled internal movement, contraband screening and reliable staff duress capability, integrated through a command-and-control environment built for continuous, high-consequence operation.

  • Stadium and Large-Venue Security: Screening, Crowd Monitoring and Command Coordination

    Stadium and Large-Venue Security: Screening, Crowd Monitoring and Command Coordination

    Stadiums and large public venues concentrate tens of thousands of people, media, vendors and staff into a fixed footprint for a defined window of time. That combination of scale, timing and public exposure makes venue security a distinct discipline from everyday facility protection.

    Perimeter screening at scale

    Entry screening for a major event has to process large crowds quickly without creating dangerous queuing at the perimeter itself. Many venues now combine walkthrough magnetometers or AI-assisted weapons-detection lanes with bag policies and staffed pat-downs, tuning the mix of technology and staffing to the expected attendance and threat level of a given event.

    Video surveillance and crowd-density monitoring

    Venue-wide camera networks support both security monitoring and operational needs such as identifying overcrowding at concourses, exits or transit points. Crowd-density analytics can alert operators when a specific area approaches capacity, which supports both security response and general life-safety planning for evacuation.

    Access control for restricted areas

    Beyond the general admission perimeter, stadiums manage layered access to locker rooms, broadcast areas, VIP suites, loading docks and back-of-house corridors. Credentialing systems for staff, media and vendors typically combine badges with access-control integration so that movement through restricted zones is logged and can be reviewed after an incident.

    Counter-drone and airspace awareness

    Unauthorized drone activity over stadiums during events has become a more frequent operational concern, and some major venues have added counter-UAS detection capability to identify unauthorized aircraft near the venue during events, coordinating with local aviation and law-enforcement authorities on any mitigation response, since counter-drone mitigation options are tightly regulated in most jurisdictions.

    Unified command and multi-agency coordination

    Large events typically involve venue security, local police, fire and emergency medical services operating from a shared or closely coordinated command structure. A unified command center that brings together video feeds, access-control status, radio communications and public-address control lets these agencies share situational awareness in real time rather than working from separate information sources.

    Planning around specific event risk

    Security planning for a venue is not static: a regular-season game, a championship event and a concert with a different audience profile can carry different risk considerations. Venue operators generally adjust staffing, screening intensity and technology configuration event by event rather than applying a single fixed posture year-round.

    Conclusion

    Stadium and large-venue security depends on technology that can operate at crowd scale, from rapid screening to crowd-density analytics to counter-drone awareness, integrated through a command structure that allows venue security and public-safety agencies to act on the same information together.

  • School and Campus Security Technology: Access, Detection and Communication

    School and Campus Security Technology: Access, Detection and Communication

    Schools and college campuses share a difficult security profile: they must stay open and welcoming to students, staff, families and visitors, while protecting large populations across buildings that were often not designed with modern security requirements in mind.

    Layered access control

    Many K-12 campuses now control building entry with electronic locks, visitor check-in systems and single-point-of-entry designs during the school day, while allowing classrooms to be locked from inside in an emergency. University campuses typically layer broader perimeter and building access around more open pedestrian environments, since restricting movement across an entire campus is rarely practical.

    Visitor management

    Digital visitor-management systems that screen visitors against watchlists, print time-limited badges and log entry and exit have become standard in many districts, replacing paper sign-in sheets. These systems give administrators a real-time record of who is on site, which matters both for day-to-day safety and for emergency accountability.

    Weapons detection and screening

    Some districts and universities have introduced weapons-detection systems at building entrances, ranging from traditional metal detectors to newer AI-assisted scanning designed to move larger volumes of students through checkpoints with less friction than manual bag checks. Adoption varies widely by district and budget, and the technology is generally deployed as one layer among several rather than a standalone solution.

    Video surveillance and analytics

    Camera coverage of entrances, hallways, parking areas and building perimeters supports both incident response and day-to-day safety and discipline needs. Some systems add analytics for tasks such as detecting a propped-open door or unusual after-hours activity, which can be more useful on large, multi-building campuses than continuous human monitoring alone.

    Mass notification and emergency communication

    Rapid, campus-wide communication is central to school security planning. Mass-notification systems typically combine PA announcements, text and email alerts, and integration with local law enforcement, and many districts now tie lockdown procedures to a single trigger that activates locks, notifications and camera views simultaneously.

    Balancing security and learning environment

    Security leaders in education generally caution against measures that make schools feel like fortified facilities, since that can affect student wellbeing without necessarily improving safety outcomes. Physical security investments are typically paired with threat-assessment programs, staff training and clear procedures, which education-security researchers describe as at least as important as the technology itself.

    Conclusion

    Effective school and campus security combines layered access control, visitor management, appropriate detection technology, video coverage and fast communication, implemented in a way that fits the culture and openness required of a learning environment rather than working against it.

  • Retail Loss Prevention Technology: Cameras, EAS and AI in 2026

    Retail Loss Prevention Technology: Cameras, EAS and AI in 2026

    Retail security has to solve two problems at once: reduce theft and operational loss, and keep stores welcoming to paying customers. That balance shapes almost every technology decision in the sector.

    Shrink is more than shoplifting

    Retailers typically group loss into external theft, internal theft, process failures such as pricing or receiving errors, and vendor fraud. Because the causes differ, effective loss-prevention programs combine several tools rather than relying on a single system, and they measure results against the specific type of loss they are meant to address.

    Video analytics and exception-based reporting

    Modern video management systems can flag specific patterns for review, such as high-value transactions without a matching item scan, repeated returns, or unusual dwell time near high-shrink categories. Exception-based reporting narrows a large volume of camera footage down to the clips most likely to matter, which is essential in stores with dozens of cameras and limited loss-prevention staff.

    Electronic article surveillance and RFID

    Electronic article surveillance (EAS) tags and gates remain a baseline deterrent at store exits. Item-level RFID adds a further layer by giving retailers near real-time visibility into inventory location, which supports both loss prevention and out-of-stock reduction. The two technologies are increasingly deployed together rather than as alternatives.

    Point-of-sale integration

    Connecting video to point-of-sale and self-checkout transaction data lets a system correlate what a camera captured with what was actually rung up. This is particularly relevant for self-checkout, where scan-avoidance and mis-scanning account for a meaningful share of shrink at many retailers, and where store layout and camera placement affect how well a system can verify a transaction.

    Access control and back-of-house protection

    Loss prevention extends beyond the sales floor. Receiving docks, stockrooms and cash offices benefit from access control, audit trails and camera coverage focused on internal theft and vendor-fraud risks, which studies consistently identify as a significant share of total retail shrink.

    Balancing security with customer experience

    Overly visible or intrusive security measures can affect how customers perceive a store. Retailers increasingly favor systems that operate quietly in the background, use data to focus staff attention where it is most useful, and avoid treating every shopper as a suspect.

    Conclusion

    Retail loss-prevention technology works best as a layered, data-driven program rather than a single device. The strongest deployments combine video analytics, EAS or RFID, point-of-sale integration and access control, and they measure outcomes against the specific categories of loss each layer is designed to reduce.

  • Denmark Selects Terma to Build Nationwide Counter-Drone Defense System

    Denmark Selects Terma to Build Nationwide Counter-Drone Defense System

    A Shared National Drone Picture

    Denmark’s Ministry of Defence Acquisition and Logistics Organisation (DALO) announced on August 19, 2026 that it has selected Danish defense contractor Terma to deliver an integrated, nationwide command-and-control system for counter-drone defense. The system will connect existing and future sensors operated by the Danish Armed Forces, civilian authorities and critical infrastructure operators into a single shared drone situational picture, according to Terma.

    “To defend ourselves, we need to be able to eliminate enemy drones in our airspace,” Danish Defense Minister Jeppe Bruus said of the contract. Terma said the platform will support the management of drone incidents at military installations, airports, ports, energy facilities, government buildings and other critical infrastructure sites, and that its architecture is designed to allow additional sensors, sites and countermeasures to be integrated over time.

    Built on Terma’s Helion Data Backbone

    The system is based on Terma Helion, the company’s multi-domain data backbone, and will integrate command-and-control and data-fusion software from OSL Technology, which Terma acquired in 2025. The combined platform uses artificial intelligence to process, classify and prioritize sensor data, fusing input from radar, other surveillance systems and third-party sensors to support tactical decision-making at both local and central command levels.

    “This new agreement with Terma is an important cornerstone in the ongoing effort to build a strong counter-drone capability, both within the Danish Armed Forces and Danish industry,” said Lieutenant General Per Pugholm Olsen, chief of DALO. The contract comes as European states have grown increasingly concerned about unauthorized drone activity near military sites, airports and other critical infrastructure. Terma and DALO did not disclose the contract value.

    Sources

  • DHS Awards Department-Wide Contracts for Counter-Drone Capabilities

    DHS Awards Department-Wide Contracts for Counter-Drone Capabilities

    A Common Acquisition Pathway Across DHS

    The Department of Homeland Security announced on August 5, 2026 that it has made multiple contract awards to support department-wide access to Counter-Unmanned Aircraft Systems (C-UAS) capabilities. The awards give DHS components a common pathway to acquire C-UAS hardware, software and services tailored to fixed-site, mobile, aviation, maritime, aircraft-based and special-mission environments, according to the department’s Science and Technology Directorate.

    “These awards mark an important step in strengthening DHS’s ability to respond to unauthorized and malicious unmanned aircraft systems,” said Homeland Security Secretary Markwayne Mullin. “By taking a Department-wide approach, we are improving mission readiness, supporting more consistent capabilities, and helping ensure DHS personnel have access to the right tools for the job.”

    Replacing Fragmented Procurement

    DHS components have historically procured C-UAS capabilities through separate acquisition efforts. The new contract structure is intended to support greater consistency, interoperability, operational flexibility, technology refresh and lifecycle management across the department, while still letting individual components select solutions aligned to their specific missions. The awarded contracts cover detection, tracking, classification, identification, mitigation, command-and-control integration, training, maintenance, technical support, system integration, research and development, test and evaluation, and vendor-operated turnkey services.

    “As unmanned aircraft systems become more capable and more widely available, DHS needs solutions that can adapt,” said Under Secretary for Science and Technology Pedro Allende. Components expected to use the contract include the U.S. Secret Service, U.S. Coast Guard, Customs and Border Protection, Immigration and Customs Enforcement, the Transportation Security Administration, FEMA, the Federal Protective Service, U.S. Citizenship and Immigration Services, and the Science and Technology Directorate itself. DHS did not disclose specific contract values or awardee names in its announcement.

    Sources

  • Johnson Controls Metasys Building Automation Platform Patches Persistent XSS Vulnerability

    Johnson Controls Metasys Building Automation Platform Patches Persistent XSS Vulnerability

    Crafted URL Can Hijack Administrator Sessions

    CISA published ICS advisory ICSA-26-225-14 on August 13, 2026, disclosing a cross-site scripting vulnerability in Johnson Controls Metasys, a building automation and management platform used across critical manufacturing, commercial facilities, government facilities, transportation systems and energy sites worldwide. Tracked as CVE-2026-34491 and rated CWE-79, the flaw carries a CVSS v3 base score of 8.0.

    According to CISA, a low-privilege user can inject a malicious payload into the Metasys web interface through a crafted URL. The payload persists across logins and executes in the browser context of other users who view the affected page, including administrators, which could lead to session hijacking and unauthorized access to building systems. The advisory lists Metasys 12 and 13 as affected in all versions, and Metasys 14 before v14.1.5 and Metasys 15 before v15.0.1.

    Mitigation

    Johnson Controls has released patched versions for the affected Metasys 14 and 15 branches and published mitigation guidance for the platform. CISA recommends operators apply the available updates, restrict Metasys web interface access to trusted networks, and follow standard input-validation and session-management hardening for building management system deployments.

    Sources