
Category: Hospitals

  • Warner and Wyden Reintroduce Bill to Set Mandatory Cybersecurity Standards for Hospitals

    Warner and Wyden Reintroduce Bill to Set Mandatory Cybersecurity Standards for Hospitals

    Senators Mark R. Warner (D-VA) and Ron Wyden (D-OR) reintroduced the Health Infrastructure Security and Accountability Act on September 17, 2026, legislation that would establish mandatory minimum cybersecurity standards for hospitals and other covered healthcare entities and their business associates. The bill largely mirrors a 2024 version the senators introduced previously, with its implementation timeline shifted forward by two years.

    Under the bill, the Department of Health and Human Services would set, enforce and update the minimum standards at least every two years, with heightened requirements for systemically important entities and those deemed critical to national security. Covered entities would also need continuity and recovery plans covering technical failures, disruptive cyber events and natural disasters. The legislation would direct $1.3 billion toward helping hospitals meet the new standards, including $800 million earmarked for rural hospitals and facilities serving underserved urban communities.

    Why it matters

    Healthcare has lagged other critical-infrastructure sectors on baseline cybersecurity requirements even as ransomware and data-theft incidents increasingly disrupt patient care rather than just back-office systems — the bill’s dedicated funding for rural and underserved hospitals directly addresses the resource gap that smaller facilities cite as the main reason they can’t meet the same security bar as large health systems.
    Sources

  • Hospital Security Technology: Protecting Patients, Staff and Clinical Operations

    Hospital Security Technology: Protecting Patients, Staff and Clinical Operations

    Hospitals are open environments with a difficult security balance: they must remain accessible to patients and visitors while protecting people, medicine, data, critical equipment and restricted clinical areas.

    A uniquely open security environment

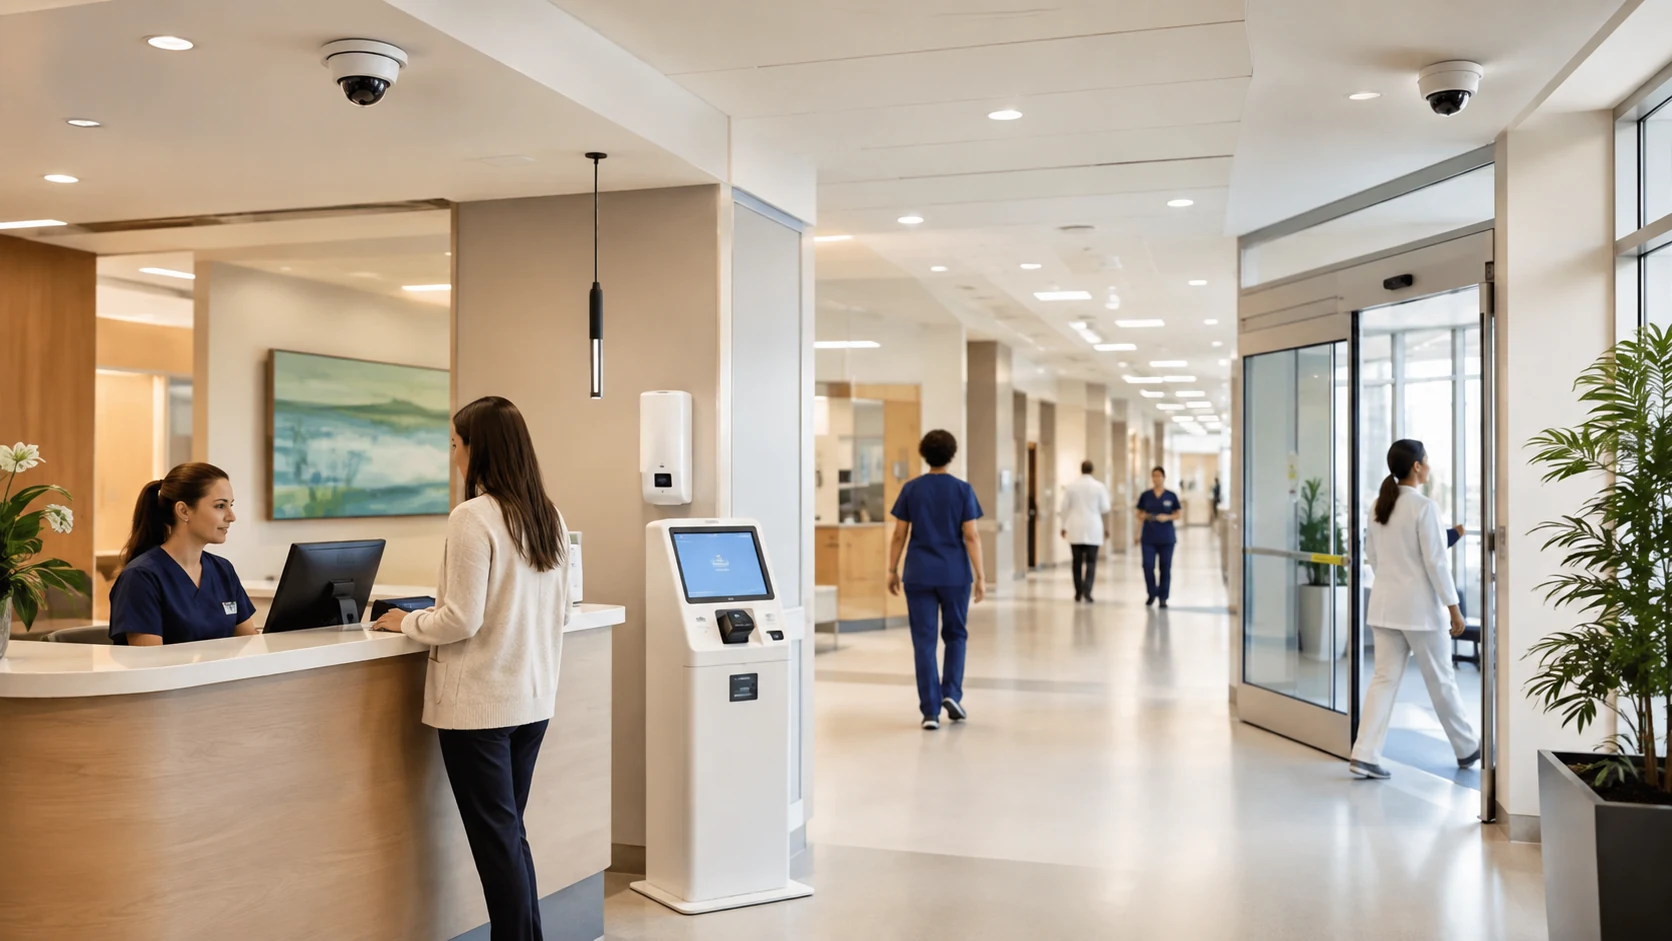
    Unlike many critical facilities, hospitals cannot operate as closed campuses. Emergency departments, outpatient clinics and public entrances create continuous flows of people, making identity, visitor management and staff workflows central to the security design.

    Access and identity

    Modern hospitals commonly combine staff credentials, mobile access, role-based permissions and visitor registration. Sensitive zones such as pharmacies, laboratories, operating rooms, neonatal areas and data rooms require stronger controls and detailed audit trails.

    Video and analytics

    Video systems support investigation, crowd awareness and protection of entrances, parking areas and high-risk corridors. Analytics can help detect unusual movement or congestion, but privacy rules and clinical context require careful policy design.

    Duress and emergency communication

    Staff duress devices, fixed panic buttons and location-aware alerts can shorten response time. Mass notification must reach clinical staff without creating alarm fatigue or interfering with critical care.

    Integration matters

    The most effective hospital security platform connects access events, alarms, video, visitor data and emergency communications. Cybersecurity and privacy governance must be built in because physical-security systems increasingly share the hospital network.

    Conclusion

    Hospital Security Technology should be evaluated as part of a broader operational architecture. The strongest deployments combine suitable sensing technology, resilient communications, clear procedures and measurable performance rather than relying on a single device or headline specification.