Category: News

Current, event-driven reporting, announcements and industry developments.

  • NAPCO Releases Prima v8 App With New Security Controls

    NAPCO Releases Prima v8 App With New Security Controls

    September 4, 2026 — NAPCO Security Technologies has released Prima v8, a redesigned mobile app for its Prima self-contained smart security systems. The update adds revised security controls, biometric authentication, expanded notification settings and an Apple Watch companion app.

    What Changed in Prima v8

    The new version reorganizes navigation and rebuilds core workflows for arming, device control and account management. Security screens provide clearer entry and exit countdowns, alarm details and sensor status information. Users can also manage connected lights, locks, garage doors, water valves and thermostats from the app.

    NAPCO says existing users can install the update without creating a new account or re-pairing their system devices. Credentials, configurations and device pairings are intended to carry over. The Apple Watch companion app supports arming and disarming from the watch, while revised settings give users more control over push, email and SMS notifications.

    Why It Matters

    Residential and small-commercial security platforms increasingly combine alarm status, connected-device control and account administration in one mobile interface. A clearer workflow can reduce routine friction for users and installers, but app convenience does not replace professional system design, reliable communications or an appropriate alarm-response plan.

    The release follows the wider shift toward software-led management of intrusion and connected-building systems. For background on the underlying sensors and control architecture, see SectechMedia’s guide to intrusion detection and alarm systems.
    Sources

  • FOSA Webinar to Explore DTS for Early Fault Detection in Solar PV and Underground Cables

    FOSA Webinar to Explore DTS for Early Fault Detection in Solar PV and Underground Cables

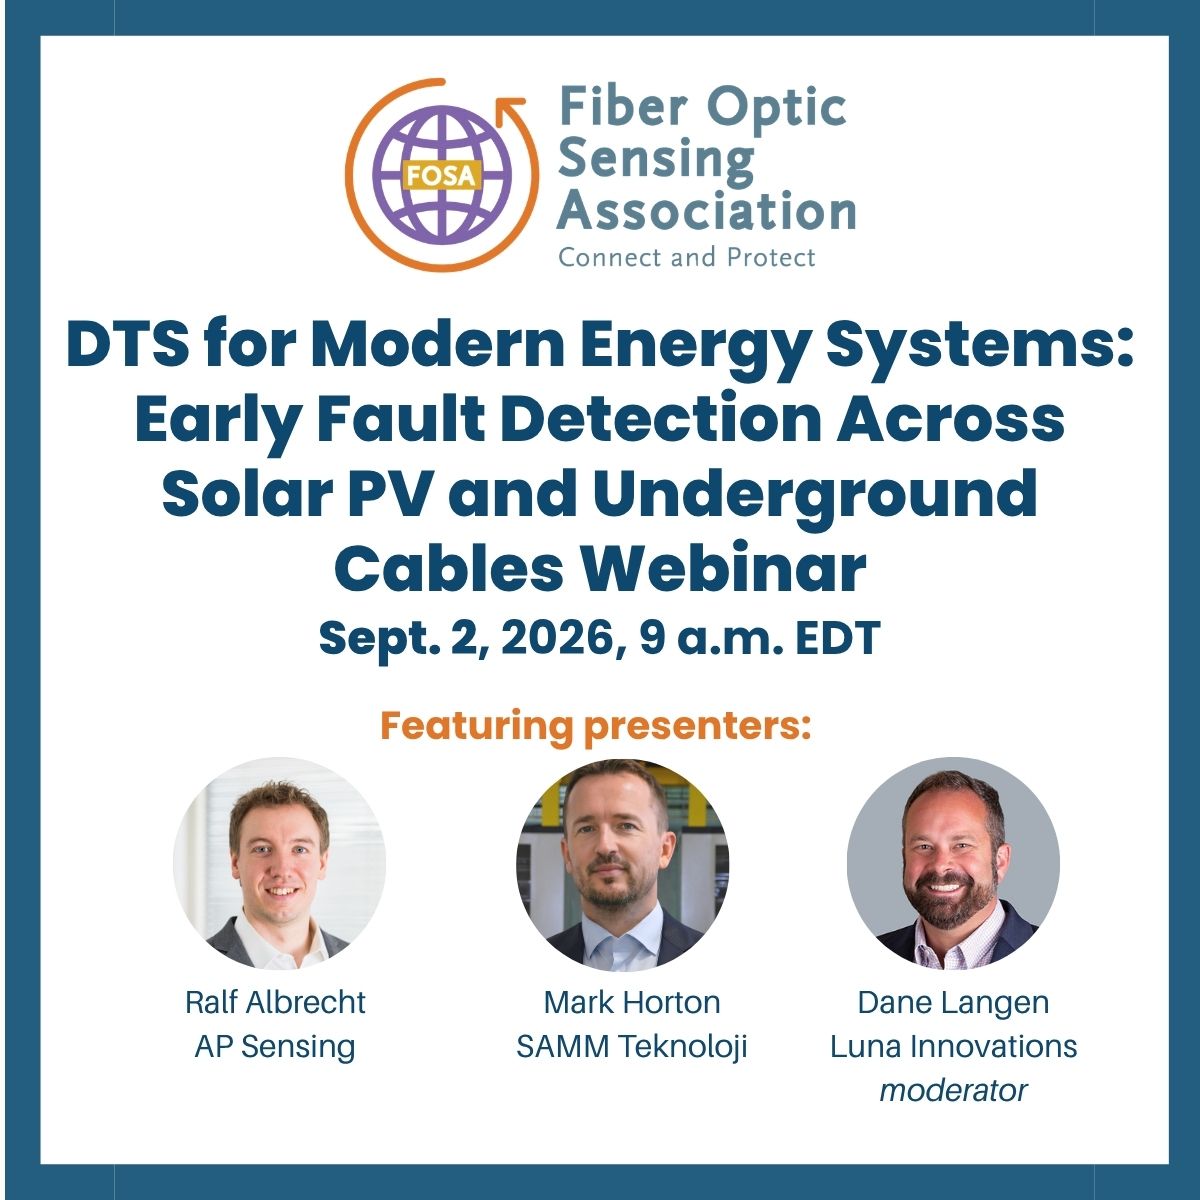
    SAMM Technology (SAMM Teknoloji İletişim A.Ş.) is taking part in an upcoming webinar hosted by the Fiber Optic Sensing Association (FOSA), addressing how Distributed Temperature Sensing (DTS) can support early fault detection across solar photovoltaic (PV) installations and underground power cable networks.

    The webinar, titled “DTS for Modern Energy Systems: Early Fault Detection Across Solar PV and Underground Cables,” takes place on September 2, 2026, at 9:00 AM EDT (13:00 UTC), hosted online via Zoom by FOSA, the US-based non-profit industry association focused on advancing distributed and quasi-distributed fiber optic sensing technologies.

    SAMM Technology on the Panel

    Representing SAMM Technology, Mark Horton, the company’s International Operations Director, joins the session alongside Ralf Albrecht of AP Sensing, with Dane Langen of Luna Innovations moderating. According to FOSA’s own event announcement, the panel will discuss how DTS technology is being applied to monitor modern energy infrastructure, with a focus on practical approaches to early fault detection in solar PV installations and underground power cable networks.

    In its own announcement of the participation, SAMM Technology said the webinar “provides an excellent opportunity to share knowledge, discuss emerging trends, and demonstrate how innovative monitoring technologies are supporting the future of energy systems,” adding that it was “proud to see Mark Horton representing SAMM Technology on this distinguished panel.”

    Why DTS for Solar PV and Underground Cables

    Distributed Temperature Sensing turns a standard optical fiber into a continuous string of temperature sensors along its full length, without the need for external power at the sensing points. For underground and solar PV power infrastructure, that capability is particularly relevant: temperature anomalies along a cable route or within a PV installation can be early indicators of developing faults, hotspots, or degrading connections — issues that are otherwise difficult to catch before they cause an outage or safety incident. Panel discussions on this topic typically cover how real-time DTS monitoring data feeds into asset reliability programs, operational efficiency, and system safety practices for energy operators.

    How to Attend

    The FOSA webinar is scheduled for September 2, 2026, 9:00 AM EDT (13:00 UTC), and will be held online via Zoom. Registration details are available through FOSA’s website.

    This article is based on SAMM Technology’s own announcement of its webinar participation (dated August 5, 2026) and FOSA’s official event promotional graphic and public webinar listing.

  • Meta Tests Robots From Watney, Kinova and ABB to Automate Data Center Maintenance

    Meta Tests Robots From Watney, Kinova and ABB to Automate Data Center Maintenance

    Meta is piloting robots from three vendors, Watney Robotics, Kinova and ABB, to handle physical maintenance tasks inside its data centers, including swapping network cables, power-cycling servers, reseating components and inspecting equipment, according to an August 31, 2026 report from WIRED based on current and former employees familiar with the trials.

    What the Robots Are Doing

    At Meta’s Altoona, Iowa campus, a pair of dual-armed Watney robots has been tested on cabling work since June 2025, supervised by human operators and still slower than a person, per the report. At the Prometheus campus in New Albany, Ohio, four-wheel ABB robots equipped with a scissor-lift riser and a six-axis arm are being used to reseat hardware components, and Meta is separately evaluating a Kinova Gen3 robotic arm for power-cycling servers. Meta has also deployed simpler robots that remotely restart devices by physically pressing power buttons. Kinova and ABB declined to comment to WIRED, and Watney did not respond to the outlet’s requests for comment.

    Why It Matters

    One Meta data-center worker told WIRED that a working cable-swapping system could eventually take on as much as 80% of some technicians’ current workload, though that figure is an employee estimate rather than a company-published target, and the robots still struggle with dense cabling, tight corners and tasks that require sustained autonomy. As AI-driven data center buildouts accelerate, the trials point to facility operations and physical security converging with the same automation trends reshaping server hardware itself.

  • Report: Security Leaders Overconfident on Authentication Even as Modernization Stalls

    Report: Security Leaders Overconfident on Authentication Even as Modernization Stalls

    A new report from rf IDEAS and Wavelynx has found that most security leaders believe their organizations are more advanced than industry peers on authentication, even though barely a quarter describe their systems as largely modernized, according to the 2026 State of Authentication Modernization Report published August 31, 2026.

    Key Findings

    The survey of 500 IT and security leaders at mid-sized to enterprise organizations found 93% believe their authentication and security maturity outpaces their industry peers, yet only 24% said their systems are largely modernized and 53% have not significantly updated authentication systems in at least three years. While 78% called modernization a high priority for the next 12 months, only 72% of managers closer to day-to-day execution agreed it was a high priority, and 27% cited unclear return on investment as a barrier. Among organizations that do prioritize the work, 55% plan to allocate at least $500,000 to it, but credential and authentication upgrades ranked eighth among security initiatives overall, behind higher-profile priorities.

    Why It Matters

    Forty percent of respondents estimated that a breach involving unauthorized access would cost their organization less than $1 million, well below the $4.4 million global average cost of a data breach reported for 2025. rf IDEAS and Wavelynx said the gap between confidence and readiness underscores the need to treat physical and logical access control as a single modernization effort rather than two separate budgets.

  • LastPass Adds Mobile Smart Scanner and Expanded SaaS Monitoring to Business Security Suite

    LastPass Adds Mobile Smart Scanner and Expanded SaaS Monitoring to Business Security Suite

    LastPass rolled out a series of product updates on August 31, 2026 aimed at credential and access management, including what the company describes as the industry’s first Mobile Smart Scanner and expanded SaaS Monitoring capabilities for its Business Max customers, according to the company’s announcement carried by Security Info Watch.

    What’s New

    The Mobile Smart Scanner lets users scan passwords from printed lists, screenshots and handwritten notes through the LastPass Mobile app and convert them into encrypted, autofill-ready credentials. Persistent Monitoring, now fully released across all browser extensions, keeps SaaS visibility active through a permanent browser-extension connection even when a user is signed out of LastPass, and administrators can now set more granular SaaS Protect usage rules for specific users or groups. LastPass also completed its move from a Legacy Admin Console to a single Unified Admin Console, introduced a company-wide sign-up link for Teams, Business and Business Max customers, and is shifting Dark Web Monitoring for consumer accounts to automatic enrollment. The company said it passed independent SOC 2 and ISO 27001/27701 audits with zero findings for a second consecutive year.

    Why It Matters

    LastPass tied the updates to IBM’s 2026 Cost of a Data Breach Report, which found AI-driven attacks rose 56% year over year and added roughly $1 million to average breach costs, with 92% of organizations hit by AI-related breaches lacking adequate AI access controls. The emphasis on visibility and credential hygiene mirrors a broader push across the industry to close the kind of access gaps that groups exploit in AI-assisted phishing and credential-theft campaigns.

  • Pentagon Suspends CMMC Phase II Rollout as Reform Task Force Reviews Program

    Pentagon Suspends CMMC Phase II Rollout as Reform Task Force Reviews Program

    The Department of Defense has suspended Cybersecurity Maturity Model Certification (CMMC) Phase II requirements that were scheduled to take effect November 10, 2026, while a reform task force reviews the program, according to an August 31, 2026 report from Security Info Watch. Phase I self-assessments and current NIST SP 800-171 Revision 2 obligations remain in effect for defense contractors.

    What’s Paused, What Isn’t

    Level 1 self-assessments covering 15 safeguarding requirements from FAR clause 52.204-21 continue on their annual cycle, and Level 2 self-assessments against the 110 security requirements in NIST SP 800-171 Rev. 2 continue every three years with annual affirmation, with results still required in the Supplier Performance Risk System (SPRS). For contracts under DFARS clause 252.204-7012, contracting officers must still verify a current SPRS assessment score before certain awards, extensions or option exercises. Only the timing of third-party CMMC Phase II assessments has changed, not the underlying obligation to safeguard Controlled Unclassified Information, Bill Osborne, vice president of Defense Sector Services at Magna5, told the publication.

    Why It Matters

    The pause gives contractors more time to fix gaps in scope, documentation and System Security Plans before a Third-Party Assessment Organization is engaged, rather than a reason to slow readiness work altogether. Compliance requirements of this kind sit alongside physical protections for critical infrastructure and defense-linked targets that state-linked threat actors continue to probe.

  • Keenfinity Splits Intrusion and Access Control Units Into Radionix and MiCOS

    Keenfinity Splits Intrusion and Access Control Units Into Radionix and MiCOS

    Keenfinity Group is separating its former Intrusion & Access portfolio into two dedicated subsidiaries effective September 1, 2026, with Radionix taking over intrusion alarm systems and MiCOS concentrating exclusively on access control, the company confirmed to Security Info Watch on August 31, 2026.

    New Leadership Structure

    Phil Dutoy, who joined Keenfinity in 2025 and previously worked on the company’s transformation strategy following its carve-out from Bosch, becomes CEO of Radionix. Gregor Schlechtriem, who had led the combined Intrusion & Access business through the Radionix brand launch, moves to lead MiCOS exclusively. Both companies remain wholly owned Keenfinity subsidiaries pursuing separate go-to-market strategies, and Keenfinity said the change will not alter existing product lines: Radionix continues to build on Bosch intrusion technology, while Bosch-branded access control products continue under the same development and support teams.

    Two Legacy Brands, Two Focused Businesses

    Radionix, formally launched at GSX 2025, builds on nearly six decades of intrusion-system heritage and includes the G Series platform that integrates intrusion detection, access control and fire alarm functions. MiCOS revives a brand with more than four decades of access control history and will operate out of Eindhoven, Netherlands, with a development center in Aachen, Germany. Keenfinity became an independent company on July 1, 2025, after Triton completed its acquisition of Bosch’s security and communications technology business.

    Why It Matters

    The split gives each business room to compete more directly in increasingly specialized markets, following a broader industry pattern of vendors separating access control strategy from intrusion detection as buyers demand deeper feature depth in each category rather than a single generalist product line.

  • CISA Ends Six Free Cybersecurity Assessments for Critical Infrastructure Operators

    CISA Ends Six Free Cybersecurity Assessments for Critical Infrastructure Operators

    The Cybersecurity and Infrastructure Security Agency (CISA) has confirmed it is ending six free assessment programs long used by critical infrastructure operators to evaluate their cybersecurity posture, Cybersecurity Dive reported.

    What’s New

    CISA’s regional field staff will no longer conduct Cyber Resilience Reviews, Cyber Resilience Essentials surveys, Ransomware Readiness Assessments, Incident Management Reviews, External Dependencies Management Assessments or Cyber Infrastructure Surveys. All six relied on CISA’s Cyber Security Evaluation Tool (CSET). Acting Cybersecurity Division head Chris Butera said eliminating the “legacy assessments” would “reduce redundancy for CISA and organizations requesting an assessment,” adding that operators can instead reference CISA’s Cybersecurity Performance Goals.

    Why It Matters

    Experts told Cybersecurity Dive that the Cybersecurity Performance Goals are not a substitute for the hands-on, in-person guidance the discontinued assessments provided. Tatyana Bolton, executive director of the OT Cyber Coalition, said “severe budget cuts have forced CISA into a corner where they can no longer provide the level of hands-on, operational support to critical infrastructure that they once did.” The change follows a reported loss of roughly a third of CISA’s workforce and comes as small utilities and rural operators — among the heaviest users of the free assessments — face rising cyber and physical threats with fewer federal resources to call on.

  • Ring Rolls Out TAKE Encryption to Limit Who Can Access Home Security Camera Footage

    Ring Rolls Out TAKE Encryption to Limit Who Can Access Home Security Camera Footage

    Amazon’s Ring announced a new default encryption system for its security cameras and video doorbells on August 26, 2026, called TAKE — short for Throw Away the Key Encryption — designed to limit ongoing access to customer video, including by Ring itself and by law enforcement without a user’s consent, according to the company’s announcement and reporting from The Verge and CEPRO.

    How TAKE Works

    Under the new system, each camera encrypts its video using unique keys that rotate roughly every five minutes. A temporary copy of each key is held in what Ring calls a secure enclave in the cloud, long enough to power features such as smart alerts, video search and AI-generated video descriptions, after which the company says it permanently deletes its copy of that key. Ring has framed the approach as a middle ground between full end-to-end encryption, which would block many of its AI-driven features outright, and its previous architecture, which gave Ring’s cloud infrastructure more persistent access to footage.

    Rollout Timeline

    TAKE is scheduled to become the default encryption setting for all Ring customers worldwide in phases starting in September 2026, according to the company’s announcement.

    Why the Framing Matters

    The change follows years of scrutiny over Ring’s video-sharing practices, including a 2023 FTC settlement over unauthorized employee and law-enforcement access to customer footage, and comes as its former data-sharing partner Flock Safety faces its own wave of municipal contract cancellations over surveillance and privacy concerns. Privacy researchers note that because Ring — not an independent, published standard — designed the key-deletion process itself, customers still have to trust Amazon’s implementation rather than verify it independently, a caveat also raised by outlets covering the announcement.

  • Researchers Find All 21 Tested Open-Weight AI Models Can Be Stripped of Safety Guardrails

    Researchers Find All 21 Tested Open-Weight AI Models Can Be Stripped of Safety Guardrails

    An international research team led by the University of Waterloo and the nonprofit AI-security group FAR.AI found that all 21 of the most widely used open-weight large language models they tested could have their built-in safety protections removed with relatively little technical effort, according to the university’s own announcement, corroborated by EurekAlert and independent technology outlet HyperAI.

    What the Researchers Tested

    The team built an open-source testing tool called TamperBench to standardize how they simulated tampering attacks across the 21 models. Every model examined could be modified to bypass its safety guardrails despite the protections built in by their developers, and the seven defensive techniques the researchers evaluated did not reliably stop the tampering methods they tried, according to the University of Waterloo’s release.

    The Stakes of Open Weights

    “When the safety guardrails are stripped out of a capable model, it can be used at scale for harm in ways a single person could never manage manually,” said Dr. Sirisha Rambhatla, a University of Waterloo professor of management science and engineering and director of its Critical Machine Learning Lab, who led the study. The researchers warned that models stripped of their protections could be used to run large-scale disinformation campaigns, automate convincing scam emails, or produce instructions for creating hazardous materials.

    Open Models Remain Valuable, But Riskier to Control

    The study’s authors were careful to note that open-weight models remain important for research transparency and independent scrutiny, since outside researchers can inspect and test them in ways closed, proprietary systems don’t allow. But once a model’s weights are published, its creator loses most practical ability to prevent later tampering — the opposite trade-off from closed models, where the vendor retains centralized control but outside researchers have far less visibility. The team’s findings, presented at the ACM Conference on Knowledge Discovery and Data Mining, add to a growing body of evidence that AI safety standards are lagging the pace at which open-weight models are approaching the capability of proprietary frontier systems.