Author: Osiris

  • Warner and Wyden Reintroduce Bill to Set Mandatory Cybersecurity Standards for Hospitals

    Warner and Wyden Reintroduce Bill to Set Mandatory Cybersecurity Standards for Hospitals

    Senators Mark R. Warner (D-VA) and Ron Wyden (D-OR) reintroduced the Health Infrastructure Security and Accountability Act on September 17, 2026, legislation that would establish mandatory minimum cybersecurity standards for hospitals and other covered healthcare entities and their business associates. The bill largely mirrors a 2024 version the senators introduced previously, with its implementation timeline shifted forward by two years.

    Under the bill, the Department of Health and Human Services would set, enforce and update the minimum standards at least every two years, with heightened requirements for systemically important entities and those deemed critical to national security. Covered entities would also need continuity and recovery plans covering technical failures, disruptive cyber events and natural disasters. The legislation would direct $1.3 billion toward helping hospitals meet the new standards, including $800 million earmarked for rural hospitals and facilities serving underserved urban communities.

    Why it matters

    Healthcare has lagged other critical-infrastructure sectors on baseline cybersecurity requirements even as ransomware and data-theft incidents increasingly disrupt patient care rather than just back-office systems — the bill’s dedicated funding for rural and underserved hospitals directly addresses the resource gap that smaller facilities cite as the main reason they can’t meet the same security bar as large health systems.

    Sources

  • SightLogix Launches NS12 and TC12 Thermal Cameras for Critical Infrastructure Perimeters

    SightLogix Launches NS12 and TC12 Thermal Cameras for Critical Infrastructure Perimeters

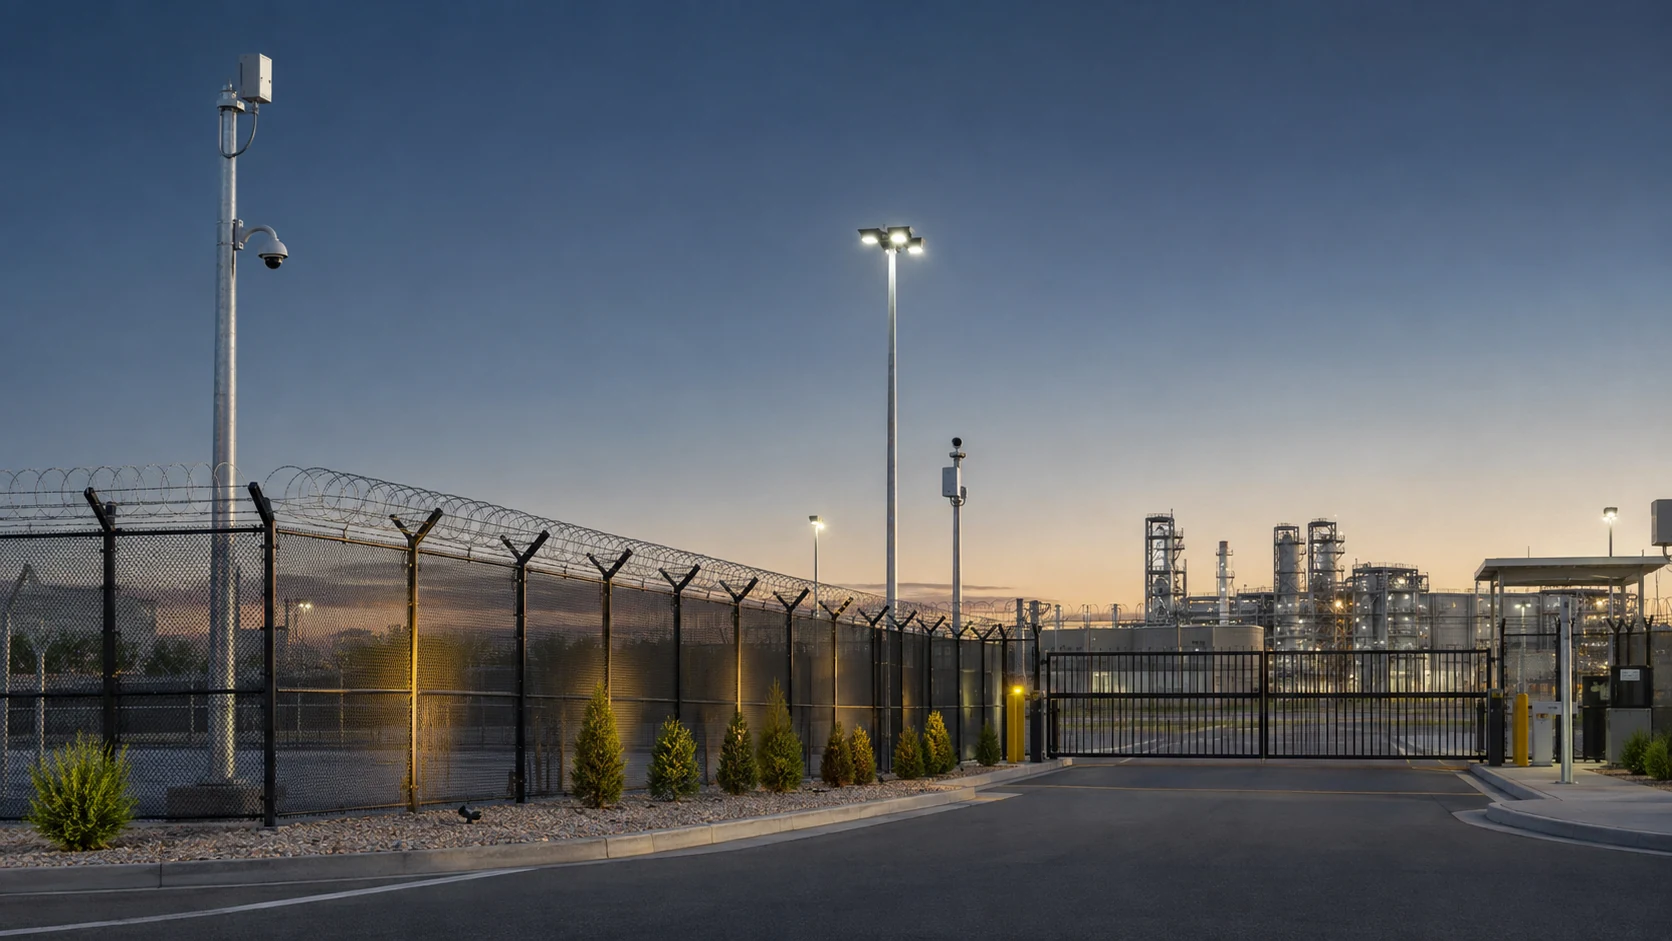
    SightLogix introduced two new fixed thermal cameras, the SightSensor NS12 and TC12, designed to extend perimeter coverage at critical-infrastructure sites while reducing the number of devices needed across large properties. Both use a 1280×1024 thermal imager, which the company says covers approximately 2.5 times the area of a traditional 640×480 thermal camera, and both run on SightLogix’s Gen7 edge-processing platform, which the company describes as delivering 20 times the AI processing throughput of previous generations.

    The NS12 offers detection distances up to 310 meters depending on lens configuration, while the TC12 combines a thermal sensor with a 4K visible-light camera in a single unit, processing both streams on-device without relying on cloud analysis. Both models use edge-based AI classification intended to reduce false alarms, and integrate with SightLogix’s SightTracker PTZ system for automated target following. The company is positioning the cameras for utility substations, data centers, airports, ports, logistics facilities and large industrial campuses.

    Why it matters

    Perimeter camera coverage at large industrial sites is often limited less by camera quality than by how many devices and how much cabling and networking a site can afford to install — a sensor that covers 2.5 times the area of the previous generation directly reduces that per-site device and installation cost for operators securing long perimeters.

    Sources

  • PD Ports Deploys Abloy Electronic Access Control Across UK Sites

    PD Ports Deploys Abloy Electronic Access Control Across UK Sites

    PD Ports, which operates major UK port gateways handling millions of tonnes of cargo annually, has deployed Abloy UK’s PROTEC2 CLIQ electronic access control system across multiple sites, combining mechanical lock protection with digital access management. The port group previously relied on Abloy mechanical products to secure perimeter gates and operational facilities, but growing operations and increasingly complex access requirements prompted it to add electronic control without ripping out the existing hardware.

    The deployment covers 112 PROTEC2 CLIQ keys alongside 32 mechanical padlocks. Each CLIQ key can be programmed and updated remotely, letting PD Ports control permissions across different locations from a central point, and every use is logged through CLIQ Web Manager, creating an audit trail and allowing access rights to be revoked instantly if a key is lost. Because CLIQ keys also operate Abloy’s existing mechanical locks, PD Ports introduced electronic access control incrementally rather than replacing its entire lock inventory at once. The system protects warehouses holding high-value goods as well as perimeter gates and remote access points.

    Why it matters

    Ports typically have large numbers of gates, warehouses and remote access points spread across a site that is expensive to fully re-key — a system that layers electronic control onto existing mechanical locks, rather than requiring wholesale replacement, is often the more realistic upgrade path for large industrial sites with sunk investment in mechanical hardware.

    Sources

  • Hensec Launches Portags, a Combined Drone and GNSS Monitoring Platform for Ports

    Hensec Launches Portags, a Combined Drone and GNSS Monitoring Platform for Ports

    German security company hensec secure solutions launched Portags, short for Port Airspace and GNSS Security, an integrated monitoring platform designed to protect ports against airborne threats and disruption to satellite navigation. Rather than treating drone detection and GNSS interference as separate problems handled by separate systems, Portags fuses data from radio-frequency sensors, passive radar and GNSS signal analysis into a single operational view.

    The system watches the airspace above a port for potential drone activity while simultaneously assessing whether GNSS signals in the area are reliable or under jamming or spoofing attack, giving security teams one interface to detect, assess and document both types of threat. The modular platform can be deployed in stationary or mobile configurations across container terminals, tank farms, port entrances and automated facilities, with open interfaces for integration into existing operations centers. hensec developed Portags following a 2025 measurement campaign that identified combined jamming and spoofing activity in the southern Baltic Sea, as regional nations tighten security cooperation against hybrid threats.

    Why it matters

    Drone incursions and GNSS interference at ports have typically been monitored by separate systems, if at all — correlating the two in one platform matters because attackers increasingly combine tactics, and a port that can only see one threat type at a time may miss an incident where GNSS spoofing and an unauthorized drone are part of the same operation.

    Sources

  • Critical Docker Sandboxes Flaw Let Malicious Code Escape Into macOS Host Files

    Critical Docker Sandboxes Flaw Let Malicious Code Escape Into macOS Host Files

    Docker disclosed and patched a critical vulnerability, CVE-2026-77179, affecting Docker Sandboxes versions 0.28.0 through 0.41.x on macOS. The flaw sits in the virtio-fs host server that Docker Sandboxes uses to share files between a virtual machine and the host: when the server reopens an unlinked file from a previously stored path, it improperly follows symbolic links. A malicious guest can exploit that behavior by replacing a parent directory with a symlink, breaking out of the shared workspace it was supposed to be confined to.

    Once outside the shared workspace, code running inside the sandboxed VM can read or modify arbitrary files anywhere on the host, running with the privileges of the host account that operates the virtual machine, which can extend to host code execution. Docker fixed the issue in version 0.42.0, released September 7, 2026. Docker has not reported any in-the-wild exploitation, and as of the September 16 edition of CISA’s Known Exploited Vulnerabilities catalog, the flaw had not been added.

    Why it matters

    Sandboxing is supposed to be the containment boundary that makes it safe to run untrusted or AI-agent-generated code; a host-escape flaw in the sandbox’s own file-sharing layer undermines that boundary for any developer or CI pipeline that assumed the VM could not touch files outside its assigned workspace.

    Sources

  • Physical Security Risk Assessments: Threat, Vulnerability and Consequence Analysis

    Physical Security Risk Assessments: Threat, Vulnerability and Consequence Analysis

    Security budgets are finite, and not every threat deserves the same investment. A physical security risk assessment is the structured process of identifying what could go wrong at a facility, how likely each scenario is, and how much damage it would cause, so that security spending targets the risks that matter most rather than whatever equipment a vendor is currently promoting. Done well, it produces a prioritized list of gaps tied to actual consequences; done poorly, it produces a generic checklist that could apply to any building anywhere.

    Threat Identification

    The first step catalogs what a facility actually needs to defend against, which varies enormously by site: a data center worries about unauthorized physical access to server racks and insider threats, a retail location worries about theft and workplace violence, a chemical plant worries about sabotage with public-safety consequences. Threat identification draws on crime statistics for the area, the facility’s own incident history, industry-specific threat intelligence, and simply asking staff what near-misses or concerns they have already observed on site.

    Vulnerability Analysis

    Once threats are identified, vulnerability analysis asks how exposed the facility actually is to each one — walking the perimeter, testing access points, and reviewing whether existing controls (fencing, lighting, cameras, access control, guarding) would actually detect or delay a given scenario, as opposed to simply being present. A door with a card reader is not a control if it is routinely propped open; a camera pointed at a loading dock is not a control if no one monitors the feed or reviews it after an incident.

    Consequence and Criticality

    Not every asset in a facility matters equally, so assessments rank assets and areas by criticality: what happens if this specific space, system, or piece of equipment is compromised? A server room outage might halt operations company-wide, while a supply closet breach is a minor loss. This criticality ranking, combined with threat likelihood and vulnerability, is what lets an assessment produce an actual risk score rather than a flat list of undifferentiated findings.

    The CARVER-Style Prioritization Model

    Higher-consequence facilities often use structured scoring frameworks, descended from the military CARVER method (Criticality, Accessibility, Recoverability, Vulnerability, Effect, Recognizability), to rank assets and scenarios on a consistent numeric scale rather than relying on a single assessor’s subjective judgment. These frameworks force the assessment team to score each factor separately before combining them, which helps surface disagreements about, for example, how accessible a target really is, rather than letting one loud opinion in the room set the final priority.

    From Assessment to Action

    An assessment that sits in a binder changes nothing. The output that matters is a prioritized remediation plan mapping each significant gap to a specific fix, an owner, a cost estimate, and a timeline, with the highest-consequence, highest-likelihood gaps addressed first. Because threats and the facility itself both change over time, most security programs treat the risk assessment as a recurring process, typically annual or after any major incident or facility change, rather than a one-time report.

    Reference sources

  • Key Control and Electronic Key Management Systems Explained

    Key Control and Electronic Key Management Systems Explained

    Every access-controlled building still has mechanical keys somewhere: master keys for maintenance staff, override keys for electronic locks during a power failure, keys to server cabinets, vehicles, or cash boxes that were never converted to card access. Key control is the discipline of tracking who holds which key, when, and why — and electronic key management systems exist because a sign-out clipboard in a supervisor’s office does not scale, and does not produce an audit trail anyone can trust.

    From Lockboxes to Electronic Cabinets

    A basic key control program starts with a locked cabinet and a manual log, but electronic key management cabinets replace that with individually locked key slots, or in higher-security versions, keys physically tethered to an electronic fob that only releases when a valid credential is presented. Each key or fob has a unique identifier the system tracks, so the cabinet knows not just that a key was removed, but which specific key, by whom, and whether it was returned to the correct slot.

    Access Rules and Scheduling

    Electronic systems let administrators define exactly which users can access which keys, and when: a contractor might be authorized to remove a specific key only during scheduled work hours, while a facilities manager retains broader access at any time. Some systems require a second authorized user to approve release of high-value or master keys, and most will trigger an alert if a key is not returned within a defined window, turning a vague policy (“please return keys promptly”) into an enforced and logged rule.

    Integration With Access Control and Asset Management

    Because key cabinets are themselves electronic devices, they increasingly integrate with the same access-control platform managing card readers and door hardware, so a single credential works at both the front door and the key cabinet, and a single audit log covers both. Some cabinets extend beyond keys to manage other high-value or sensitive items — radios, weapons, narcotics box keys in healthcare settings, or fleet vehicle fobs — using the same locker-and-credential model.

    Mechanical Master Keying

    Underneath any electronic layer, most buildings still rely on a mechanical master-key system, where individual keys open specific doors and progressively higher master keys open larger groups of doors. Designing and maintaining that hierarchy is its own discipline: a lost sub-master key can force rekeying an entire wing of a building, which is one of the strongest practical arguments for moving high-consequence keys into an electronic cabinet with a full audit trail rather than leaving them in general circulation.

    Reference sources

  • Two-Way Radio and Communication Systems for Security Teams

    Two-Way Radio and Communication Systems for Security Teams

    When a security operations center needs to reach every guard on a property at once, or a guard needs to call for help without dialing a number and waiting for someone to answer, two-way radio still outperforms cellular communication — which is why it remains standard equipment for security teams even in facilities otherwise saturated with smartphones and networked devices. The technology has changed substantially from the analog handhelds of a generation ago, but the core advantage, instant one-to-many communication independent of a carrier network, has not.

    Analog vs. Digital Radio

    Analog radios remain in use for their simplicity and low cost, but digital radio systems, built on standards like P25 (common in North American public safety) or DMR (widely used commercially), offer clearer audio at the edge of range, encryption options, and the ability to carry data alongside voice, such as GPS location or status updates. Digital systems also support trunking, where a pool of radio channels is shared dynamically across many users and talkgroups rather than each group being locked to a single dedicated frequency.

    Talkgroups and Channel Discipline

    Larger security operations organize radio traffic into talkgroups, separate channels for different teams, shifts, or functions, such as patrol, dispatch, and emergency, so that routine chatter does not bury a genuine emergency call. Effective radio discipline (clear callsigns, brief transmissions, a defined process for emergency traffic to interrupt routine use) matters as much as the hardware, since a radio system is only as useful as the protocol governing how people use it under stress.

    Coverage: DAS and Repeaters

    Radio range is limited by building materials, terrain, and radio-frequency interference, which is why large or below-grade facilities often deploy a distributed antenna system (DAS) or repeaters to extend coverage into stairwells, parking structures, and basement levels where a direct radio signal would not reach. Many jurisdictions now require in-building radio coverage systems for first-responder communication as a life-safety code requirement, separate from and in addition to whatever radio system a security team uses day to day.

    Integration With Duress and Dispatch Systems

    Modern radio systems increasingly integrate with software dispatch platforms, letting a control room see which radio units are active, log call history automatically, and trigger a radio-based duress alert that surfaces on a dispatcher’s screen with the reporting unit’s identity and location rather than requiring a verbal report during an active incident. This integration turns the radio network from a simple voice channel into a data source that feeds incident logging and after-action review.

    Interoperability With Public Safety

    Facilities that regularly coordinate with police or fire, such as stadiums, hospitals, and large campuses, often need their radio systems to interoperate with public-safety agencies during a major incident, which typically means supporting shared frequencies, mutual-aid talkgroups, or gateway devices that bridge a private security radio system with a public-safety network without requiring every private-security radio to be reprogrammed on the spot.

    Reference sources

  • Physical Penetration Testing: How Red Teams Assess Physical Security Programs

    Physical Penetration Testing: How Red Teams Assess Physical Security Programs

    A facility can pass every compliance checklist — badges issued, cameras installed, doors alarmed — and still be vulnerable to someone who simply holds a door for a stranger carrying boxes. Physical penetration testing exists to find that gap before an adversary does, by hiring a team to actively attempt unauthorized entry, credential theft, or data exfiltration using the same techniques a real intruder would use, rather than reviewing policies and equipment lists from a desk.

    Scoping and Rules of Engagement

    Every physical penetration test starts with a written scope defining exactly what testers are authorized to attempt, which buildings and hours are in play, and critically, what to do if a tester is confronted or detained — typically a “get out of jail free” letter signed by an authorized executive that testers carry and can present to security or police. Rules of engagement also specify hard limits: most engagements exclude anything that could cause real property damage, injury, or trigger an actual emergency response, distinguishing a controlled assessment from genuine criminal activity.

    Social Engineering and Tailgating

    The most commonly successful technique in physical penetration tests is not defeating a lock but exploiting human courtesy: tailgating through a badge-controlled door behind an employee, posing as a vendor or delivery driver, or simply projecting enough confidence and a plausible cover story that staff assume someone else already verified the visitor. These tests measure whether a facility’s access-control technology is actually being used as designed, since a mantrap or turnstile provides no protection if employees routinely hold the door for anyone walking behind them.

    Lock Bypass and Physical Defeat

    Where technology is tested directly, common techniques include lock picking and bumping on mechanical locks, shimming or manipulating electronic strike hardware, and testing whether door sensors and alarms actually trigger and are actually monitored rather than just installed. Testers also probe less obvious entry points: loading docks, roof access, shared stairwells in multi-tenant buildings, and ceiling tiles or under-floor spaces that can bypass a badge-controlled door entirely.

    Reconnaissance Before the Test

    Serious engagements begin with open-source reconnaissance well before anyone sets foot on site: employee badge photos posted on social media, building floor plans in public permit filings, shift-change patterns visible from a parking lot, and vendor or contractor uniforms that can be replicated. This phase mirrors the reconnaissance a genuine threat actor would conduct and often reveals more exploitable information than the physical test itself.

    Reporting and Remediation

    A physical penetration test is only useful if its findings translate into fixed gaps rather than a list of embarrassing anecdotes. Effective reports document each successful and failed attempt with timestamps and evidence, map findings to the specific control that failed (a policy, a piece of technology, or a training gap), and prioritize remediation by how easily the same technique could be repeated by someone with less skill or access than the test team had.

    Reference sources

  • Elevator and Vertical Transportation Security Technology

    Elevator and Vertical Transportation Security Technology

    In most multi-story buildings, the elevator is the fastest way to move between floors — which makes it both a convenience and a security gap. A lobby with a card reader at the front door does little good if anyone who reaches the elevator bank can ride to any floor once inside. Vertical transportation security addresses that gap through a combination of access control integration, fire-service overrides, and monitoring that has to work even when the building’s normal operating logic is suspended during an emergency.

    Destination Dispatch and Floor Restriction

    The most common access-control integration restricts which floors a rider can select, either by requiring a credential at a lobby turnstile before the elevator call is even registered, or by requiring a card or mobile credential to be presented inside the cab before a floor button will respond. Destination-dispatch systems take this further: a rider enters their destination floor at a lobby kiosk rather than inside the cab, and the system assigns them to a specific car and groups passengers heading to similar floors, which both improves traffic efficiency and gives the access-control system a clean record of who requested which floor before they ever board.

    Firefighter’s Service and Fire Recall

    Every access restriction built into an elevator has to yield to fire-service requirements. Under Phase I recall, activating a fire alarm sends all elevators in the affected bank to a designated landing, typically the ground floor, where they park with doors open until firefighters take manual Phase II control using a key switch inside the cab. This recall function overrides any access-control floor restriction in place during normal operation, and life-safety codes require it to work independent of the building’s access-control system in case that system has failed or lost power.

    Shaft and Machine Room Monitoring

    Beyond passenger-facing controls, elevator machine rooms and shaft access points are themselves targets for tampering, since disabling or manipulating elevator controls can create both a safety hazard and a way to bypass floor restrictions elsewhere in the building. Machine room doors are typically included in the building’s access-control and alarm system like any other restricted space, and some buildings add door-position sensors on shaft access doors at each floor to detect unauthorized entry into the shaft itself.

    Cameras in the Cab

    Camera coverage inside elevator cabs presents a narrower field of view and more variable lighting than open building spaces, which has driven demand for cameras designed specifically for cab mounting — typically compact, ceiling- or corner-mounted units with wide-angle lenses and onboard storage or wireless transmission, since cars moving between floors can briefly lose connectivity to a wired network. Video from cab cameras is used both for incident investigation and, increasingly, for analytics that can flag events like a fall or an altercation in the confined space of a moving car.

    Emergency Communication

    Elevator emergency phones remain a code requirement in most jurisdictions, but the technology behind them has moved from a simple two-way phone line to two-way voice communication systems tied into the building’s broader emergency communication and monitoring platform, often with automatic location identification so a monitoring center knows which car and which building a call originates from without the trapped passenger needing to describe their location.

    Reference sources