Category: Articles & Analysis

Long-form guides, explainers, comparisons, analysis and sector assessments.

  • AI Video Analytics in 2026: What Actually Works

    AI Video Analytics in 2026: What Actually Works

    AI video analytics has moved from a specialist add-on to a core layer of modern physical security. The useful question is where it performs reliably enough to improve operations and reduce investigation time.

    Mature use cases

    Person and vehicle detection, line crossing, loitering, occupancy, queue analysis and basic object classification can be effective when scenes and objectives are clearly defined.

    Claims that require caution

    Vague predictions of suspicious intent or complex behavior are context dependent. These systems should support operators rather than act as unquestionable decision makers.

    Architecture choices

    Edge analytics can reduce bandwidth, server analytics can use larger models, and cloud analytics can simplify scaling. Enterprises often combine all three.

    How to evaluate performance

    Accuracy is not one universal number. Testing should examine precision, recall, nuisance alarms and performance across day, night, rain, glare, occlusion and seasonal change.

    Workflow, privacy and governance

    Detection is most useful when connected to maps, cameras, access status and response procedures. Organizations should also document data processing, retention and whether biometric identification is involved.

    Conclusion

    AI delivers the most value when it solves a narrow, measurable operational problem and is verified under representative site conditions.

  • Unified Security Platforms: Integration vs True Unification

    Unified Security Platforms: Integration vs True Unification

    Security vendors often use integration and unification interchangeably, but they describe different architectures. Integration connects separate products; unification begins with shared data, identity, workflows and administration.

    Traditional integration

    A VMS, access-control system and intrusion platform may remain independent applications that exchange events through APIs or middleware, while retaining separate users, databases and upgrade cycles.

    What true unification changes

    A unified platform can provide one operator interface, common permissions and shared event handling across video, access, alarms and other systems.

    Operational benefits and data model

    Shared workflows can reduce training and speed response. The deeper distinction is whether identity and event objects are genuinely shared or merely displayed together.

    Vendor dependence and best-of-breed systems

    Unification may increase dependence on one vendor. Buyers should examine open APIs, third-party device support and export options. Specialized sites may still justify best-of-breed subsystems.

    Cybersecurity and migration

    A unified platform can simplify identity and patching but also concentrates risk. Many enterprises should migrate gradually through federation or integration as legacy systems reach end of life.

    Conclusion

    A single dashboard is not proof of unification. The correct architecture depends on scale, legacy investment, specialized requirements and long-term platform strategy.

  • Edge vs Cloud in Physical Security

    Edge vs Cloud in Physical Security

    Physical security now depends on where data is processed. Cameras can analyze video at the edge, on-site servers can run analytics, and cloud platforms can centralize management across many locations.

    What edge means

    Edge processing happens close to the sensor. A camera may classify people and vehicles locally, record to onboard storage and send only metadata or alarms, reducing bandwidth and preserving local operation.

    What cloud means

    Cloud platforms provide centralized management, remote access, scalable computing and software updates, particularly for distributed organizations that do not maintain servers at every site.

    Latency, bandwidth and resilience

    Local decisions can reduce latency for immediate actions. Systems must also define what happens during WAN failure: critical cameras should keep recording and doors should continue enforcing access rules.

    Cybersecurity and cost

    Cloud services centralize identity and updates but introduce vendor and account risks. Edge fleets require local patching. Cost comparisons should include servers, subscriptions, bandwidth, maintenance, replacement and staffing.

    Hybrid architecture

    Many organizations record locally while using cloud management and health monitoring. Basic analytics may run at the edge while cross-site search uses centralized services.

    Conclusion

    Edge is strong for autonomy and low latency; cloud is strong for scale and management. A deliberate hybrid design often provides the best balance.

  • Cyber-Physical Security Convergence: Why IT and Security Teams Are Merging

    Cyber-Physical Security Convergence: Why IT and Security Teams Are Merging

    Physical security systems increasingly run on IP networks, cloud services and software platforms, while cyber incidents can create physical consequences. This is pushing IT, cybersecurity and physical-security teams toward closer operational convergence.

    Physical devices are cyber assets

    Cameras, door controllers, intercoms, alarm panels and sensors contain processors, firmware and network interfaces. Weak credentials, vulnerable software or unnecessary services can turn protective equipment into a cyber entry point.

    Identity and incident convergence

    Joiner, mover and leaver processes should update both digital and physical permissions. Badge activity, login records, forced doors and camera status can also provide stronger incident context when correlated.

    Architecture and governance

    Security devices should not sit on unmanaged flat networks. Segmentation, secure remote access, logging and vulnerability management require shared ownership across IT, cyber and physical-security functions.

    Cloud and operational technology

    Vendor security posture becomes part of procurement as video and access platforms move to cloud services. Critical infrastructure must also consider OT systems that control physical processes.

    Benefits and limitations

    Convergence can improve asset visibility, investigation and policy consistency, but it does not require every department to merge. Clear responsibilities and escalation paths remain essential.

    Conclusion

    Unified identity, shared data and careful correlation will continue to drive cyber-physical convergence. Isolated facilities systems are increasingly difficult to govern securely.

  • Sensor Fusion: Why Cameras Alone Are No Longer Enough

    Sensor Fusion: Why Cameras Alone Are No Longer Enough

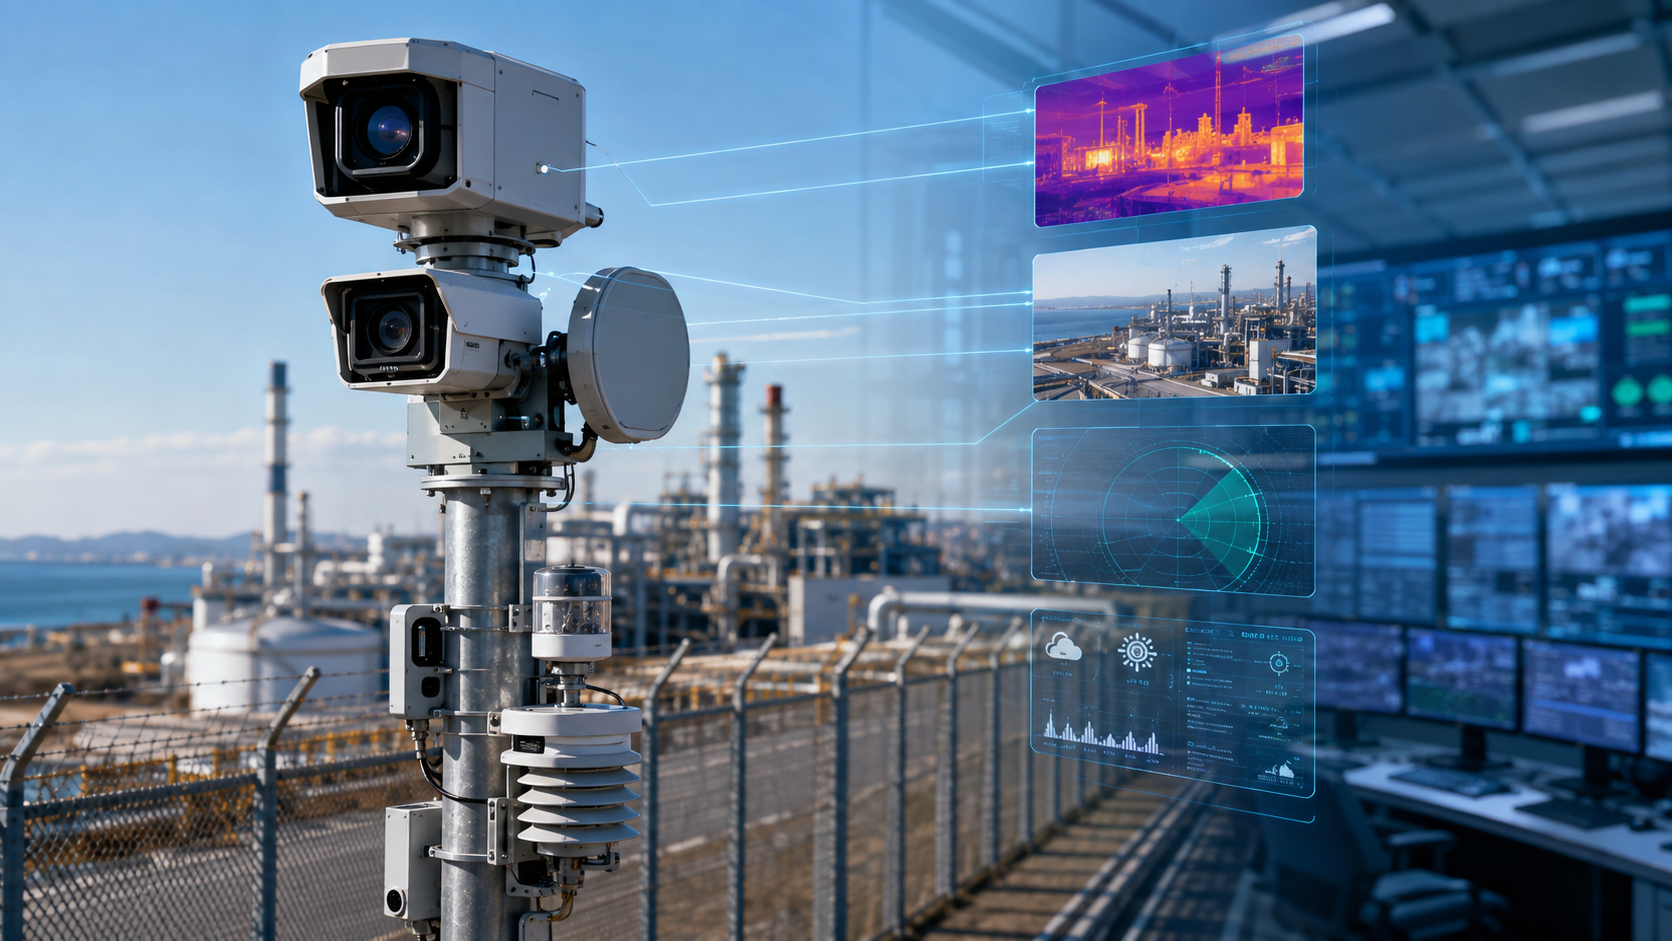
    No single sensor sees everything. Cameras provide rich visual information, radar tracks movement, thermal cameras detect heat and fiber-optic sensing covers long distances. Sensor fusion combines these complementary strengths.

    Detection, tracking and verification

    A useful layered model separates three functions. One sensor detects an event, another tracks the target, and a third verifies what it is. Access-control data can add authorization context.

    Reducing nuisance alarms

    Requiring agreement between independent sensors can improve confidence. A fence vibration event, for example, can be checked against thermal or video analytics before escalation.

    Data correlation

    Fusion is more than displaying systems on one screen. A platform must correlate time, location and identity so operators receive a coherent incident rather than unrelated alarms.

    Perimeter and critical infrastructure

    Radar, thermal, visible cameras and fiber sensors can provide overlapping coverage. Pipelines, railways and power networks may also combine sensing with weather, drone or operational data.

    Engineering challenges

    Different clocks, coordinate systems and event formats complicate integration. Time synchronization, data normalization and complementary failure modes are essential.

    Conclusion

    Security is moving from device-centric systems toward context-centric operations. Sensor fusion is the architecture that enables that transition.

  • LiDAR for Physical Security: Technology, Applications and Limitations

    LiDAR for Physical Security: Technology, Applications and Limitations

    LiDAR measures distance using laser light and can create a detailed three-dimensional representation of an area. In physical security, this supports detection and tracking based on geometry rather than visible appearance.

    How LiDAR works

    A sensor emits laser pulses and measures the time required for reflections to return. Repeated measurements create a point cloud showing the position of objects and surfaces.

    Security applications

    LiDAR can monitor entrances, facades, rooftops, restricted zones, warehouses and open areas. It can also support people counting, queue analysis and occupancy monitoring.

    Three-dimensional zones and privacy

    Virtual detection volumes can be created around assets, fences or doorways. Point clouds may represent people as shapes rather than conventional images, reducing identifiable visual data without removing privacy obligations.

    Limitations

    Heavy rain, fog, highly reflective surfaces and direct environmental conditions can affect performance. Range and point density vary between devices, and cost may exceed that of basic cameras or motion sensors.

    LiDAR, radar and video

    Radar often provides longer-range detection and stronger all-weather performance; LiDAR provides precise spatial detail; video provides texture, color and identity information. Combining them can improve tracking and verification.

    Conclusion

    LiDAR is most valuable where precise 3D awareness or privacy-conscious detection is important. Selection should follow site testing rather than generic range or accuracy claims.

  • Radar in Commercial Security: Where It Works Better Than Cameras

    Radar in Commercial Security: Where It Works Better Than Cameras

    Compact radar has become increasingly practical for commercial security. Modern sensors can detect, locate and track people or vehicles across wide outdoor areas, often in conditions where cameras struggle.

    How security radar works

    Radar transmits radio-frequency energy and analyzes reflections from objects. By measuring distance, angle and Doppler movement, a system can estimate a target’s position, speed and direction.

    Where radar outperforms cameras

    Radar does not depend on visible light and can operate in darkness. It can detect movement over wide open areas without requiring a detailed visual image, making it useful for large yards, airports, solar farms, ports, logistics areas and critical infrastructure.

    Tracking, verification and camera cueing

    Radar excels at tracking but does not provide identity. A visible or thermal PTZ camera can be cued automatically to verify a target and provide richer visual context.

    Coverage and nuisance alarms

    Vegetation, water, machinery, terrain, buildings and metal structures can affect performance or create shadow zones and reflections. Placement requires a site survey and realistic acceptance testing.

    Privacy, cybersecurity and integration

    Radar can support detection where continuous video raises privacy concerns, with video activated for verification. Networked radar also requires secure configuration, firmware management, segmentation and reliable VMS integration.

    Conclusion

    Radar is not a camera replacement. It is a complementary sensor that is often better at answering where a moving target is, how fast it is moving and where it is going.

  • Thermal Imaging in Security: Applications, Advantages and Limitations

    Thermal Imaging in Security: Applications, Advantages and Limitations

    Thermal cameras detect infrared radiation emitted by objects. Because they do not rely on visible illumination, they can detect people, vehicles and equipment in darkness and many difficult lighting conditions. Their strongest role is as part of a layered detection and verification architecture.

    Perimeter security

    Thermal imaging is especially valuable for perimeter detection. A person may appear as a clear heat contrast when a conventional camera sees only darkness. When paired with properly configured analytics, thermal cameras can classify targets and generate alarms for operator verification.

    Industrial monitoring

    Thermal cameras are also used to monitor electrical equipment, batteries, process machinery and storage areas for abnormal heat. In these applications, the same sensing platform can contribute to both safety and security operations. Temperature-related conclusions require equipment designed and configured for measurement, not merely thermal video.

    Performance in smoke, haze and low contrast

    Thermal imaging can sometimes provide useful visibility through light smoke, haze or difficult backlighting where visible cameras struggle. Performance still depends on atmospheric conditions, target contrast, wavelength and the characteristics of the scene.

    Advantages of thermal imaging

    • Operation without visible illumination
    • Strong contrast for many warm targets
    • Useful detection capability across large or remote areas
    • Potential privacy advantages where facial detail is unnecessary

    Important limitations

    Thermal cameras do not see through walls and cannot always identify a person. Glass may reflect or block thermal radiation depending on wavelength. Heavy rain, high humidity and extreme ambient temperatures can reduce effective detection performance. Thermal imagery also requires different interpretation from visible video.

    Radiometric and non-radiometric systems

    Some thermal cameras estimate temperature values, while others are intended only for imaging and detection. Temperature-measurement applications require suitable radiometric equipment, calibration, emissivity settings and environmental compensation. A non-radiometric security camera should not be treated as a precision temperature instrument.

    Analytics and seasonal testing

    Analytics can detect people or vehicles in thermal scenes, but training data and scene configuration matter. A system should be tested under representative seasonal and weather conditions because temperature contrast changes throughout the year.

    Integration with other sensors

    A common architecture uses thermal cameras for detection and visible PTZ cameras for verification. Radar can add tracking and range information. Combining complementary sensors can provide stronger situational awareness than relying on any single technology.

    Choosing a thermal camera

    Selection should begin with the required detection task, field of view, target distance, environmental conditions and integration workflow. Resolution, lens focal length, thermal sensitivity and environmental rating matter, but no single specification determines real-world performance.

    Conclusion

    Thermal imaging is a powerful specialized tool for physical security and industrial monitoring, but it is not a universal replacement for visible cameras. The best results come from risk-based design, realistic acceptance testing and integration with verification and response procedures.

  • Physical Security Technologies: From Fences to Ballistic Protection

    Physical Security Technologies: From Fences to Ballistic Protection

    Physical security is the combination of people, procedures, architecture, and technology used to protect people, facilities, operations, and assets from physical threats. It spans far more than cameras and access cards. A complete strategy can include site planning, fences, gates, lighting, intrusion detection, vehicle barriers, secure doors, glazing, ballistic-resistant assemblies, surveillance, communications, and trained response.

    The central design principle is layering. No single fence, sensor, lock, or rated material can address every threat. Effective protection uses complementary measures to deter an adversary, detect activity, delay progress, support assessment, and enable a proportionate response.

    Begin with risk, not equipment

    The U.S. Interagency Security Committee’s Risk Management Process frames facility protection around determining the facility’s security level, identifying risks, and selecting appropriate countermeasures. The same logic applies outside federal facilities: define what must be protected, identify credible threats and vulnerabilities, assess consequences, and then select measures that reduce risk to an acceptable level.

    A warehouse, data center, hospital, school, airport, power substation, and public venue require different designs. The objective is not to maximize visible hardware. It is to create a defensible system whose detection, delay, and response times work together.

    Site boundaries, fences, and controlled approaches

    Fences establish a boundary, channel movement, and can provide delay, but their performance depends on height, construction, foundations, gates, nearby climb aids, terrain, and inspection. The design should also preserve sightlines where surveillance and patrols need them. Landscaping, signage, and lighting can reinforce the boundary without creating concealment or unnecessary hazards.

    Gates are often more vulnerable than the fence line because they must support routine vehicle and pedestrian flow. Their locking, monitoring, safety controls, credentialing, and emergency operation should be treated as part of the security system rather than as standalone mechanical products.

    Vehicle barriers and hostile-vehicle mitigation

    Bollards, road blockers, wedges, gates, planters, reinforced street furniture, and landscape features can help keep unauthorized vehicles away from people or critical structures. The appropriate solution depends on the threat vehicle, approach geometry, available stand-off distance, traffic operations, emergency access, accessibility, drainage, utilities, and foundation conditions.

    Crash performance must be supported by the relevant test standard and rating for the intended scenario. ASTM F2656 addresses vehicle security barriers for medium-duty and heavy vehicles, while ASTM F3016 covers low-speed vehicle impact testing. A rating is not a universal promise: installation details, foundations, site geometry, and tested configuration matter.

    Doors, locks, access control, and compartmentation

    The building envelope continues the layered system. Doors, frames, hinges, glazing, locks, and surrounding construction should be considered as an assembly. A high-security lock installed in a weak door or frame does not create a high-security opening. Access control adds identity, authorization, event records, and centralized management, but mechanical egress, fire safety, fail-safe or fail-secure behavior, and emergency procedures remain essential.

    Inside a facility, zoning and compartmentation restrict movement after the outer boundary has been crossed. Critical rooms may need stronger construction, two-factor access, anti-tailgating measures, monitored doors, or local response procedures based on risk.

    Intrusion detection, surveillance, and assessment

    Detection technologies can include fence-mounted sensors, buried sensors, magnetic contacts, motion detectors, radar, thermal cameras, visible-light cameras, and distributed fiber optic sensing. Each responds to different physical phenomena and environmental conditions. Combining independent sensing modes can improve confidence, but only if alarm logic and operator workflow are designed to avoid overload.

    Surveillance supports assessment and investigation. It should be designed around operational tasks: detect a person or vehicle, recognize activity, identify a subject where lawful and necessary, verify an alarm, or reconstruct an event. Camera placement, lighting, field of view, pixel density, retention, cybersecurity, and operator workload are more important than simply maximizing camera count.

    Ballistic-resistant protection

    Ballistic-resistant glazing, opaque panels, doors, frames, transaction windows, and guard enclosures are used where a threat assessment identifies a firearms risk. The protection must be specified as a tested assembly for the relevant threat, not by vague labels such as “bulletproof.” UL 752 is one established standard for bullet-resisting equipment. NIJ Standard 0108.01 addresses ballistic-resistant protective materials, although project teams should confirm whether a newer or jurisdiction-specific requirement applies.

    Material selection alone is insufficient. Joints, frames, penetrations, mounting, supporting construction, spall behavior, visibility, weight, fire performance, and egress can determine whether the installed system performs as intended. Field modifications that differ from a tested construction require careful engineering review.

    Blast, forced-entry, and related threats

    Ballistic resistance, forced-entry resistance, and blast resistance are different performance requirements. A product tested for one should not be assumed to satisfy the others. Blast design may involve stand-off distance, structural response, façade and glazing behavior, fragment hazards, and progressive-collapse considerations. Forced-entry design focuses on resisting tools, impact, and sustained attack for a defined period. Where these hazards are credible, qualified specialists should translate the risk assessment into tested performance requirements.

    People, procedures, and response

    Technology cannot compensate for an undefined response. Alarm ownership, escalation, communications, guard deployment, law-enforcement coordination, visitor management, key and credential control, maintenance, and drills are part of the physical security system. CISA’s physical-security guidance repeatedly emphasizes understanding risk, planning, training, and layered protective measures.

    A useful timing model compares adversary progress with detection, assessment, communication, and response. Delay measures are valuable when they create enough time for a reliable response; delay without detection may simply postpone an unnoticed intrusion.

    Design and procurement checklist

    1. Define assets, threats, vulnerabilities, consequences, and operational constraints.
    2. Map public, controlled, restricted, and critical zones.
    3. Coordinate architecture, security, fire safety, accessibility, and emergency egress.
    4. Specify tested performance standards and the exact configurations required.
    5. Integrate detection, assessment, communications, and response procedures.
    6. Protect networked security devices and management platforms from cyber compromise.
    7. Commission the installed system with realistic tests, including degraded and emergency modes.
    8. Inspect, maintain, audit, and update the design as threats and operations change.

    FAQ

    Is a tall fence enough to secure a site?
    No. A fence can define a boundary and add delay, but gates, terrain, climb aids, surveillance, detection, lighting, inspection, and response determine the effectiveness of the perimeter.

    What is the difference between ballistic-resistant and blast-resistant construction?
    Ballistic resistance addresses projectile threats; blast resistance addresses pressure, impulse, fragments, and structural response. They require different tests and engineering.

    Do crash-rated bollards work in every installation?
    No. The tested barrier configuration, foundation, spacing, approach conditions, utilities, and installation quality all matter. The selected rating must match the design threat.

    Should security doors fail safe or fail secure?
    That decision depends on life-safety codes, occupancy, threat, operational requirements, and emergency procedures. Egress must never be treated as an afterthought.

    Conclusion

    Physical security works as a system of layers rather than a catalog of products. Fences, barriers, doors, sensors, surveillance, and ballistic-resistant assemblies each have a role, but their value depends on risk-based selection, tested performance, integration, and a credible human response. The strongest design is the one that protects the mission while preserving safety, accessibility, and normal operations.

    Sources and verification

    Verification note: No barrier, ballistic, forced-entry, blast, or detection rating is claimed for a specific product. Project requirements must reference current standards, the tested configuration, local codes, and qualified engineering.

  • Distributed Fiber Optic Sensing Explained

    Distributed Fiber Optic Sensing Explained

    Distributed fiber optic sensing (DFOS) turns an optical fiber into a continuous measurement line rather than using isolated electronic sensors at individual points. An interrogator launches light into the fiber and analyzes light that is scattered back from locations along the route. Because the return signal is associated with distance, one cable can provide spatially resolved information across a long asset.

    DFOS is an umbrella term. The three most common families are distributed acoustic sensing (DAS), distributed temperature sensing (DTS), and distributed strain sensing (DSS or DTSS when strain and temperature are measured together). They share an optical measurement architecture, but they do not measure the same physical quantity and should not be treated as interchangeable.

    How distributed fiber sensing works

    A typical system contains a sensing fiber or fiber-optic cable, an optoelectronic interrogator, signal-processing software, and an application layer that turns measurements into alarms, trends, or engineering information. The interrogator sends controlled optical pulses or frequency sweeps into the fiber. Microscopic variations in the glass scatter a small portion of the light back toward the instrument. By measuring the timing and characteristics of that return, the system estimates where a change occurred and what type of response the selected sensing method can reveal.

    This architecture is different from a string of conventional point sensors. The fiber itself provides measurement coverage along its route, while active electronics can remain at an accessible endpoint. However, the cable, installation method, coupling to the monitored asset, interrogation method, processing, and acceptance testing all influence performance.

    Rayleigh, Raman, and Brillouin scattering

    DFOS technologies are often described by the optical scattering mechanism they analyze. Rayleigh scattering is elastic scattering caused by small refractive-index variations in the fiber. Phase-sensitive Rayleigh techniques are widely associated with DAS because dynamic strain from vibration or acoustic energy changes the returned optical phase pattern.

    Raman scattering produces Stokes and anti-Stokes components. The relationship between those components is temperature-sensitive, which is why Raman-based systems are commonly used for distributed temperature measurement. Brillouin scattering is sensitive to both strain and temperature and is used in distributed strain and temperature measurements. A valid design must account for cross-sensitivity when the measurement responds to more than one physical quantity.

    DAS: distributed acoustic sensing

    DAS measures dynamic strain along the fiber and converts it into spatially resolved vibration or acoustic information. Security applications include perimeter activity detection, excavation and third-party-interference monitoring, and event awareness along pipelines, railways, borders, or other linear assets. Engineering applications include train tracking, traffic observation, seismic acquisition, and machinery-related monitoring.

    DAS does not literally turn fiber into a conventional microphone at every point. Its response depends on how strain is transferred into the cable, the orientation and frequency content of an event, environmental noise, optical conditions, gauge length, processing, and classification logic. A cable loosely placed in a duct may behave very differently from one mechanically coupled to a fence, buried beside a pipeline, or bonded to a structure.

    DTS: distributed temperature sensing

    DTS provides a temperature profile along the sensing route. Applications include fire and heat detection in tunnels, cable trays, conveyors, warehouses, and industrial facilities; thermal monitoring of power cables; process-vessel and well monitoring; and observation of heat movement in environmental and geotechnical studies.

    The U.S. Environmental Protection Agency describes fiber-optic DTS as a technique used in hydrogeological work to collect spatially and temporally dense temperature information. IEC 61757-2-2 specifies distributed temperature measurement by fiber-optic sensors. Those sources reinforce an important point: DTS is a measurement technology, while an alarm or diagnosis depends on application-specific thresholds, calibration, installation, and interpretation.

    DSS and distributed strain/temperature sensing

    Distributed strain sensing maps changes in strain along a fiber and can support structural and geotechnical monitoring. Use cases include deformation monitoring in tunnels, bridges, dams, slopes, foundations, pipelines, and other civil assets. Brillouin-based measurements may respond to both strain and temperature, so system design may require compensation, reference sections, or another way to separate the effects.

    Static or slowly changing strain measurement is not the same task as detecting fast vibration with DAS. Selection should begin with the measurand and required time behavior, not with the generic label “fiber sensing.”

    Where DFOS adds value

    • Long linear coverage: one sensing route can observe conditions across assets where dense point-sensor deployment would be difficult.
    • Passive field element: the optical fiber requires no electrical power at each measurement location.
    • Remote interrogation: active equipment can be placed in a controlled location while the cable follows a hazardous, remote, or inaccessible asset.
    • Spatial context: measurements can be displayed by distance, helping operators localize and compare events.
    • Multi-purpose infrastructure: in some projects, suitable existing fiber may support sensing, but feasibility must be confirmed through fiber characterization and field trials.

    Design limitations and trade-offs

    Performance figures are not universal. Sensing reach, spatial resolution, temperature or strain resolution, acoustic bandwidth, localization accuracy, and probability of detection depend on the interrogator, fiber and cable, optical loss, measurement settings, environment, installation geometry, and signal-processing requirements. Improving one parameter can reduce another; for example, longer reach or faster sampling may involve a resolution or signal-quality trade-off.

    DFOS also produces large data streams. A practical deployment needs alarm zoning, event classification, health monitoring, time synchronization, cybersecurity, retention rules, and integration with systems such as SCADA, GIS, video management, or security operations platforms. Site acceptance testing should use representative events and operating conditions rather than relying only on a laboratory specification.

    How to specify a DFOS project

    1. Define the physical quantity to measure: dynamic strain, temperature, static strain, or a combination.
    2. Describe the credible events and the response workflow after detection.
    3. Map the asset, fiber route, available fibers, splices, connectors, and expected optical loss.
    4. Design cable placement and mechanical or thermal coupling for the application.
    5. Set measurable acceptance criteria without assuming vendor claims are transferable between sites.
    6. Test representative events, background conditions, fault states, and integration paths.
    7. Plan ongoing calibration, model tuning, maintenance, and change control.

    FAQ

    Can ordinary telecommunications fiber be used for distributed sensing?
    Sometimes. Dark fiber or spare fibers may be usable, but cable construction, routing, splices, optical loss, access, and coupling to the monitored environment must be assessed. A communications route that is excellent for data transmission is not automatically a good sensing installation.

    Are DAS, DTS, and DSS interchangeable?
    No. DAS is generally used for dynamic strain and vibration, DTS for temperature, and DSS for distributed strain. The interrogator, processing, cable design, and installation must match the measurand.

    Does DFOS eliminate conventional sensors?
    Not necessarily. Point sensors may provide direct measurements, local redundancy, or calibration references. Hybrid architectures often combine distributed and point sensing.

    Can one fiber support both communications and sensing?
    Some architectures can share infrastructure or use different fibers within the same cable, but optical compatibility, network ownership, operational risk, and performance must be engineered and tested.

    Conclusion

    Distributed fiber optic sensing provides a powerful way to observe temperature, strain, vibration, and acoustic activity along extended assets. Its value comes from continuous spatial coverage and a passive sensing medium, not from a universal performance guarantee. Successful projects begin by selecting the correct sensing family, engineering the fiber’s relationship to the asset, and validating the complete detection-to-response workflow under real conditions.

    Sources and verification

    Verification note: No product-specific sensing range, resolution, accuracy, channel count, or detection-performance claim is presented. Those values must be verified for the selected interrogator, fiber, installation, and application.