Category: News

Current, event-driven reporting, announcements and industry developments.

  • Cohere and Aleph Alpha Finalize $20B Merger to Build ‘Sovereign AI’ Alternative

    Cohere and Aleph Alpha Finalize $20B Merger to Build ‘Sovereign AI’ Alternative

    Canada’s Cohere and Germany’s Aleph Alpha signed a definitive merger agreement, combining into a single business that will operate under the Cohere name with dual headquarters in Toronto and Berlin. Aleph Alpha’s Heidelberg office will focus on research under the combined company, and Aleph Alpha co-chief Ilhan Scheer becomes chief operating officer of the merged entity.

    Lidl parent Schwarz Group is investing 500 million euros in the combined company as part of the deal, which was first disclosed in April 2026 at an estimated $20 billion valuation. The transaction remains subject to regulatory approval. Cohere chief executive Aidan Gomez said the merger is meant to meet demand from government and enterprise customers for AI systems that are “powerful enough to compete, but secure and governable enough to trust,” particularly customers wanting data residency and independence from US cloud providers.

    Why it matters

    Governments and regulated industries in Europe have been pushing for AI infrastructure they can host and control domestically rather than relying on US hyperscalers — a combined Cohere-Aleph Alpha is explicitly positioning itself to serve that “sovereign AI” demand.
    Sources

  • King Charles Convenes Nvidia, OpenAI, Anthropic and DeepMind Leaders for AI Safety Summit

    King Charles Convenes Nvidia, OpenAI, Anthropic and DeepMind Leaders for AI Safety Summit

    King Charles III hosted senior leaders from Nvidia, OpenAI, Google DeepMind and Anthropic at Dumfries House in Ayrshire, Scotland, for a summit on AI safety organized by the Ditchley Foundation. Reported attendees included Nvidia chief executive Jensen Huang, Google DeepMind founder Demis Hassabis and OpenAI chief financial officer Sarah Friar.

    Discussion topics reportedly included whether the AI industry needs a shared code of conduct and how autonomous AI agents can be advanced responsibly. The gathering is a separate, multi-stakeholder dialogue distinct from the public disagreement between Nvidia’s Huang and Anthropic and OpenAI executives over the pace of AI safety measures reported earlier this week.

    Why it matters

    A UK monarch-convened, closed-door summit signals that governments outside the US are trying to build their own channels of influence over frontier AI labs’ safety practices, rather than leaving the conversation entirely to Washington and the companies themselves.

    Sources

  • Ransomware Attacks on Manufacturers Rose Nearly 40% in First Half of 2026, Report Finds

    Ransomware Attacks on Manufacturers Rose Nearly 40% in First Half of 2026, Report Finds

    Cyber-risk intelligence firm Black Kite reported 1,183 manufacturing-sector ransomware victims in the first seven months of 2026, a nearly 40% increase year-over-year, with attacks on the sector more than doubling since 2023. Manufacturing accounted for 22% of all 7,551 ransomware disclosures the firm tracked across all industries in the period.

    The report found newer ransomware groups — including The Gentlemen, which alone claimed 142 manufacturing victims, along with Qilin, Akira, DragonForce and INC Ransom — have displaced the threat-actor groups that previously dominated the sector. Black Kite said 73% of attacks hit mid-market companies, with a median victim revenue of $42.9 million, and that European victim counts rose 85.4% year-over-year while the US share of global victims fell from 52.3% to 34.8%.

    Why it matters

    The shift toward mid-market manufacturers suggests attackers are increasingly targeting companies that may have less mature security operations than large enterprises but still enough revenue — and enough dependence on continuous production — to make ransom payment attractive.

    Sources

  • Airwise and UAS Sentry Integrate Remote ID Drone Detection Into Airspace Platform

    Airwise and UAS Sentry Integrate Remote ID Drone Detection Into Airspace Platform

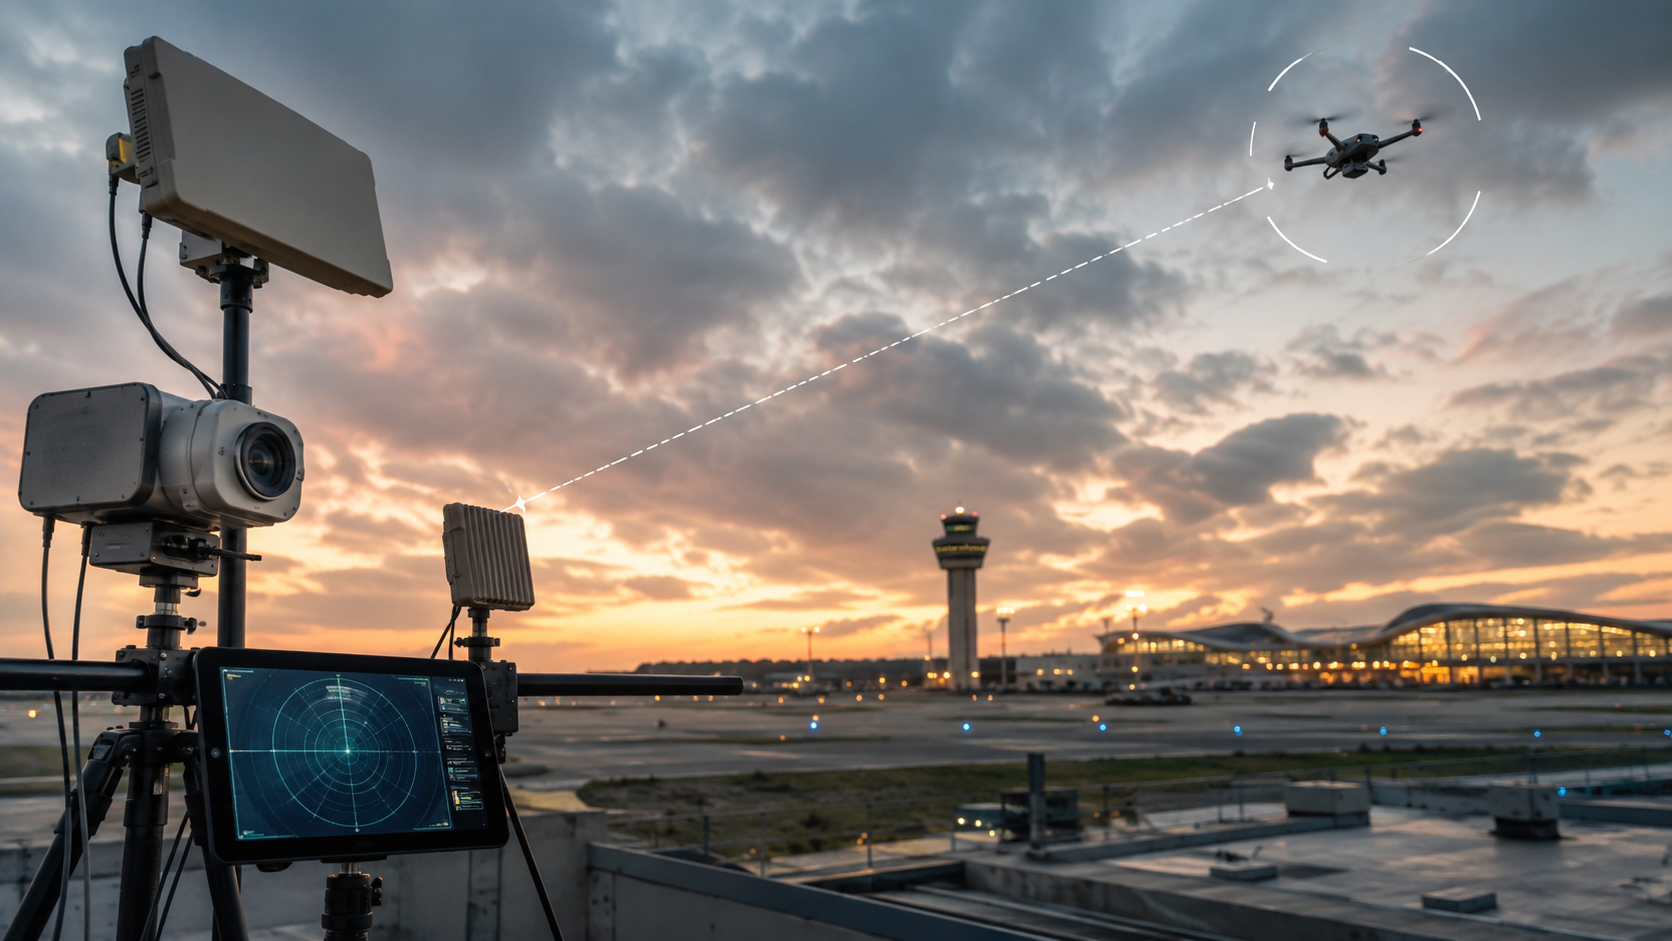
    Airwise Solutions and UAS Sentry announced a partnership integrating UAS Sentry’s Nexus Remote ID drone-detection capability into Airwise’s Nexus operational airspace platform. The integration displays detected Remote ID signals from nearby drones alongside an organization’s own drone operations, airspace data, mission activity, telemetry, FAA services and weather in a single operating picture.

    The companies are targeting critical infrastructure operators, utilities, energy sites, public-safety agencies, airports and industrial facilities that need visibility into unauthorized drone activity in their airspace — not just their own fleet’s operations.

    Why it matters

    Remote ID data gives facility operators a legal, standards-based way to see who is flying a drone nearby without deploying their own detection hardware, which lowers the barrier to basic airspace awareness for sites that can’t justify a full counter-UAS system.

    Sources

  • Hardcoded Cryptographic Keys in Wärtsilä Ship Management Software Rated Critical

    Hardcoded Cryptographic Keys in Wärtsilä Ship Management Software Rated Critical

    CISA disclosed two critical vulnerabilities in Wärtsilä FOS-Onboard, fleet-management software used aboard vessels, after the flaws were reported by maritime cybersecurity firm Cydome Security. CVE-2026-78225, rated 9.1 to 9.5 depending on scoring version, is a hardcoded cryptographic server key in the software’s Update Controller component that could let an attacker deliver an unauthorized software update or execute code on affected systems.

    A second flaw, CVE-2026-81855, is a hardcoded client authentication key in a robot-testing-framework component that could let an attacker extract credentials and impersonate a privileged client. Wärtsilä said the vulnerabilities are not exploitable under its recommended installation configuration and has made a patch available to customers on request. CISA lists the affected sector as Transportation Systems, with deployment worldwide.

    Why it matters

    Hardcoded keys are a recurring failure mode in operational technology because they can’t be rotated the way a normal credential can — once exposed, every deployed unit sharing that key is affected until firmware is patched.

    Sources

  • DroneShield Fields Vehicle-Mounted Counter-Drone System on US Army Infantry Squad Vehicles

    DroneShield Fields Vehicle-Mounted Counter-Drone System on US Army Infantry Squad Vehicles

    DroneShield said it has completed installation and operational acceptance of its DroneSentry-X Mk2 counter-drone system on US Army Infantry Squad Vehicles, reaching the milestone roughly 80 days after the contract was awarded under Joint Interagency Task Force 401. The installation process included fitting the system to the vehicles, a live-drone acceptance test and operator training, establishing what the company calls initial operational capability.

    Unlike fixed-site counter-drone installations, the vehicle-mounted system is designed to give mobile forces detection and electronic-countermeasure capability against drones while on the move. DroneShield said three additional DroneSentry-X Mk2 units are planned under a recent contract modification.

    Why it matters

    Mobile counter-drone capability addresses a gap that fixed installations can’t: forces operating away from a base still face the same low-cost drone threats that have driven counter-UAS investment at airports, stadiums and critical infrastructure sites.

    Sources

  • Critical Flaw in Siemens Reyrolle Grid Protection Relays Allows Authentication Bypass

    Critical Flaw in Siemens Reyrolle Grid Protection Relays Allows Authentication Bypass

    CISA published an advisory disclosing 14 vulnerabilities in Siemens Reyrolle 7SR5 protection relays, devices used in electrical substations worldwide to detect faults and trigger circuit breakers. The most severe, CVE-2026-62645, carries a CVSS score of 9.8 out of 10 and stems from the relay’s web interface exposing information that lets an attacker calculate current and past session IDs — enough to bypass authentication entirely without any privileges or user interaction.

    The advisory also describes a related flaw allowing predictable session-ID generation from insufficient entropy, an out-of-bounds write reachable through crafted URLs that can force the device to reboot, and a physical-access vector that could allow unsigned code execution through a maintenance-mode key sequence. Siemens has released firmware version 2.70 to address the vulnerabilities; earlier versions remain exposed.

    Why it matters

    Protection relays are a core safety component of the electrical grid — an attacker who can bypass authentication on one gains the ability to interfere with fault detection and circuit-breaker operation, which is exactly the kind of access that grid-security planners worry about most.

    Sources

  • At GSX 2026, Security Executives Push Back Against AI Hype in Favor of Practical Results

    At GSX 2026, Security Executives Push Back Against AI Hype in Favor of Practical Results

    On the second day of GSX 2026 in Atlanta, Security Info Watch interviewed seven security-industry executives about what customers and partners are actually asking for on the show floor. The consistent theme across the conversations: integration and day-to-day usability concerns are outweighing pure AI-feature hype, and reliable service delivery remains the top purchasing driver for many buyers.

    Executives also pointed to longer-term questions emerging about the future of access-control credentials as AI capabilities proliferate across security systems, suggesting the next wave of purchasing decisions may hinge less on which vendor has the most AI features and more on which systems integrate cleanly with what customers already operate.

    Why it matters

    The pushback signals that buyers in physical security are becoming more discerning about AI claims after two years of heavy marketing around the technology, which could shift vendor competition toward integration quality and service reliability rather than feature lists.

    Sources

  • Robotics Startup Splan Debuts SENA Visitor and Access Robot at GSX 2026

    Robotics Startup Splan Debuts SENA Visitor and Access Robot at GSX 2026

    Robotics startup Splan introduced SENA — short for Smart Entry & Navigation Assistant — at GSX 2026 in Atlanta, an AI-powered robot designed to handle visitor registration, identity verification, guard tours and incident management at building entrances. The unveiling was among the AI-focused product debuts on the opening day of the show, which drew more than 500 exhibitors to the Georgia World Congress Center.

    According to trade-press coverage of the show floor, SENA is positioned to work alongside human guards rather than replace them, automating repetitive front-desk and patrol tasks so staff can focus on higher-judgment security decisions. The launch reflects a broader theme at this year’s GSX: multiple exhibitors showed AI systems meant to move beyond simple event detection toward actively assisting with day-to-day security operations.

    Why it matters

    Visitor-management and reception robots are one of the more visible test cases for how far building owners are willing to let autonomous systems handle identity verification — a function with real liability and access-control consequences if it gets a decision wrong.

    Sources

  • Italian Startup Exein Hits $1.7B Valuation to Secure ‘Physical AI’ Robots and Drones

    Italian Startup Exein Hits $1.7B Valuation to Secure ‘Physical AI’ Robots and Drones

    Rome-based cybersecurity startup Exein raised $270 million in an oversubscribed funding round, pushing its valuation to $1.7 billion and making it Europe’s most valuable cybersecurity company, the company said this week. The round was led by Headline, with participation from Sofina, Goldman Sachs, the EIB Group’s European Tech Champions Initiative and KfW Capital, among others.

    Exein’s Photon runtime-security platform already secures more than 2 billion connected devices across industrial automation, automotive, energy, healthcare, aerospace and semiconductor manufacturing. The company said it plans to use the new capital to build a proprietary foundation model aimed specifically at securing “Physical AI” systems — industrial robots, drones and autonomous vehicles that increasingly run their own AI models at the edge — with a target release in the first quarter of 2027. Exein reported that annual recurring revenue roughly quadrupled in the first half of 2026 and said it will open a new office in the San Francisco Bay Area as part of a US and Asia-Pacific expansion.

    Why it matters

    As physical-security systems increasingly embed AI models directly on cameras, robots and industrial controllers rather than in the cloud, runtime security for those edge AI systems becomes a new attack surface that traditional endpoint or network security tools were not built to cover.

    Sources