Category: Access Control & Identity

Credentialing, biometrics, smart locks and identity verification technologies that control who can enter a facility.

  • ProdataKey and Aiphone Launch Integrated Cloud-Based Access Control and Video Intercom Solution

    ProdataKey and Aiphone Launch Integrated Cloud-Based Access Control and Video Intercom Solution

    ProdataKey (PDK) and Aiphone announced on August 26, 2026, a new cloud-based integration designed to unify access control and video intercom management for commercial and multi-tenant properties. The integration connects AiphoneCloud, Aiphone’s cloud-managed intercom platform, with PDK.io, ProdataKey’s mobile-first access control management software.

    “The future of physical security is built on connected, intuitive technologies,” said Dallan Labrum, Executive Vice President of Sales at ProdataKey. “Our integration with Aiphone gives dealers, integrators, and end users a smarter way to manage access control and video intercoms from a unified ecosystem. Together, we’re helping customers improve operational efficiency while delivering a better experience for everyone who enters and manages their buildings.”

    Automatic Tenant Sync Eliminates Duplicate Record-Keeping

    According to the companies, when tenant information is added, updated, or removed in PDK.io, those changes automatically sync to connected Aiphone IXG intercoms, eliminating the need for dealers and property managers to maintain duplicate records or manually coordinate directory updates between two separate systems. Security administrators and property managers can manage both access control and video intercom operations through a single streamlined workflow, which the companies say reduces administrative overhead and helps close security gaps caused by human error in manual record-keeping.

    The launch follows ProdataKey’s earlier preview of the integration at ISC West 2026, where the company showcased new locksets, readers, burglar-panel integrations, and video intercom offerings alongside the incoming Aiphone connection. For multi-tenant and commercial property operators, the combined platform reflects a broader industry shift toward converging previously siloed access control and visitor-verification systems into single-pane-of-glass management, reducing the operational friction that has historically accompanied maintaining separate vendor ecosystems for door access and intercom hardware.
  • Smart Gates and Vehicle Access Control

    Smart Gates and Vehicle Access Control

    Vehicle entrances are among the most complex points in physical security because they combine identity, traffic flow, safety and perimeter control. A modern smart gate must determine who or what is approaching, whether access is authorized and how to move vehicles through the site without creating congestion or unsafe conditions.

    Common technologies include license-plate recognition, RFID tags, mobile credentials, intercoms, loop detectors, radar, barriers, bollards and video analytics. High-security sites may also add under-vehicle inspection or guard verification.

    The most effective systems link the vehicle to an access policy. A recognized plate alone should not automatically be treated as proof of identity in every environment. The system may also verify a driver credential, delivery schedule, visitor record or vehicle classification.

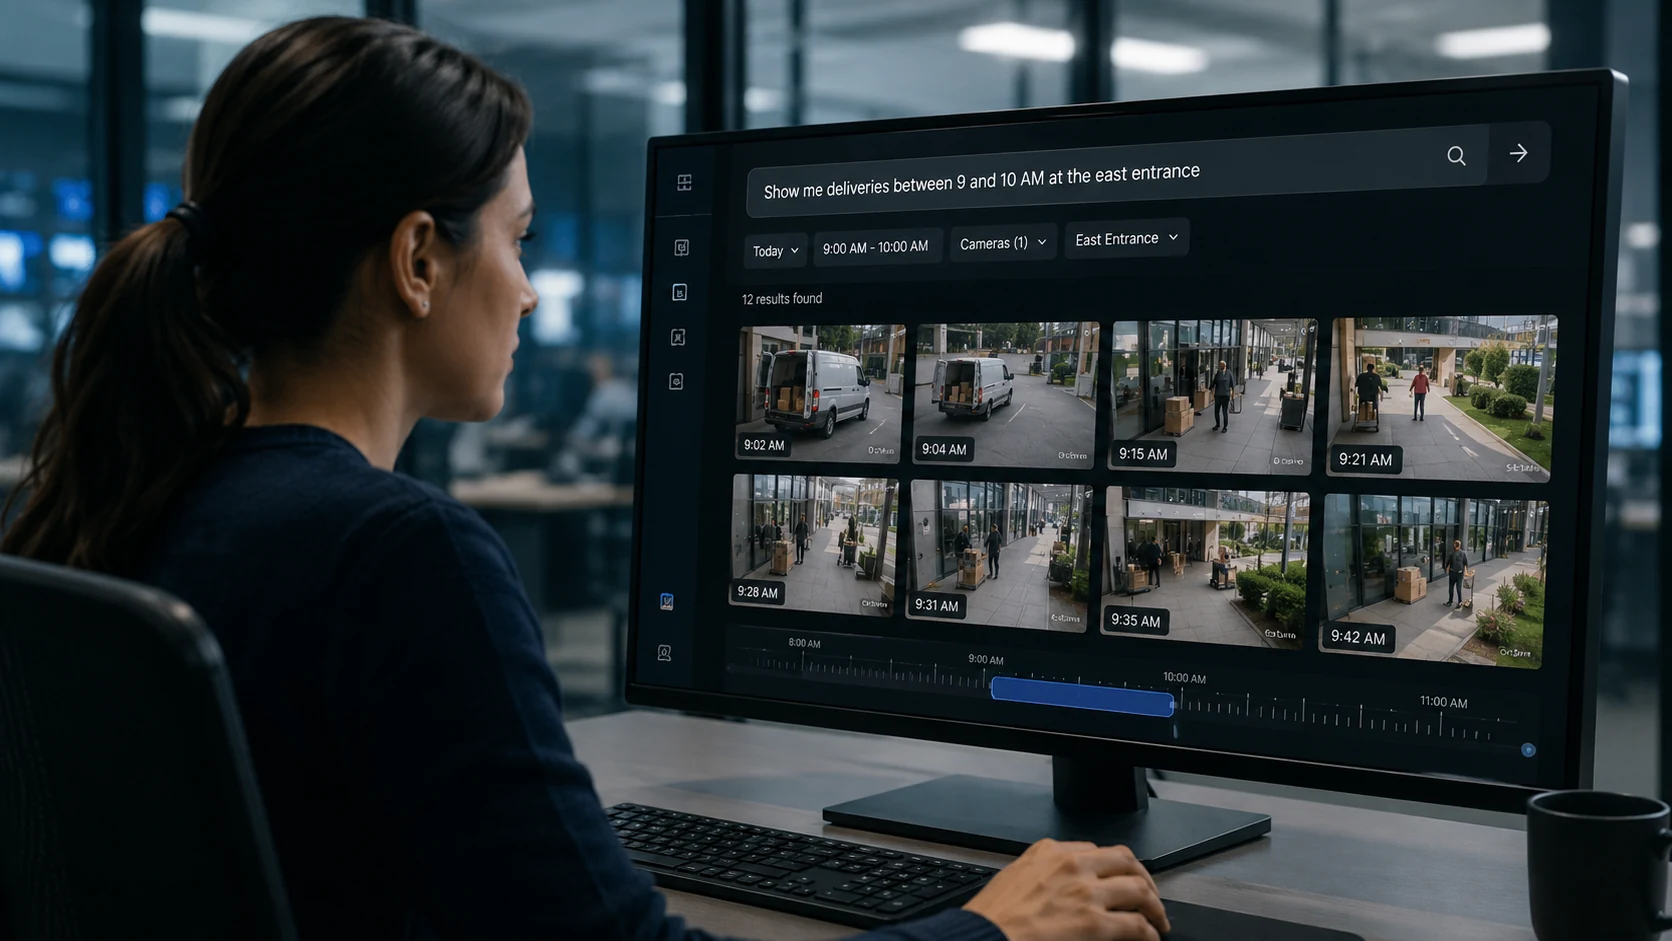
    Video plays a major role in evidence and exception handling. Cameras can document the vehicle, driver lane and surrounding context, while analytics can detect tailgating, wrong-way movement or a vehicle entering a restricted lane.

    Safety must be engineered alongside security. Barrier arms, gates and bollards require presence detection and safe operating logic to avoid collisions. Emergency egress and fire-service access also need dedicated procedures.

    For multi-site organizations, cloud-connected gate management can centralize credentials and audit logs. At critical infrastructure sites, local operation should remain available if connectivity fails.

    Smart vehicle access is therefore not one product but a coordinated system. The strongest designs combine identification, physical barriers, sensors, video and workflow software into one controlled entry process.

  • Zero Trust Meets Physical Access Control

    Zero Trust Meets Physical Access Control

    Contextual access

    Decisions can consider identity, role, employment status, time, location and area sensitivity rather than badge possession alone.

    Continuous lifecycle

    Authoritative identity data should update physical permissions quickly when employment or responsibilities change.

    Least privilege

    Users should receive only the buildings, floors and rooms required for current work.

    Stronger zones

    Higher-risk areas can require biometrics, PINs or dual authorization.

    Monitoring and convergence

    Unusual access patterns can prioritize investigation while cyber and physical identity systems share lifecycle controls.

    Conclusion

    Zero Trust modernizes access governance without requiring every reader to be replaced.

  • Wireless Smart Locks vs Wired Access Control

    Wireless Smart Locks vs Wired Access Control

    Wired access control

    Wired doors provide continuous power, predictable communication and real-time monitoring for critical openings.

    Wireless smart locks

    Battery-powered locks can reduce cabling and extend electronic access to existing buildings and interior doors.

    Operational trade-offs

    Wireless deployments require battery, radio coverage and firmware processes; wired systems require more installation work.

    Security considerations

    Encryption, credential protection, secure firmware and physical resistance matter in both architectures.

    Hybrid designs

    Many sites use wired systems at perimeters and critical rooms while applying wireless locks to lower-risk spaces.

    Conclusion

    The correct design matches each opening’s risk, environment and maintenance capability.

  • Contractor Access: The Hidden Weakness in Corporate Security

    Contractor Access: The Hidden Weakness in Corporate Security

    Why contractors create risk

    Contractors often sit outside normal HR lifecycle controls, so manually issued permissions can remain active after assignments end.

    Time-limited permissions

    Credentials should expire automatically and be restricted to necessary locations and working hours.

    Sponsorship and accountability

    Every contractor needs an accountable sponsor and individual credential; shared badges undermine investigations.

    Work-order integration

    Linking access to maintenance tickets or project schedules can suspend permissions automatically when work closes.

    Monitoring

    Dormant credentials, unusual hours and denied attempts deserve review.

    Conclusion

    Strong contractor identity governance closes a common gap in employee-focused access control.

  • Visitor Management Systems for Enterprise Security

    Visitor Management Systems for Enterprise Security

    Why visitor management matters

    Visitors sit outside the employee identity lifecycle, creating a temporary trust problem that requires a sponsor, purpose and expiration.

    Pre-registration and check-in

    Hosts can invite guests in advance and support proportionate identity verification on arrival.

    Temporary access credentials

    Integration with access control can issue time- and area-limited permissions instead of generic badges.

    Emergency accountability

    Accurate visitor presence records can support evacuation and incident response.

    Privacy and retention

    Visitor data needs defined retention, restricted access and transparent collection practices.

    Conclusion

    Effective visitor management connects reception, identity governance, access control and emergency procedures.

  • Passwordless Physical Access: Wallet Credentials and Digital Identity

    Passwordless Physical Access: Wallet Credentials and Digital Identity

    What passwordless means

    Users prove identity without entering a reusable secret. A device-bound credential protected by secure hardware and local authentication can provide stronger assurance than a badge alone.

    Wallet credentials

    Digital wallets support remote provisioning and central revocation tied to HR or identity lifecycle systems.

    Identity convergence

    A shared authoritative identity can govern application sign-in and physical entry, reducing duplicate records and improving auditability.

    Security and resilience

    Phone possession can be combined with biometric verification, while fallback processes remain necessary for dead batteries, lost devices and visitors.

    Conclusion

    Passwordless physical access is part of a broader shift toward unified cyber-physical identity governance.

  • Biometric Access Control: Fingerprint, Face, Iris and Palm

    Biometric Access Control: Fingerprint, Face, Iris and Palm

    Fingerprint

    Fingerprint readers are mature and compact, but dirty, wet or damaged fingers and hygiene concerns can affect performance and acceptance.

    Face recognition

    Contactless facial authentication can be fast, but depends on camera position, lighting, image quality and presentation-attack defenses.

    Iris recognition

    Iris patterns can support high-assurance matching, while specialized hardware and user positioning may increase complexity and cost.

    Palm and palm-vein systems

    Palm systems may use surface geometry or subsurface vein patterns. Contactless options can balance strong authentication with high-throughput operation.

    Use more than one factor

    Combining a biometric with a secure card or mobile credential reduces reliance on a single modality and provides a recovery path when authentication fails.

    Privacy and governance

    Biometric templates require encryption, retention limits, access controls, a lawful processing basis and reliable deletion procedures. Unlike a password, a biometric characteristic cannot simply be replaced.

    Conclusion

    There is no universally best modality. Selection should reflect risk, environment, throughput, privacy obligations and user experience.

  • Mobile Credentials: Smartphones as Security Badges

    Mobile Credentials: Smartphones as Security Badges

    Why adoption is growing

    Digital credentials can be issued remotely, updated without replacing a card and revoked quickly. This is valuable for distributed workforces, temporary personnel and multi-site organizations.

    Security advantages

    Credentials may be protected by device hardware and combined with biometric unlock, PIN protection or mobile-device management, adding controls unavailable to passive cards.

    User experience

    Performance depends on reader placement, phone models, battery state and whether NFC, Bluetooth Low Energy or wallet technology is used. Representative testing is essential.

    Operational considerations

    Organizations need processes for lost phones, replacement devices, offboarding and visitors. Mobile credentials can coexist with cards during a phased transition.

    Privacy and ownership

    Bring-your-own-device deployments need clear boundaries and data minimization so physical access does not become unnecessary tracking.

    Conclusion

    The value of mobile access extends beyond convenience to lifecycle management, flexible identity integration and stronger authentication choices.

  • IP-Based Access Control: Architecture and Advantages

    IP-Based Access Control: Architecture and Advantages

    How the architecture works

    Credential readers, controllers, locks and request-to-exit devices connect with management software through standard networks. Controllers should retain local permissions and decision-making when connectivity is interrupted.

    Why organizations choose IP

    IP architectures can simplify multi-site administration, health monitoring, firmware management and integration. Existing structured cabling may reduce installation complexity in suitable buildings.

    Cybersecurity responsibilities

    Controllers require encrypted communication, unique credentials, secure firmware, segmentation and controlled administrative access. A physically protected but poorly configured device can still create cyber risk.

    PoE and edge intelligence

    Power over Ethernet can deliver power and data over one cable. Edge-capable controllers can preserve permissions and event logs locally to support continuity during network outages.

    Where it fits

    Campuses, data centers, logistics sites and distributed enterprises often benefit, especially when IT and security teams already manage converged infrastructure.

    Conclusion

    IP access control changes deployment and governance, not just connectivity. Sound network design can make physical access more scalable, observable and interoperable.