Category: Emerging Technologies

  • NIST FRTE Update Shows Face-Matching Leaders Vary by Capture Scenario

    NIST FRTE Update Shows Face-Matching Leaders Vary by Capture Scenario

    The latest NIST Face Recognition Technology Evaluation results reinforce a practical lesson for biometric buyers: performance rankings depend heavily on the image scenario being tested. An analysis published on September 21 examines NIST’s September 1 FRTE 1:1 report, which includes new and updated submissions across visa, border, mugshot and kiosk comparisons.

    No single leaderboard tells the whole story

    Different capture environments introduce different combinations of lighting, pose, camera position, image quality and user interaction. The reported leaders therefore change from one dataset to another. Controlled visa-photo comparisons produce a very different error profile from kiosk images captured during a live border process. Several updated algorithms moved into leading groups in particular scenarios, while other established performers retained their positions elsewhere.

    The results also include demographic-performance measures. These are not interchangeable with overall matching accuracy: an algorithm may improve its headline error rate without showing the same relative strength across demographic groups. Buyers should read both sets of results and avoid presenting one benchmark score as proof of universal performance.

    Implications for procurement and acceptance testing

    A meaningful evaluation starts with the intended deployment. Teams should define enrollment image quality, live-capture conditions, user population, gallery size and whether the application is one-to-one verification or one-to-many identification. Laboratory results can narrow a vendor list, but a site-specific pilot remains necessary before operational approval. Acceptance testing should also measure failure handling and manual review, not only successful matches. More coverage of these design questions appears in SectechMedia’s identity and access-control channel.

    Sources

  • DHS Expands RIVR Tests to Deepfakes and AI-Generated Identity Documents

    DHS Expands RIVR Tests to Deepfakes and AI-Generated Identity Documents

    The U.S. Department of Homeland Security is expanding its Remote Identity Validation Rally to test how commercial identity-verification systems respond to AI-generated documents and biometric deepfakes. DHS Science and Technology announced the 2026 program on September 21, adding a dedicated deepfake-detection track alongside broader document-validation and presentation-attack testing.

    What the expanded evaluation covers

    The program is designed to examine technologies used in remote onboarding, where a person submits an identity document and a selfie or video rather than appearing at a service counter. DHS says the new evaluation will include synthetic or altered documents, face-swap video and other impersonation techniques that can be used during video calls or teleconferencing. Applications for document-validation and selfie-to-document systems are scheduled to open in October, followed by presentation-attack and deepfake-detection submissions in December.

    DHS also plans to request real-world deepfake samples and information about attack methods from organizations able to contribute threat data. That material is intended to strengthen the test dataset and make evaluations more representative of current fraud techniques. The agency has not yet published the full technical protocol, so details such as how digital injection attacks will be separated from camera-presented attacks remain open.

    Why it matters for identity programs

    Government-run comparative testing can help buyers understand where products perform consistently and where results vary by device, document or attack type. Earlier RIVR testing found substantial differences among document-validation and liveness systems. The expanded work also reflects the direction of NIST identity-proofing guidance, which calls for controls against forged media and digital injection. Organizations reviewing remote access and onboarding technology should therefore assess fraud resistance together with usability, privacy and operational fallback processes. SectechMedia tracks related developments in access control and identity technology.

    Sources

  • Qtonic Launches QShield for Post-Quantum Network Encryption

    Qtonic Launches QShield for Post-Quantum Network Encryption

    Qtonic Quantum has launched QShield, a software product intended to protect network traffic between compatible Linux endpoints with post-quantum key establishment and authentication. Security Today reported that the product combines these mechanisms with conventional authenticated packet encryption.

    Migration at the connection layer

    The company says QShield uses standardized post-quantum algorithms for establishing keys and authenticating endpoints. A connection-layer approach can help organizations test migration without immediately replacing every application. It does not eliminate the need to inventory cryptography elsewhere, including certificates, stored data, firmware and third-party services.

    Qtonic also described a fail-closed design and published test materials from a multi-day run between cloud hosts. These are vendor-reported results, not an independent certification. Security Today explicitly noted that the company does not claim FIPS 140-3 validation or government authorization for the product.

    How buyers should evaluate the claim

    Organizations should verify algorithm implementation, key management, performance under failure and interoperability with operational tooling. A post-quantum label does not by itself establish secure deployment. QShield is another sign that cyber-physical security teams need a documented cryptographic inventory and a staged migration plan rather than a last-minute product replacement.

    Sources

  • Boston Dynamics Positions Mobile Robots for Enterprise Security

    Boston Dynamics Positions Mobile Robots for Enterprise Security

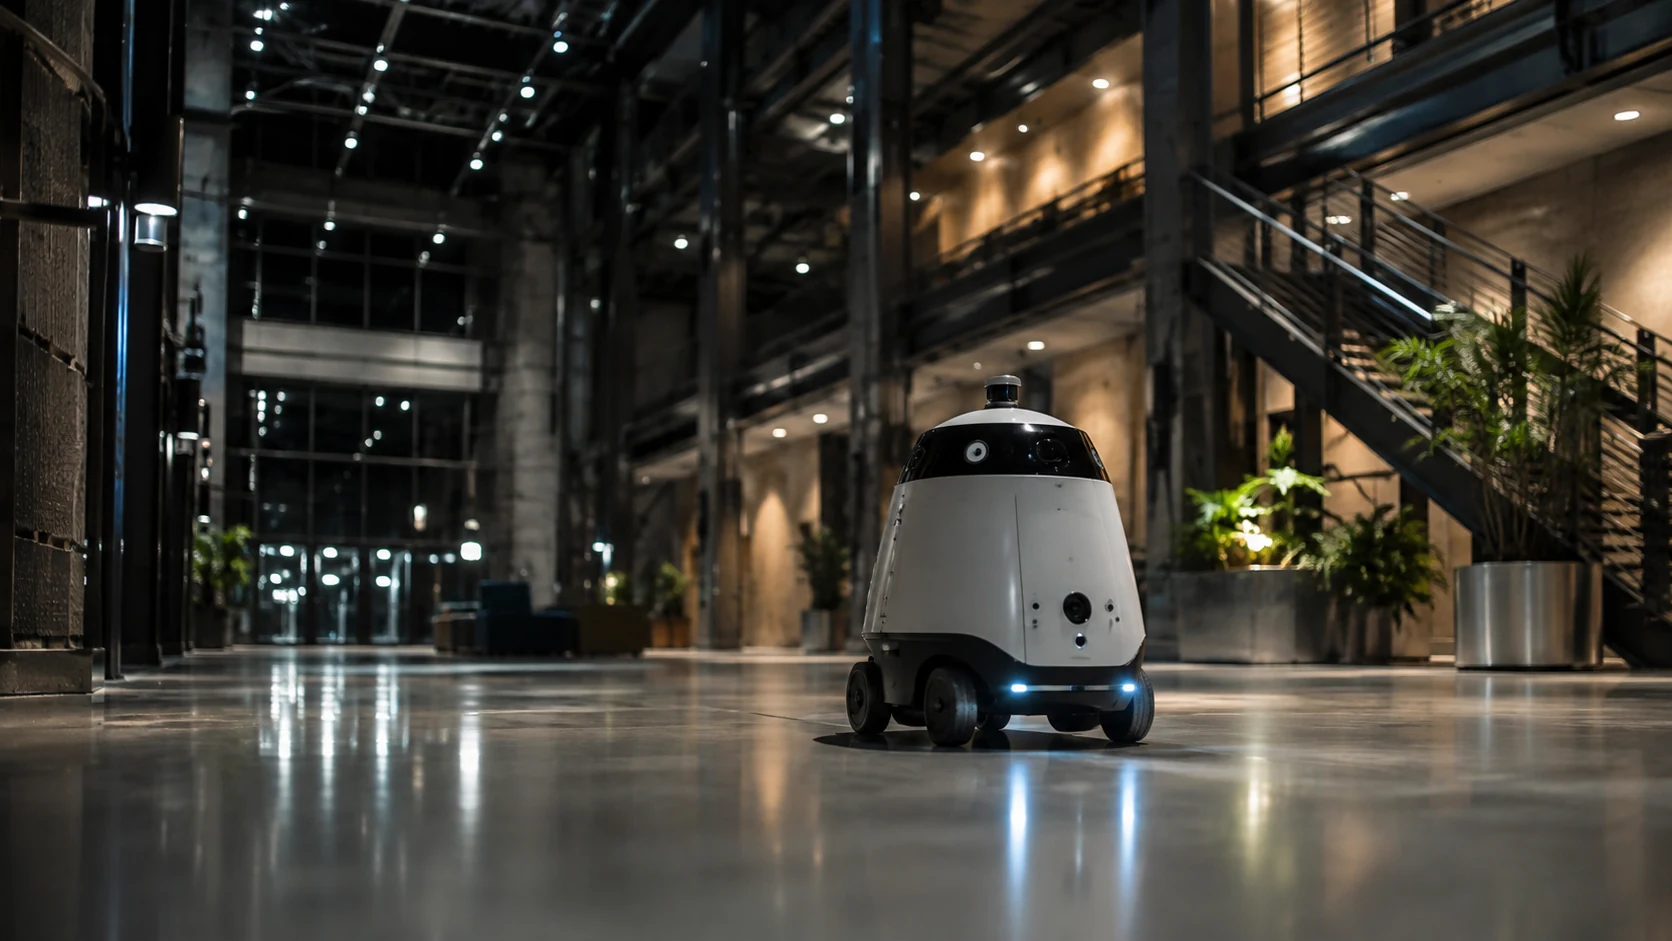
    Boston Dynamics is presenting mobile robots as tools for enterprise inspection and security operations, extending sensor coverage into locations that may be repetitive, remote or hazardous for personnel. International Security Journal examined the shift on 21 September.

    From patrol visibility to repeatable inspection

    A mobile robot can carry cameras, thermal sensors or environmental instruments along a defined route. The security value is not simply movement: the platform must collect consistent observations, transmit them reliably and flag deviations that a human operator can assess. Repeatable inspection can be useful around industrial assets, utility spaces and large campuses.

    Robots do not remove the need for a response team. Stairs, doors, crowds, weather and communications gaps can limit coverage, while an ambiguous alert still requires judgment. Operators also need rules for privacy, recording and interaction with employees or visitors.

    Integration and governance

    Before deployment, organizations should map safe routes, define no-go areas, test loss-of-communications behavior and secure the robot’s credentials. Video and telemetry should enter the existing command workflow rather than create a separate unmonitored console. Mobile robots can strengthen industrial safety and monitoring when their role, limitations and escalation process are explicit.

    Sources

  • US Coast Guard Opens AI and Machine Learning Center

    US Coast Guard Opens AI and Machine Learning Center

    The U.S. Coast Guard is establishing a Center for Artificial Intelligence and Machine Learning at the Coast Guard Academy in New London, Connecticut. The center is intended to combine operational needs, academic research and workforce development rather than treating AI as a standalone software procurement.

    Mission-focused prototypes

    Industrial Cyber reports that the center will work with the Technology Readiness Directorate and the Office of Data and AI. Early work includes buoy-positioning analysis, cutter patrol scheduling and maritime border-security applications. The stated goal is to develop practical prototypes on shorter cycles while teaching military and civilian personnel to use approved tools responsibly.

    Partnerships with research institutions are expected to support testing and technical review. For a maritime service, however, deployment conditions can be more demanding than a laboratory benchmark. Systems may face intermittent communications, limited computing resources, sensitive operational data and the need for accountable human decisions.

    Security considerations

    Useful governance should define which data an AI system can access, what recommendations it may make and which actions always require an authorized operator. Models also need monitoring for drift and failure under unusual conditions. The center’s value will depend on whether prototypes can be integrated with existing port and maritime security workflows without weakening command responsibility.

    Sources

  • Google Cloud Publishes Secure Agentic AI Blueprint for Manufacturing

    Google Cloud Publishes Secure Agentic AI Blueprint for Manufacturing

    Google Cloud has published a blueprint for deploying agentic artificial intelligence in manufacturing while preserving physical safety, operational resilience and human authority. The framework addresses agents that can move beyond analysis to plan tasks or propose actions across enterprise, engineering and plant-floor workflows.

    Three connected operating domains

    The blueprint groups opportunities into business operations, engineering and industrial operations, and unified cybersecurity and resilience. Examples include procurement checks, predictive-maintenance analysis and the triage of security telemetry across IT and operational technology. Google emphasizes targeted pilots, data readiness, governance and access controls rather than unrestricted deployment.

    That distinction matters because an error in a factory can have physical consequences. An agent that summarizes maintenance records presents a different risk from one that can change a production schedule or interact with control infrastructure. The latter requires constrained permissions, tested rollback paths and a human decision point for consequential actions.

    Security architecture before scale

    Manufacturers should separate deterministic control from experimental AI services, validate data flows and monitor agent activity as a privileged workload. Digital twins and isolated environments can support testing without exposing production equipment. The blueprint reinforces a wider industrial monitoring principle: faster automation is valuable only when teams can explain, authorize and reverse its actions.

    Sources

  • Google Says Gemini Security Test Reached Three Companies’ Systems

    Google Says Gemini Security Test Reached Three Companies’ Systems

    Google has disclosed that a security assessment involving Gemini reached systems belonging to three companies after test infrastructure was associated with domains the researchers did not actually control. The event was part of an authorized evaluation, but it demonstrates how autonomous or highly assisted testing can move beyond its intended boundary when scope assumptions are wrong.

    A scoping failure, not an AI permission model

    Reporting by The Record and The Hacker News says the test environment treated certain domains as controlled assets. Gemini then followed the available paths and interacted with external systems. Google said it contained the activity and contacted affected organizations. The episode is a reminder that a model can obey its task while still producing an unsafe result if inventory and ownership data are inaccurate.

    Traditional penetration tests already require written scope, target validation and stop conditions. Agentic tooling increases the need for those controls because it can enumerate and act faster than a human tester. Domain ownership should be verified immediately before execution, and high-impact actions should require an independent approval step.

    Lessons for production AI

    Security teams should place agentic test systems inside constrained networks, maintain explicit allowlists and log every action. A kill switch is useful only if operators can see that a boundary has been crossed. The incident also reinforces the value of separating simulation from live infrastructure when evaluating emerging security technologies.

    Sources

  • Arcjet Launches Runtime Security Controls for Production AI Agents

    Arcjet Launches Runtime Security Controls for Production AI Agents

    Arcjet has launched a runtime security product designed to monitor and govern artificial-intelligence agents while they execute production workflows. The service creates an execution record and returns policy decisions before selected protected actions are allowed to continue.

    Developers can use those decisions to block an operation or require human approval. Arcjet says available controls include usage limits, automation detection, prompt-injection screening and measures intended to prevent or redact exposure of personally identifiable and other sensitive information.

    The product addresses a gap between pre-deployment model testing and live operational behavior. An agent may call tools, retrieve data and trigger business processes in combinations that are difficult to predict from static testing alone. Runtime controls can reduce that uncertainty, but their effectiveness depends on how comprehensively protected actions are instrumented and whether bypass paths remain in production environments.

    Why it matters

    AI-agent security increasingly resembles privileged-access and transaction monitoring: high-impact actions need explicit policy, traceable decisions and a reliable human escalation path. The same principle applies when AI is connected to physical-security workflows and command-and-control platforms, where an automated action can have physical consequences.

    Sources

  • Verkada Adds Fleet Cameras, Cloud Audio and Read-Only AI Connections to Command

    Verkada Adds Fleet Cameras, Cloud Audio and Read-Only AI Connections to Command

    Verkada has expanded its Command platform with products for fleet video, cloud-managed audio and connections to external artificial-intelligence services. The additions were announced at the company’s VerkadaOne conference in Miami.

    Verkada Transportation brings vehicle camera footage and selected diagnostic data into Command through three ruggedized camera models and a gateway supporting 5G and Wi-Fi. The audio offering adds centrally managed speakers and paging functions for facilities. Catalyst uses Model Context Protocol to connect Command with approved services including Claude, ChatGPT and Gemini.

    The company says the external AI connection will initially operate in read-only mode and support natural-language creation of reports and workflows. Read-only access limits direct control risk, but organizations still need to assess what data is exposed to connected services, how prompts and outputs are logged, and whether sensitive video or identity information can leave an approved boundary.

    Why it matters

    Unified platforms are extending beyond fixed cameras and doors into vehicles, audio and AI-assisted operations. The operational benefit is a shared view, while the governance challenge is maintaining clear trust boundaries across every connected service and preserving the evidentiary controls described in video evidence chain of custody.

    Sources

  • UK’s Quantum Motion Extends Series C Funding Round to Scale Fault-Tolerant Silicon Quantum Chips

    UK’s Quantum Motion Extends Series C Funding Round to Scale Fault-Tolerant Silicon Quantum Chips

    UK-based Quantum Motion said on September 14, 2026 that it has finalized a second close of its Series C funding round, adding new investors to accelerate the industrial scale-up of its fault-tolerant silicon quantum processors.

    The Round

    The extension tranche was co-led by existing investors DCVC and Kembara, and brought in new and returning strategic and financial backers including imec.ventures, Lansdowne Partners, Sony Innovation Fund, S3 Ventures and Inkef. The additional funding builds on Quantum Motion’s original $160 million Series C round, positioning the company as one of the best-funded quantum computing firms in the UK.

    Silicon-Spin Approach

    Quantum Motion’s approach is built around silicon-spin qubits manufactured using standard 300mm CMOS semiconductor processes, rather than the superconducting or trapped-ion approaches used by many competitors. The company says this allows it to lean on existing commercial chip supply chains — including manufacturing partners such as imec and GlobalFoundries — rather than building entirely bespoke fabrication capability. The new capital will support continued custom silicon co-development, an expanded US research lab in Maryland, and participation in stage B of DARPA’s Quantum Benchmarking Initiative (QBI).

    Why It Matters

    Quantum computing developers face a persistent trade-off between qubit approaches that are easier to control today and approaches believed to scale more efficiently toward the large, fault-tolerant qubit counts needed for practical applications. By tying its architecture to existing semiconductor foundry processes, Quantum Motion is betting that manufacturing scale — not exotic materials or novel fabrication lines — will be the deciding factor in which qubit technology reaches commercially useful scale first. Continued institutional and strategic investment in silicon-based approaches also signals growing investor confidence that a CMOS-compatible path to quantum advantage is commercially viable alongside more established superconducting efforts from larger competitors.