Tag: industrial security

  • CISA Details High-Risk Flaws in Malcolm Network Analysis Platform

    CISA Details High-Risk Flaws in Malcolm Network Analysis Platform

    CISA has published advisory ICSA-26-254-01 covering multiple vulnerabilities in Malcolm network analysis platform releases earlier than v26.06.0. The advisory, dated October 1, assigns a maximum CVSS v3 base score of 8.8 and recommends moving to an appropriate September 2026 or later release.

    Broad weakness classes increase review scope

    The reported issues span cross-site scripting and open redirect, command injection, path traversal, server-side request forgery, authentication and authorization flaws, default credentials, improper certificate validation, a vulnerable dependency, and weak password hashing. This breadth means remediation planning should account for more than a single defect or attack path.

    CISA identifies Energy, Information Technology, and Water and Wastewater Systems as affected sectors and describes deployment as worldwide. Because Malcolm supports network analysis, weaknesses in the platform can be relevant to teams overseeing monitoring infrastructure and the larger cyber-physical security domain. The advisory facts do not establish exploitation, and organizations should avoid treating severity alone as evidence of compromise.

    Upgrade and exposure-reduction priorities

    CISA recommends updating to the latest September 2026 or later release. It also advises normal safeguards around network exposure, segmentation, access control, and monitoring. Operators should first identify deployed Malcolm versions and confirm the correct upgrade path for their environment, then review exposure and privileged access while the update is planned. Monitoring before and after remediation can help teams detect anomalous activity and verify that defensive controls continue to operate as intended.

    Sources and further reading

  • Johnson Controls Fixes Two EasyIO Neo Controller Security Flaws

    Johnson Controls Fixes Two EasyIO Neo Controller Security Flaws

    Johnson Controls has released updates for EasyIO Neo controllers after two security issues were documented in separate coordinated advisories. The vulnerabilities concern exposure of sensitive information and transmission of credentials or session information without adequate encryption.

    What the two advisories cover

    CVE-2026-64892 involves information that can be obtained through physical debugging interfaces. CISA gives it a maximum CVSS v3 base score of 3.5. CVE-2026-64893 addresses cleartext transmission of credentials and session data and carries a maximum CVSS v3 base score of 5.4.

    The affected devices are used in building-control environments, where controller credentials can provide a path into operational functions. CISA says it is not aware of public exploitation targeting either issue. Johnson Controls lists the related product advisories JCI-PSA-2026-20 and JCI-PSA-2026-30 on its security-advisory portal.

    Updates and compensating controls

    The vendor identifies EC version 3.3b64 and CW version 3.3b26 as fixed releases. For the network issue, operators should use HTTPS and disable HTTP where their deployment allows it. Physical access to debugging interfaces should also be restricted, with controller locations monitored as part of the site’s security plan.

    Before updating controllers, building operators should document current logic and configuration, confirm a rollback path and schedule functional testing. Network teams should check that management traffic stays on trusted segments. SectechMedia’s industrial safety and monitoring coverage includes further guidance for operational technology estates.

    Sources

  • ABB PCM600 Flaws Could Enable Privilege Escalation and File Overwrite

    ABB PCM600 Flaws Could Enable Privilege Escalation and File Overwrite

    ABB has addressed two vulnerabilities in PCM600, its protection and control engineering tool. CISA says the flaws could let a local attacker elevate privileges or cause project-archive files to be written outside the intended extraction directory.

    Two different local attack paths

    CVE-2026-15952 concerns permissions around a scheduler component running as LocalSystem. Under the conditions described by the advisory, a local user could exploit that arrangement to gain higher privileges. CVE-2026-15953 is a path-traversal issue in project archive handling that could place files beyond the selected extraction folder.

    CISA lists PCM600 versions through 2.14 as affected and gives the vulnerabilities a maximum CVSS v3 base score of 6.4. The agency says it is not aware of public exploitation. ABB has published product security advisories and provides workaround guidance for affected deployments.

    Why engineering workstations need special care

    PCM600 is used in energy-sector protection and control engineering. An engineering workstation can therefore hold trusted project files and privileged access to operational assets even when it is not directly exposed to the internet. Organizations should apply ABB’s guidance, limit local administrator rights and treat imported project archives as untrusted until validated.

    Before remediation, teams should back up projects and confirm recovery procedures. Afterward, review scheduled tasks, extraction directories and endpoint telemetry for unexpected files or privilege changes. SectechMedia’s energy-security coverage examines the wider operational context for protecting utility and industrial environments.

    Sources

  • Tethered Drones for Industrial Site Monitoring

    Tethered Drones for Industrial Site Monitoring

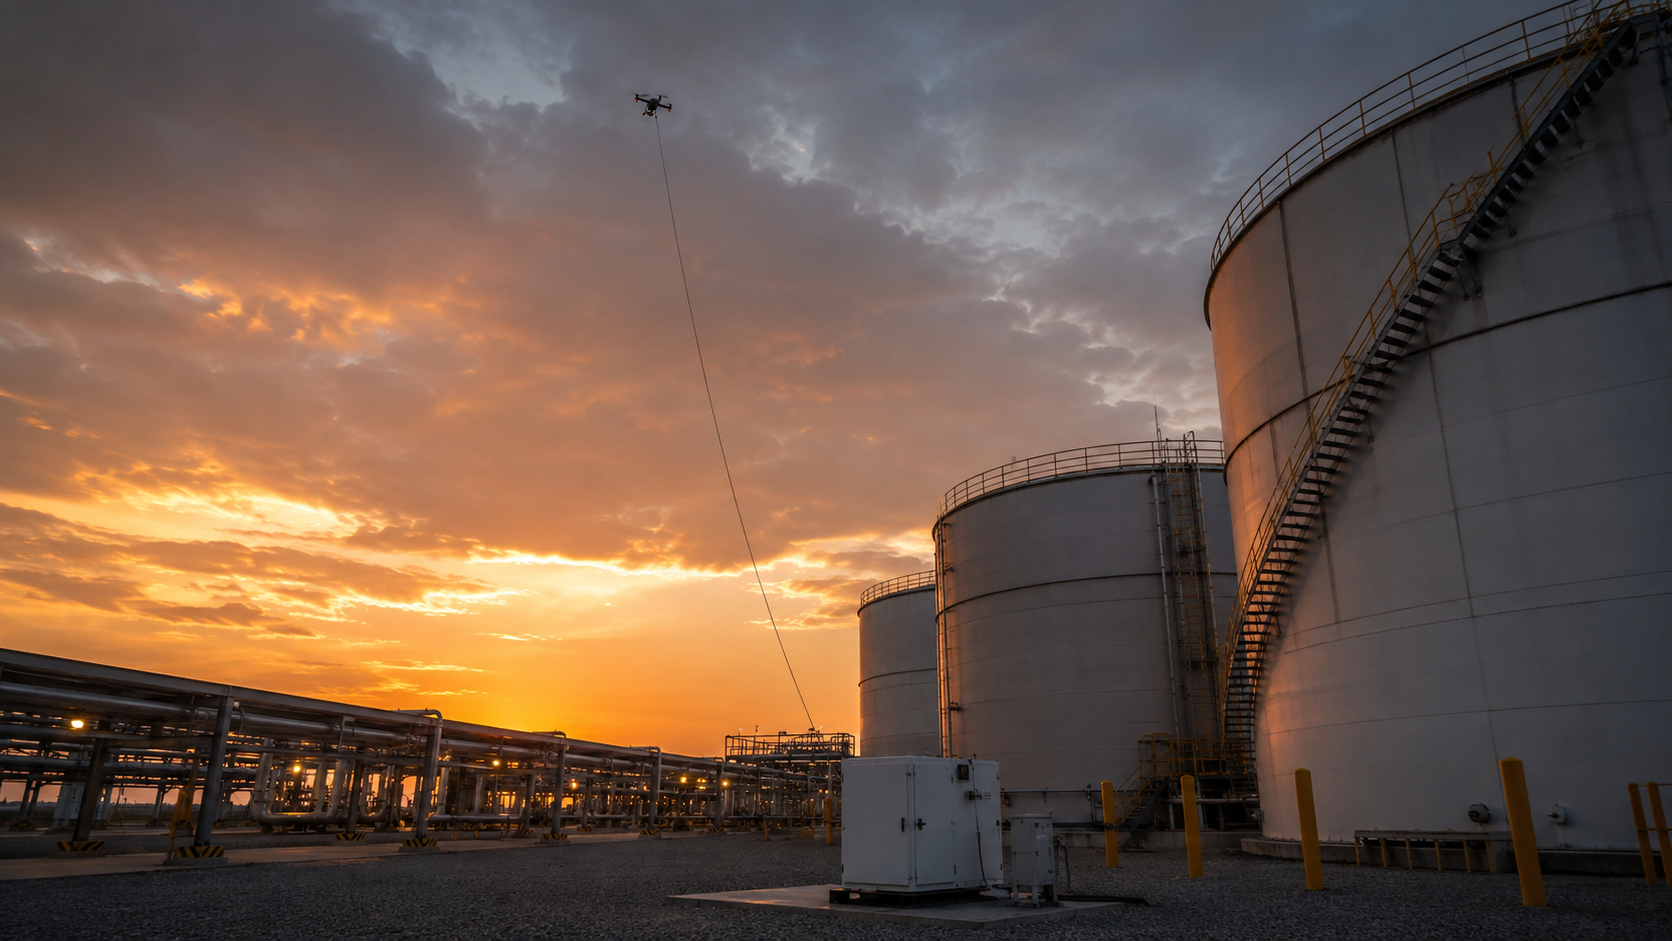
    Tethered drones occupy an unusual position between fixed surveillance towers and free-flying unmanned aircraft. Connected to the ground by a cable that can provide power and communications, a tethered drone can remain airborne for extended periods while carrying cameras, thermal sensors, communications equipment or other payloads.

    For industrial security, the main advantage is persistent elevated observation. A drone positioned tens of meters above a refinery, port, mine, pipeline construction zone or temporary event can see over fences, buildings and terrain that would block ground cameras. Because power is supplied from the ground, endurance can be measured in hours or days rather than the battery life of a conventional drone.

    The tether can also provide a secure high-bandwidth data path, reducing dependence on wireless links. This is useful where video quality, cyber security or RF congestion is a concern.

    Tethered systems still have operational limits. Wind, lightning, aviation restrictions, tether management and safe operating areas must be considered. They are not suitable everywhere, and the aircraft remains a visible physical asset that requires maintenance and procedures.

    Their strongest use case is usually temporary or semi-permanent overwatch: construction projects, incident response, large industrial shutdowns, border posts, temporary perimeter expansion or remote facilities where installing a tower would take longer.

    Tethered drones should be integrated with the wider security system rather than treated as standalone cameras in the sky. Video can feed the VMS, analytics can monitor defined zones and command-center operators can correlate aerial views with ground sensors.

    As industrial sites seek flexible surveillance coverage, tethered drones provide a middle ground between permanent infrastructure and mobile airborne patrol.