Author: Osiris

  • Anti-Tailgating and Mantrap Systems: Stopping Piggybacking at Secure Entrances

    Anti-Tailgating and Mantrap Systems: Stopping Piggybacking at Secure Entrances

    Tailgating, sometimes called piggybacking, happens when an unauthorized person follows an authorized person through a secured door before it closes and locks, quietly defeating an access control system without ever presenting a credential. It remains one of the most common real-world ways access control gets bypassed, largely because it exploits ordinary politeness rather than a technical flaw.

    Detection Versus Prevention

    Anti-tailgating technology falls into two broad categories: detection systems that sense a violation and alert security staff after the fact, and prevention systems that physically stop the second person from entering at all. Detection approaches include infrared or thermal sensors mounted above a doorway that count how many people pass through per credential swipe, and video analytics that visually track individuals entering a controlled space. These systems are lower cost and easier to retrofit into existing doorways, but they rely on a human response to an alarm rather than stopping the intrusion outright.

    How Mantraps Physically Prevent Piggybacking

    A mantrap, also called an interlocking vestibule, is a small enclosed space with two doors that are never both unlocked at the same time: a person must pass through the first door, have it lock behind them, and only then can the second door open, typically after a sensor confirms only one person is present in the vestibule. This makes it physically impossible for a second, uncredentialed person to slip through alongside an authorized individual, which is why mantraps are standard in the highest-security environments, including data centers, pharmaceutical facilities, and secure government spaces.

    Sensor Technology Inside the Vestibule

    Modern mantraps typically use overhead infrared beams, weight-sensing floor plates, or 3D depth sensors to verify occupancy before releasing the second door, since simple beam sensors alone can sometimes be fooled by unusual body positions or objects carried through the space. Some higher-security installations also require a second credential check or biometric verification at the interior door, adding an additional layer beyond simple occupancy counting.

    FAQ

    What is the difference between a mantrap and an airlock-style vestibule? The terms are often used interchangeably in security contexts; both describe a two-door interlocking space where only one door can be open or unlocked at a time.

    Can mantraps handle wheelchairs or large deliveries? Many facilities install a separate, staff-monitored accessible or delivery entrance alongside a mantrap, since the enclosed vestibule space can be too small for wheelchairs, carts or bulky equipment.

    Are camera-based tailgating detection systems as effective as mantraps? Detection-based systems are useful for lower-risk areas and can flag violations for review, but they do not physically prevent an intrusion the way a mantrap does, which is why the highest-security spaces typically use mantraps rather than detection alone.

  • Turnstiles and Pedestrian Access Barriers: Types and How to Choose

    Turnstiles and Pedestrian Access Barriers: Types and How to Choose

    Turnstiles are one of the oldest access control technologies still in widespread use, and for good reason: paired with a card reader or biometric scanner, a turnstile physically enforces that only one person passes per valid credential, something a door alone cannot guarantee. Choosing the right type is a balance between throughput, security level and how a site wants to present itself to visitors.

    Waist-Height Turnstiles for High Throughput

    Waist-height turnstiles, the tripod or drop-arm style common in stadiums, transit stations and office lobbies, prioritize speed, letting large numbers of people pass quickly while still enforcing single-person entry per credential. Their tradeoff is security level: a determined person can climb or vault over a waist-height barrier, which is why they are typically paired with a security guard or camera coverage rather than deployed as a standalone security measure in high-risk environments.

    Full-Height Turnstiles for Higher Security

    Full-height turnstiles, which resemble a rotating cage extending from floor to ceiling, physically prevent climbing over or crawling under, making them the standard choice for unstaffed perimeter entrances at data centers, utilities and other facilities where an unauthorized entry cannot rely on a guard noticing in time. The tradeoff is throughput and cost: full-height units process people more slowly and take up significantly more space and budget than waist-height alternatives.

    Optical and Sensor-Based Lanes

    A newer category, optical turnstiles or speed lanes, uses infrared sensors rather than physical arms to detect unauthorized passage, sounding an alarm or triggering a barrier only when someone attempts to pass without a valid credential or follows too closely behind an authorized person. These systems offer a more open, modern appearance favored in corporate lobbies, but they generally rely on integration with video analytics or a staffed reception desk to respond to detected violations rather than physically stopping them outright.

    Matching the Barrier to the Risk

    Security consultants typically select turnstile type based on the consequence of an unauthorized entry, the expected volume of legitimate traffic, and whether the location has staff present to respond to an alarm. A single site often uses different turnstile types at different entrances, for example optical lanes at a staffed main lobby and full-height turnstiles at an unstaffed rear or loading-area entrance.

    FAQ

    Can turnstiles alone stop tailgating? Waist-height and optical turnstiles reduce tailgating but do not fully prevent a determined person from following closely behind an authorized individual; full-height turnstiles and mantrap-style systems provide stronger physical prevention.

    Are full-height turnstiles required for data centers? Not universally required by code, but they are a common industry best practice for unstaffed high-security entrances where climbing over a barrier must be physically prevented rather than just detected.

    Do optical turnstiles work with mobile credentials? Yes, most modern optical turnstile systems integrate with the same card, mobile or biometric credential readers used elsewhere in a facility’s access control system.

  • Lawsuit Tests Whether AI Gun-Detection Vendors Can Be Held Liable When Systems Miss a Threat

    Lawsuit Tests Whether AI Gun-Detection Vendors Can Be Held Liable When Systems Miss a Threat

    A legal analysis published by SecurityInfoWatch examines a lawsuit, filed May 1, 2026, by a survivor of the January 2025 shooting at Antioch High School in Nashville against AI weapons-detection vendor Omnilert and installer System Integrations. The suit alleges the AI gun-detection system deployed at the school failed to flag the shooter’s weapon.

    The SIW analysis frames the case as an early test of whether weapons-detection vendors can be held legally liable when a system’s marketed detection capabilities do not perform as claimed in a real-world incident — a question the physical security industry has largely not had to confront in court until now.

    Why it matters: As AI-based weapons detection is adopted more widely in schools and other public facilities, this case and others like it will likely shape how vendors market detection-accuracy claims, how procurement contracts allocate liability, and how buyers evaluate performance guarantees — regardless of the case’s eventual outcome.

    Source: SecurityInfoWatch.com, September 10, 2026.

  • CISA Updates Advisory on Critical Flaws in ST Engineering iDirect Satellite Terminals

    CISA Updates Advisory on Critical Flaws in ST Engineering iDirect Satellite Terminals

    CISA issued Update A to advisory ICSA-26-183-01, covering four vulnerabilities in ST Engineering iDirect iQ-series satellite (VSAT) terminals, with CVSS scores up to 8.8 and one flaw rated 9.4 on the CVSS 4.0 scale. The advisory was originally released July 2, 2026.

    The flaws include missing authentication on REST API endpoints that expose device identity and cryptographic material, a cross-site request forgery vulnerability that can trigger a remote reboot or denial of service, a local privilege-escalation path via a factory-default low-privilege account, and exposure of password hashes. CISA lists Communications, Defense Industrial Base, Energy, Government and Transportation as affected sectors.

    Why it matters: VSAT terminals from vendors like ST Engineering iDirect provide connectivity for maritime vessels, remote energy sites, and defense operations where terrestrial networks are unavailable. Authentication bypasses on internet-facing satellite terminal management interfaces are a persistent, underappreciated risk category for organizations with remote or offshore infrastructure.

    Source: CISA ICS Advisory ICSA-26-183-01 (Update A), September 10, 2026.

  • Fresh Drone Alert Issued Around Amritsar International Airport Days After Flight Diversions

    Fresh Drone Alert Issued Around Amritsar International Airport Days After Flight Diversions

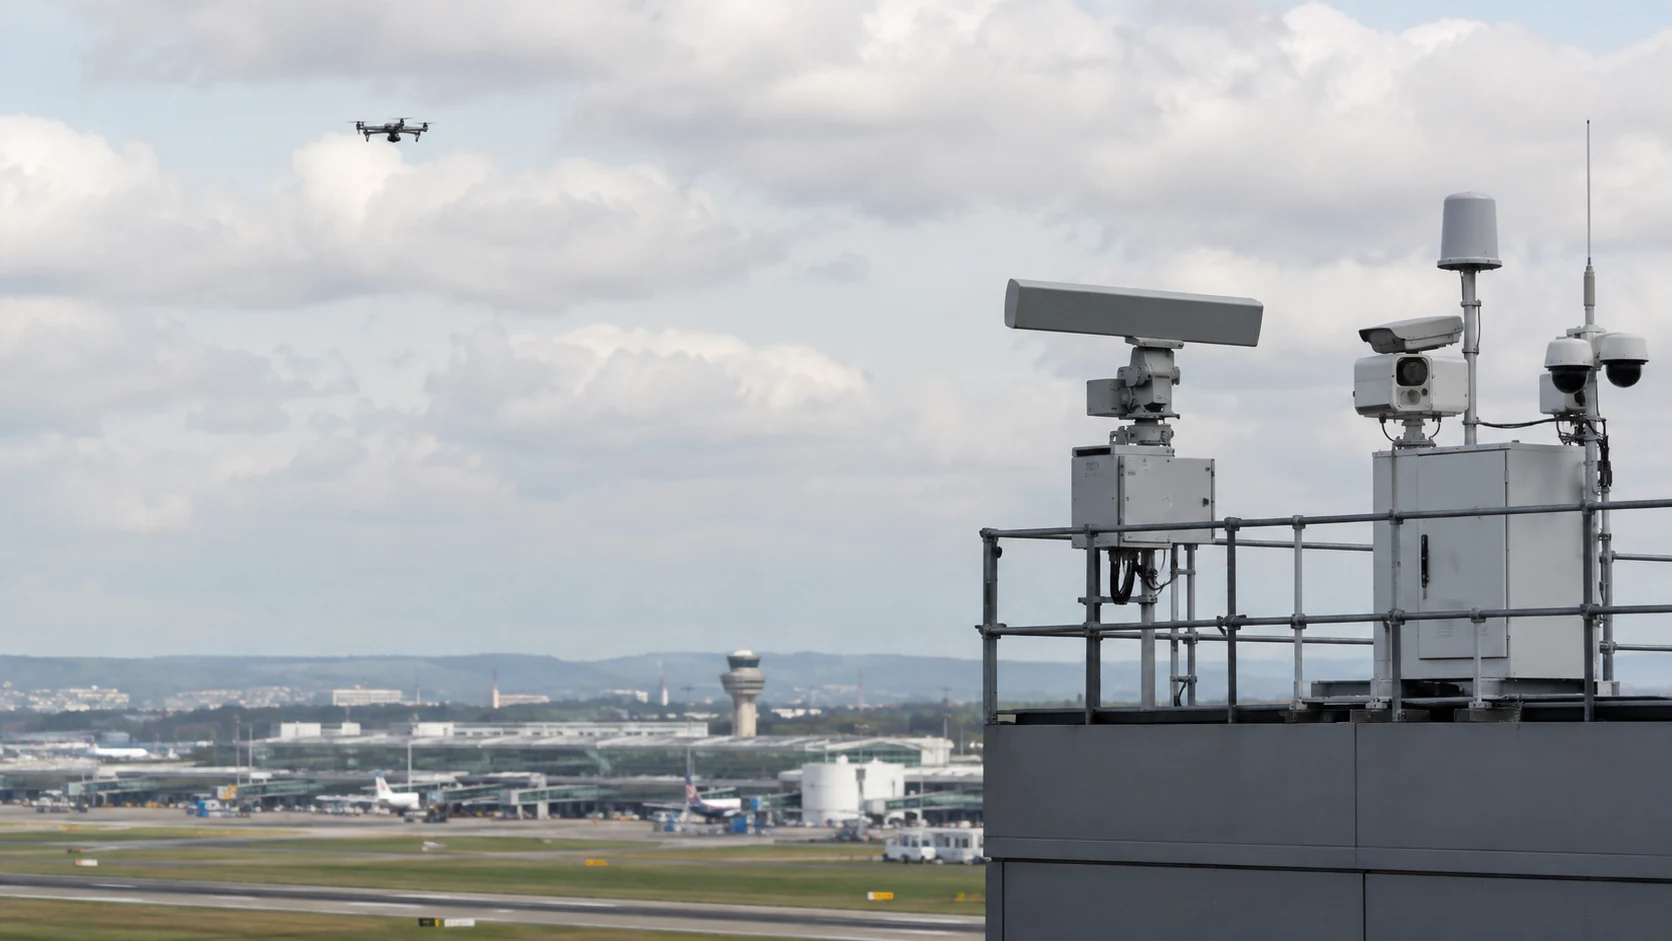
    Amritsar Police issued a fresh drone-activity alert covering a 3-kilometer “Red Zone” and 5-kilometer “Yellow Zone” around Sri Guru Ram Dass Jee International Airport, NDTV reported. The alert follows a September 7 incident in which suspected drone activity forced the diversion of seven flights, reported separately by Hindustan Times and Indian Express.

    Authorities are now requiring advance notice for any local drone operation near the airport as part of the response.

    Why it matters: The measures reflect a broader pattern of airports responding to unauthorized drone activity with administrative restricted-zone declarations ahead of, or alongside, physical counter-UAS detection investment — a lower-cost interim step that depends heavily on operator compliance and enforcement to be effective.

    Source: NDTV, September 10-11, 2026, corroborated by Hindustan Times and Indian Express on the underlying September 7 diversion event.

  • Oracle Reports Record Cloud Infrastructure Growth, Remaining Performance Obligations Hit $664 Billion

    Oracle Reports Record Cloud Infrastructure Growth, Remaining Performance Obligations Hit $664 Billion

    Oracle reported first-quarter fiscal 2027 total revenue of $19.3 billion, up 30% year-over-year, according to the company’s official earnings release. Cloud Infrastructure (IaaS) revenue rose 121% to $7.4 billion.

    The company said it delivered 850MW of additional data center capacity and more than 300,000 GPUs to AI cloud customers since the previous quarter, and booked over $30 billion in new AI cloud contracts, pushing Remaining Performance Obligations to $664 billion, up $209 billion year-over-year.

    Why it matters: The scale of Oracle’s new AI cloud contract bookings and physical data center capacity additions in a single quarter underscores how rapidly cloud infrastructure providers are scaling to meet AI compute demand — growth that directly drives the data center physical security, power and cooling buildout this publication tracks.

    Source: Oracle official earnings release, September 10, 2026.

  • TSMC Posts Record August Revenue, Up 53% Year-Over-Year on AI Chip Demand

    TSMC Posts Record August Revenue, Up 53% Year-Over-Year on AI Chip Demand

    TSMC reported August 2026 revenue of NT$514.8 billion ($16.35 billion), up 53.3% year-over-year and 10.1% month-over-month, according to the company’s investor relations release, corroborated by CNBC. It marked TSMC’s fourth consecutive month of revenue growth, driven by AI server chip demand.

    January-through-August 2026 revenue totaled NT$3.39 trillion, up 39.3% year-over-year.

    Why it matters: As the dominant manufacturer of advanced chips for AI accelerators, TSMC’s monthly revenue figures function as a leading indicator for the broader pace of AI infrastructure buildout — directly relevant to security and infrastructure planners tracking how fast data center and compute capacity is scaling globally.

    Source: TSMC investor relations release, corroborated by CNBC, September 10, 2026.

  • CISA Advisory: Hard-Coded Cryptographic Key Found in AVEVA Pipeline Integrity Monitor

    CISA Advisory: Hard-Coded Cryptographic Key Found in AVEVA Pipeline Integrity Monitor

    CISA published advisory ICSA-26-253-01 describing four vulnerabilities in AVEVA Pipeline Integrity Monitor, with CVSS scores up to 8.4 (CVE-2026-81821 through CVE-2026-81824). The flaws include a hard-coded cryptographic key, use of a broken or risky cryptographic algorithm, missing authorization checks, and a stored cross-site scripting vulnerability.

    According to CISA, successful exploitation could allow an attacker to disclose sensitive project data, brute-force password hashes, or execute arbitrary code in a victim’s browser session. The advisory identifies the Critical Manufacturing sector as affected. AVEVA has released a fix in the 2025 SP1 P2 release.

    Why it matters: Pipeline integrity monitoring software is used to track the structural and operational health of oil, gas and other pipeline infrastructure. Vulnerabilities that expose project data or credential material in this class of software are a direct concern for critical-infrastructure operators, even where exploitation requires network access rather than being remotely trivial.

    Source: CISA ICS Advisory ICSA-26-253-01, September 10, 2026.

  • Russian-Speaking Actor Used Hundreds of AI Agents to Exploit PaperCut in 395+ Organizations

    Russian-Speaking Actor Used Hundreds of AI Agents to Exploit PaperCut in 395+ Organizations

    Security research firm GreyNoise reported that a Russian-speaking threat actor used hundreds of AI agents, built on an AI coding harness paired with a large language model, to weaponize CVE-2026-81578 and CVE-2026-82078 in PaperCut NG/MF print-management software, BleepingComputer and SecurityWeek reported.

    The AI-orchestrated campaign compromised at least 395 organizations across 48 countries since August 31, 2026, with roughly half of victims in the education sector, according to GreyNoise’s research.

    Why it matters: The scale and speed of an AI-agent-orchestrated exploitation campaign against a known, patchable vulnerability illustrates how AI coding tools are lowering the operational cost of mass exploitation for attackers, independent of whether the underlying vulnerability itself is novel — a trend security teams increasingly need to plan around rather than treat as a future risk.

    Source: GreyNoise research, corroborated by BleepingComputer and SecurityWeek, September 10, 2026.

  • Vecna Robotics Raises $31 Million as FCC Foreign-Robot Restrictions Boost US-Built Warehouse Automation

    Vecna Robotics Raises $31 Million as FCC Foreign-Robot Restrictions Boost US-Built Warehouse Automation

    Waltham, Massachusetts-based Vecna Robotics raised $31 million led by Unless, DC Velocity reported, citing surging demand tied to a July 2026 Federal Communications Commission policy restricting purchases of certain foreign-made robots on cybersecurity grounds. The company builds case and pallet automation systems for warehouses.

    Vecna said the funding will be used to scale deployment teams and expand its automation capabilities as US-based logistics operators shift purchasing toward domestically built robotics platforms.

    Why it matters: The FCC’s restriction treats foreign-made warehouse and logistics robots as a potential cybersecurity and supply-chain risk category, similar to earlier restrictions on foreign-made telecom and video surveillance equipment — a signal that physical automation hardware is increasingly being evaluated through the same national-security lens as networking gear and cameras.

    Source: DC Velocity, September 10, 2026, corroborated by GlobeNewswire press release and Boston Business Journal.