Category: News

Current, event-driven reporting, announcements and industry developments.

  • Gyazo Breach Exposes 23.6 Million Users and 490 Million Metadata Records

    Gyazo Breach Exposes 23.6 Million Users and 490 Million Metadata Records

    Gyazo developer Helpfeel has disclosed a breach involving approximately 23.6 million user records and a much larger collection of image metadata. Infosecurity Magazine reported that attackers exploited a vulnerability in an upload server, while Helpfeel’s 16 September notice said the weakness had been remediated.

    Why metadata can be sensitive

    The affected metadata reportedly included image identifiers, source IP and URL information, user-agent data, OCR-extracted text and other fields connected with captures. Such records can be valuable even when they are not the original image. OCR text may contain terminal output, internal application details or credentials that happened to be visible in a screenshot.

    Helpfeel warned that some metadata could be used to construct image URLs and temporarily restricted access to affected images. The company urged users to change passwords, particularly where credentials were reused, and to watch for follow-on phishing. Some data related to older images, which may reduce but does not remove risk.

    Lessons for screenshot and collaboration tools

    Organizations should treat screenshot services as data processors within their security inventory. Retention, OCR, access control and deletion settings deserve review, and secrets visible on screen should be considered exposed if captured. The incident reinforces the need for incident response plans that examine metadata and derived data, not only primary files.
    Sources

  • Qtonic Launches QShield for Post-Quantum Network Encryption

    Qtonic Launches QShield for Post-Quantum Network Encryption

    Qtonic Quantum has launched QShield, a software product intended to protect network traffic between compatible Linux endpoints with post-quantum key establishment and authentication. Security Today reported that the product combines these mechanisms with conventional authenticated packet encryption.

    Migration at the connection layer

    The company says QShield uses standardized post-quantum algorithms for establishing keys and authenticating endpoints. A connection-layer approach can help organizations test migration without immediately replacing every application. It does not eliminate the need to inventory cryptography elsewhere, including certificates, stored data, firmware and third-party services.

    Qtonic also described a fail-closed design and published test materials from a multi-day run between cloud hosts. These are vendor-reported results, not an independent certification. Security Today explicitly noted that the company does not claim FIPS 140-3 validation or government authorization for the product.

    How buyers should evaluate the claim

    Organizations should verify algorithm implementation, key management, performance under failure and interoperability with operational tooling. A post-quantum label does not by itself establish secure deployment. QShield is another sign that cyber-physical security teams need a documented cryptographic inventory and a staged migration plan rather than a last-minute product replacement.

    Sources

  • Boston Dynamics Positions Mobile Robots for Enterprise Security

    Boston Dynamics Positions Mobile Robots for Enterprise Security

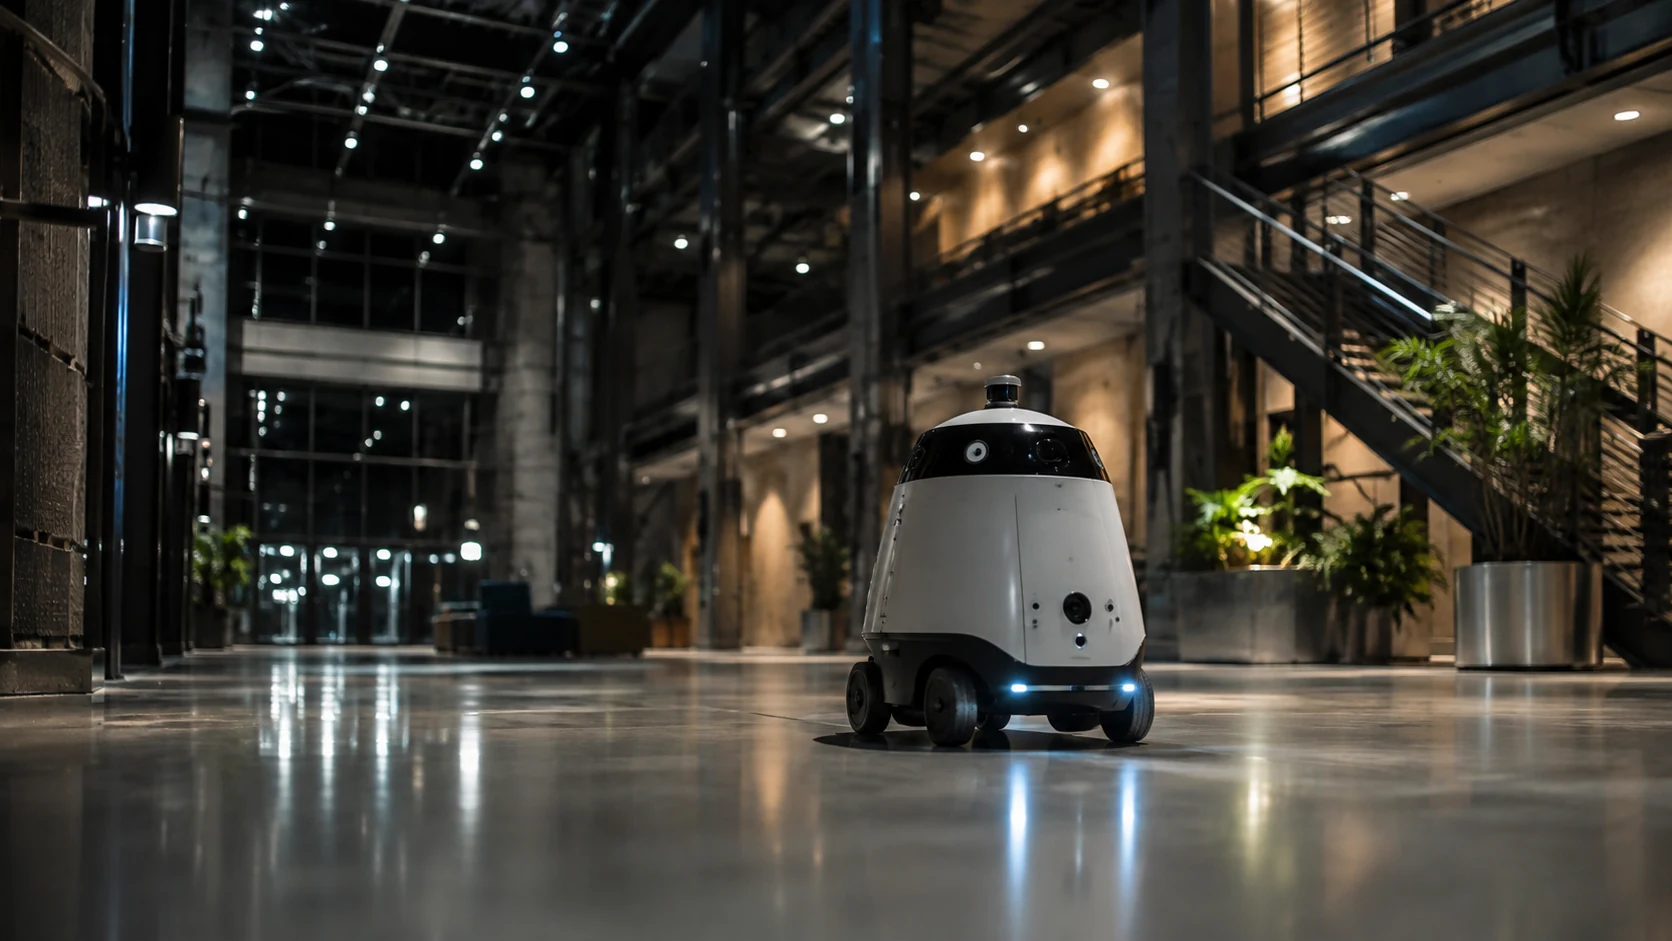
    Boston Dynamics is presenting mobile robots as tools for enterprise inspection and security operations, extending sensor coverage into locations that may be repetitive, remote or hazardous for personnel. International Security Journal examined the shift on 21 September.

    From patrol visibility to repeatable inspection

    A mobile robot can carry cameras, thermal sensors or environmental instruments along a defined route. The security value is not simply movement: the platform must collect consistent observations, transmit them reliably and flag deviations that a human operator can assess. Repeatable inspection can be useful around industrial assets, utility spaces and large campuses.

    Robots do not remove the need for a response team. Stairs, doors, crowds, weather and communications gaps can limit coverage, while an ambiguous alert still requires judgment. Operators also need rules for privacy, recording and interaction with employees or visitors.

    Integration and governance

    Before deployment, organizations should map safe routes, define no-go areas, test loss-of-communications behavior and secure the robot’s credentials. Video and telemetry should enter the existing command workflow rather than create a separate unmonitored console. Mobile robots can strengthen industrial safety and monitoring when their role, limitations and escalation process are explicit.

    Sources

  • Streamlight Launches Hazard-Rated Side-Mounted Firefighter Helmet Light

    Streamlight Launches Hazard-Rated Side-Mounted Firefighter Helmet Light

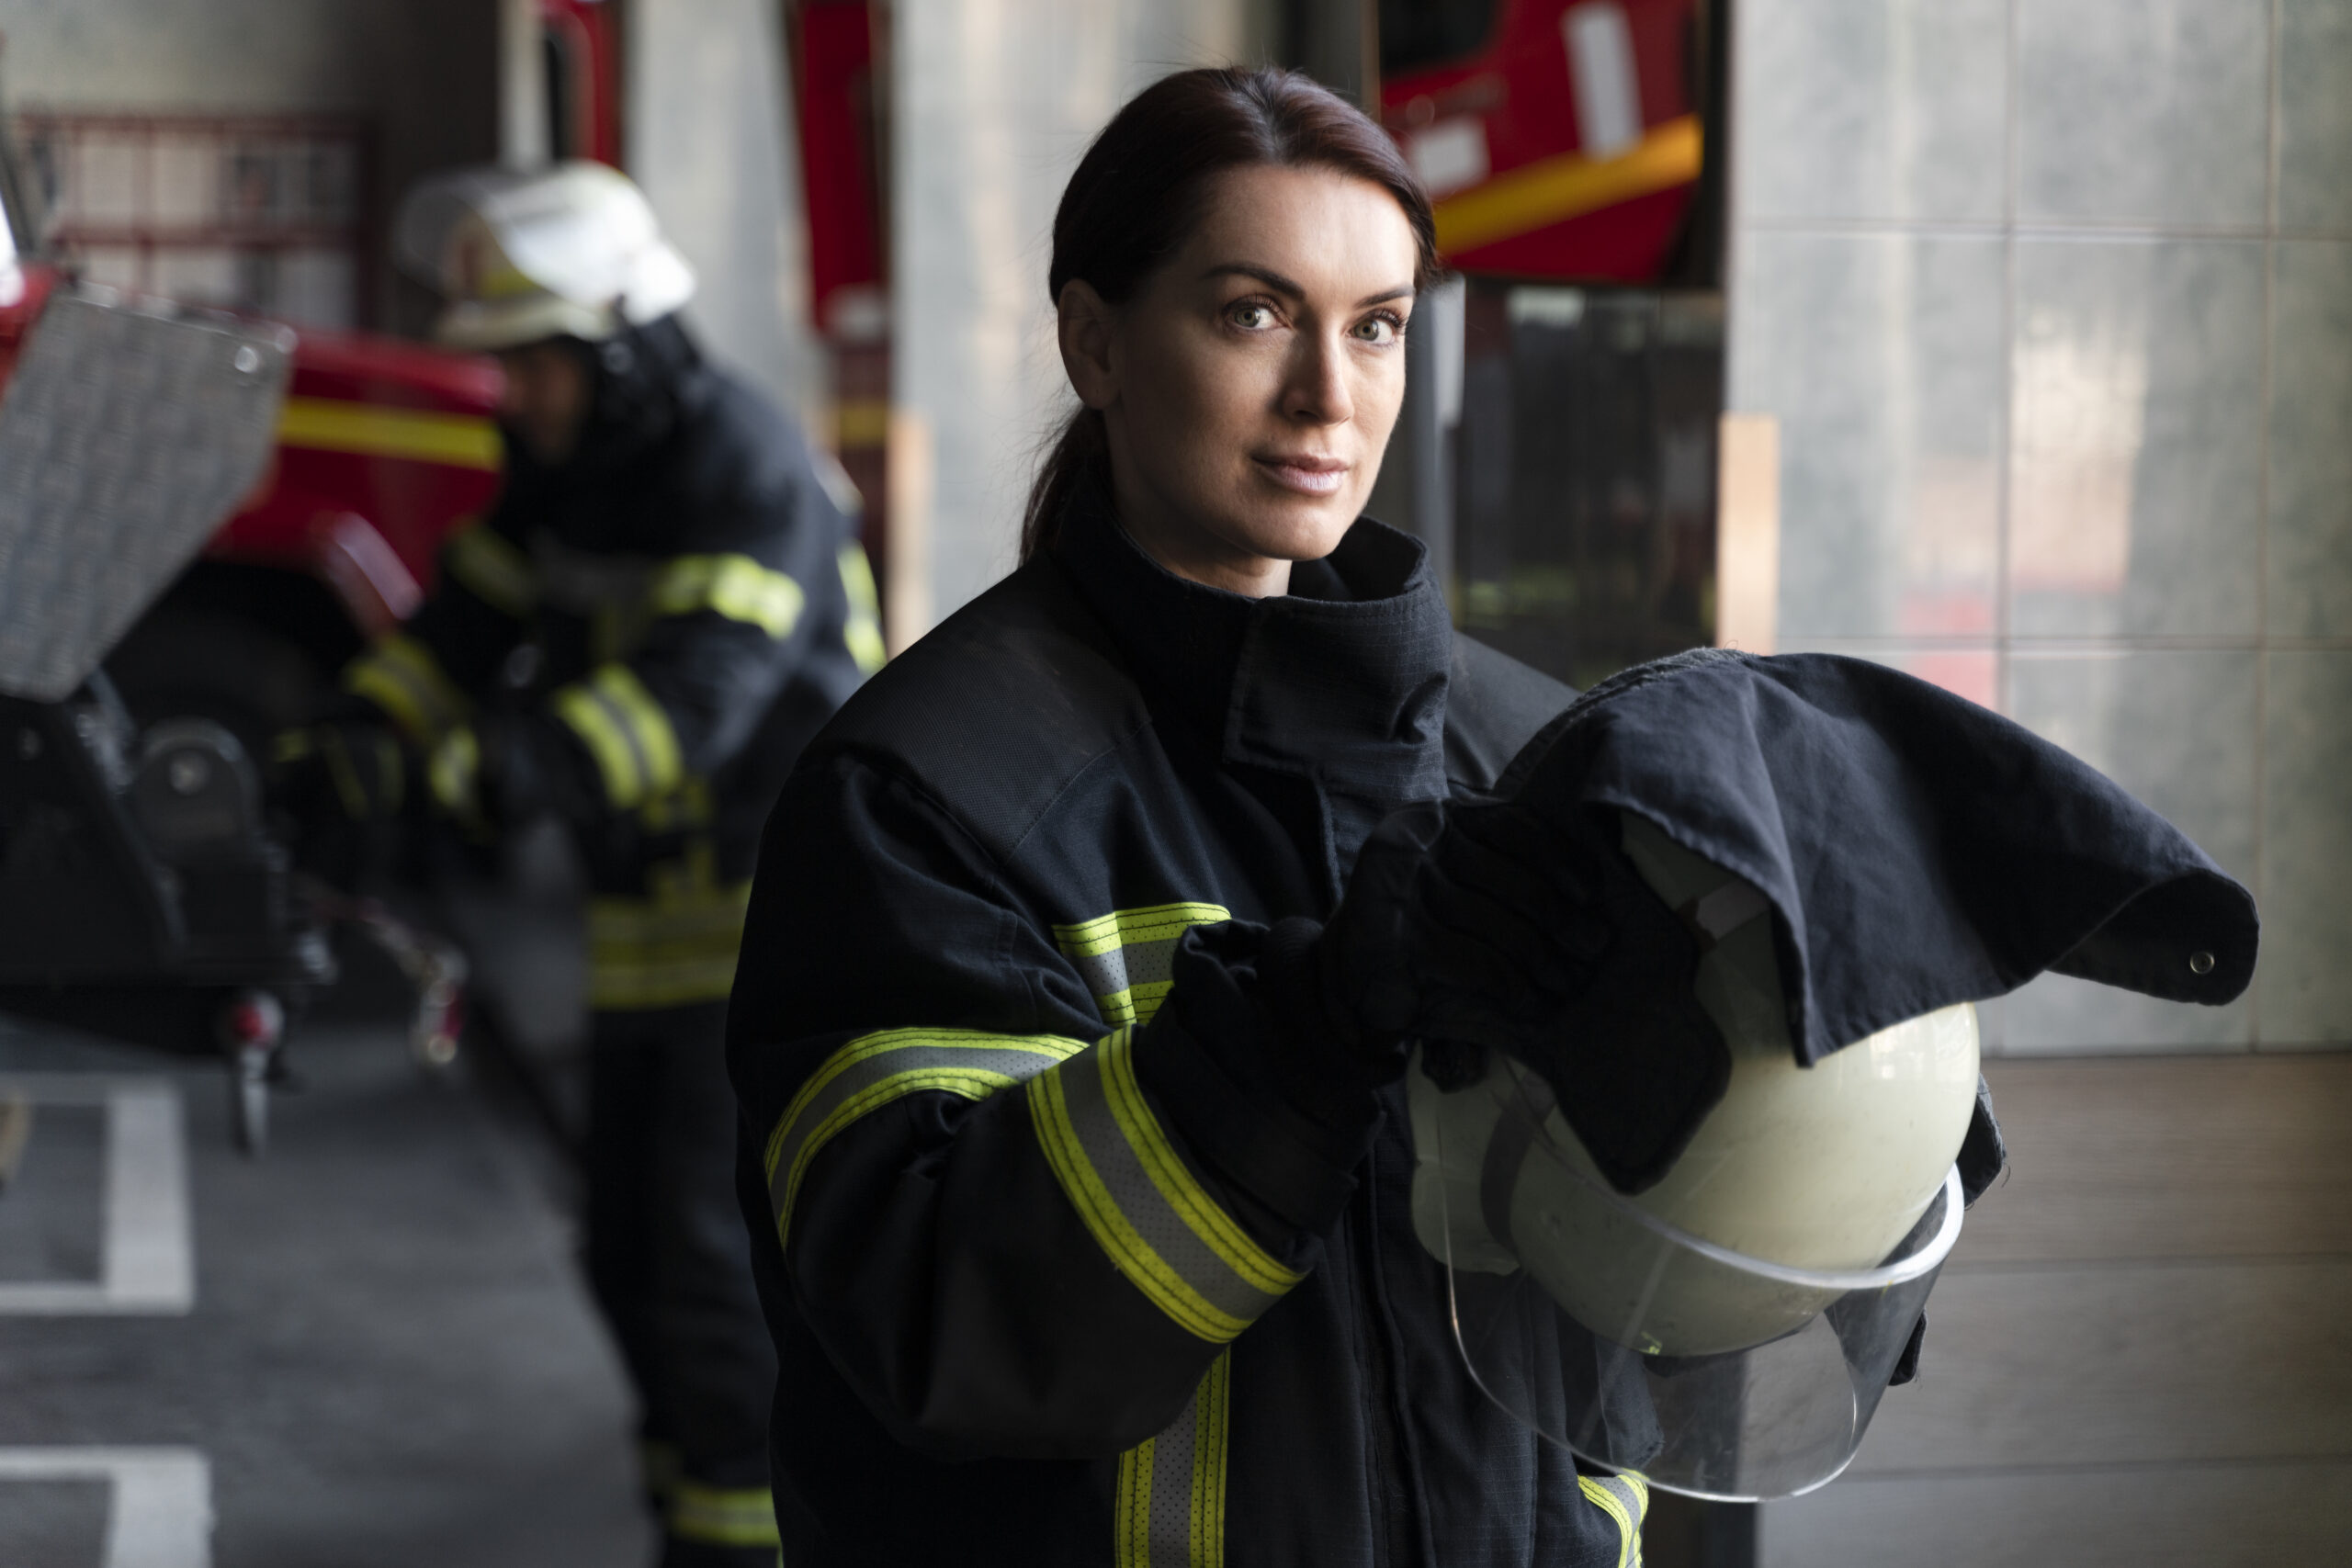
    Streamlight has introduced the SL-SideSaddle HAZ-LO, a side-mounted helmet light aimed at firefighting and rescue work in locations where equipment may need a hazardous-location rating. International Fire and Safety Journal reported the launch on 21 September.

    Helmet-mounted lighting as safety equipment

    A helmet light keeps both hands available and can illuminate the direction in which the wearer is looking. Side mounting is intended to reduce interference with other helmet components, but fit must be assessed with the complete ensemble, including face protection, communications equipment and breathing apparatus. A light that catches on equipment or changes helmet balance can create a new problem.

    Hazardous-location suitability should be confirmed against the exact certification and operating environment rather than inferred from the product name. Users also need to follow battery, charging and inspection instructions. Damage to seals or housings can invalidate assumptions made at procurement.

    Deployment considerations

    Fire services should test beam pattern, controls and glove usability under realistic visibility conditions. Equipment checks should be incorporated into routine readiness procedures, including battery state and secure attachment. The product sits within a broader emergency and life-safety system in which personal lighting supports, but does not replace, team communications and scene illumination.

    Sources

  • US Air Force Seeks Deployable Counter-UAS Package

    US Air Force Seeks Deployable Counter-UAS Package

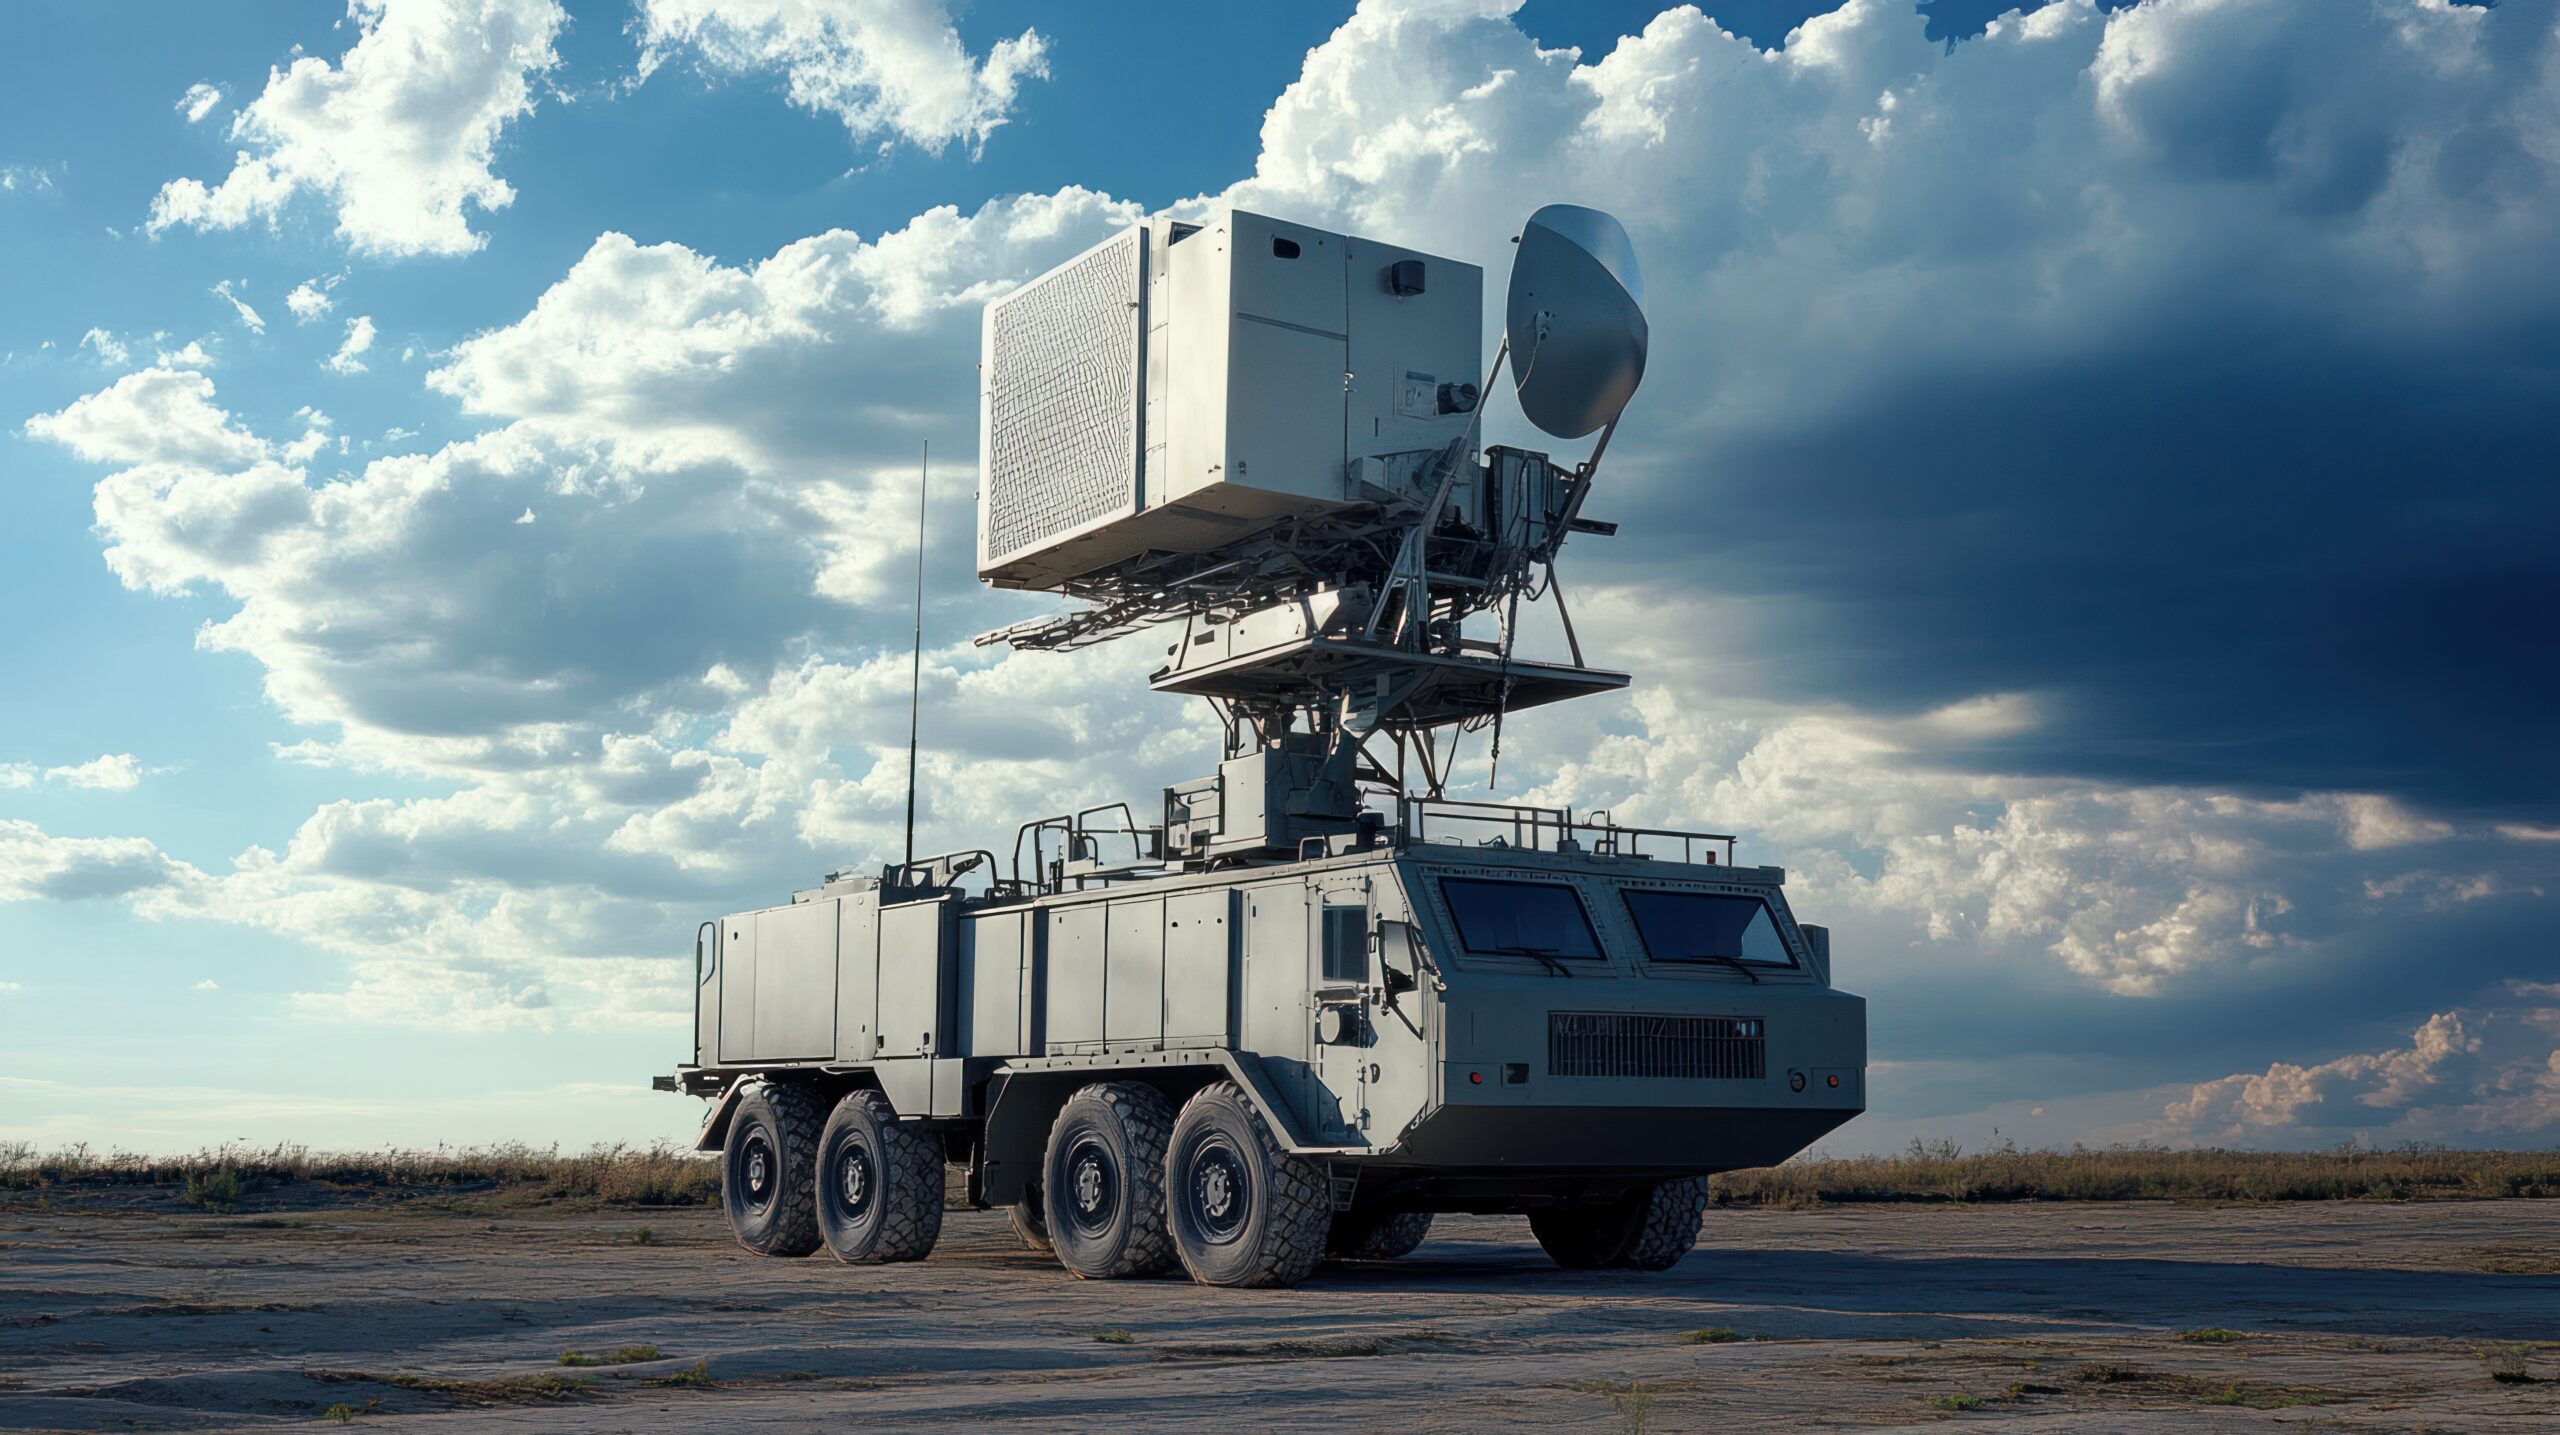
    The U.S. Air Force is seeking a deployable counter-UAS package intended to address gaps in the protection of operating locations. A federal opportunity notice identified by Unmanned Airspace points to demand for a capability that can be moved, established and integrated without relying on a permanent site architecture.

    What deployability changes

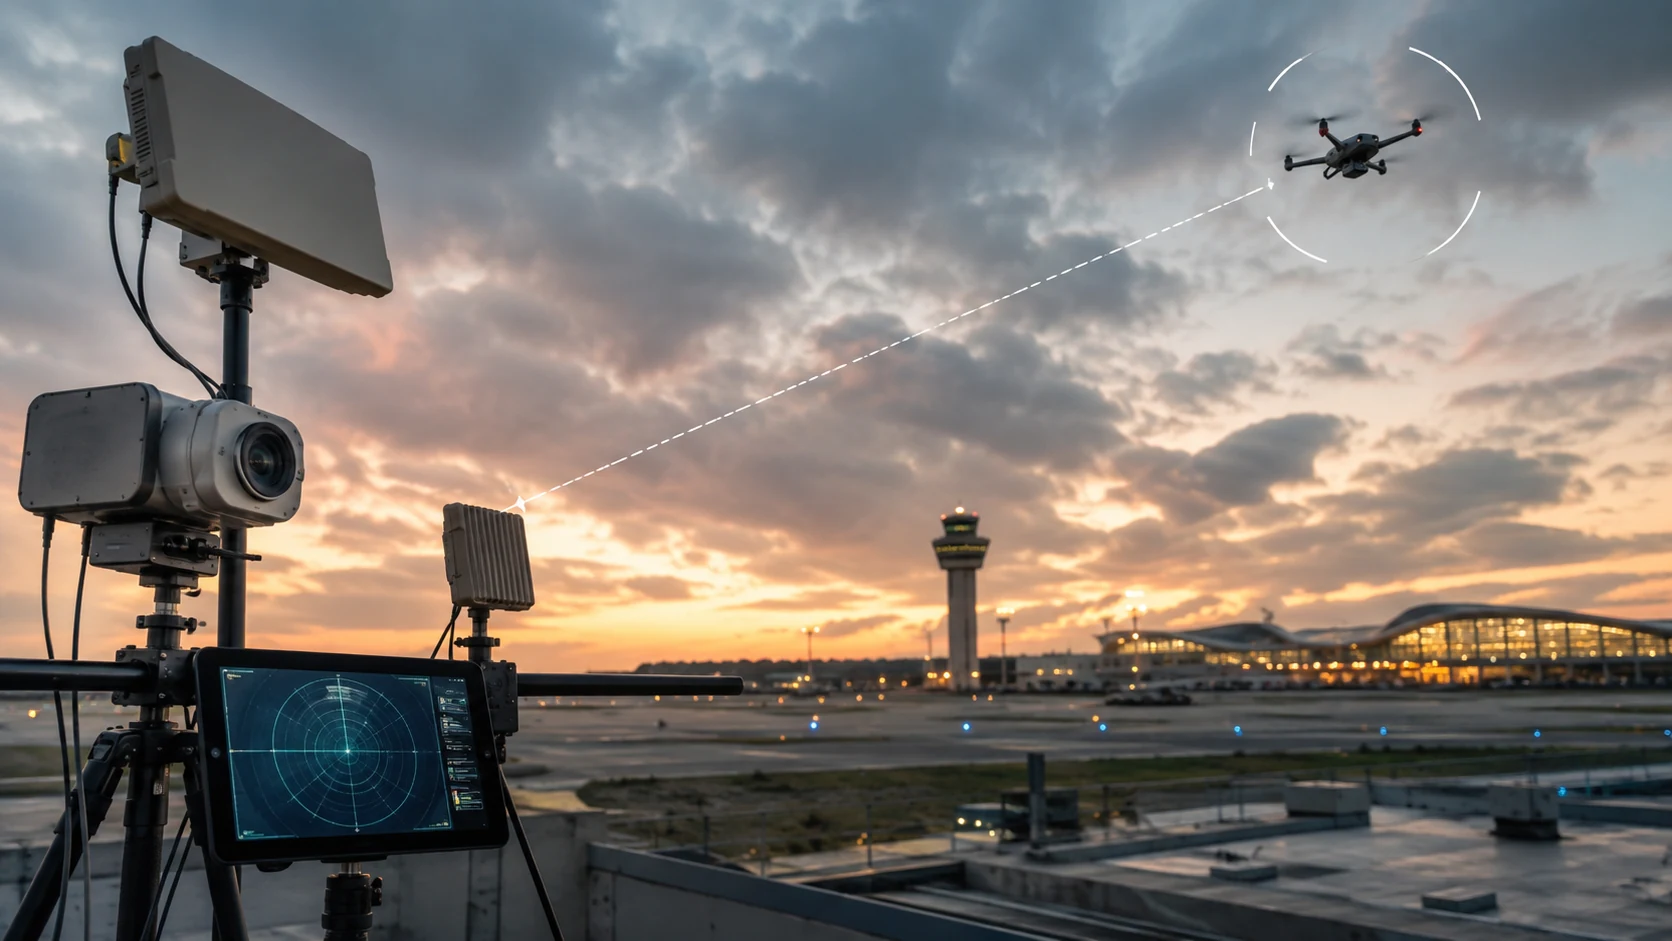
    A transportable system must balance coverage with logistics. Sensors, command equipment, power, communications and any authorized effectors have to fit the deployment concept and become operational within a useful period. Equipment that performs well at a fixed test range may behave differently when terrain, electromagnetic conditions and local air traffic are unfamiliar.

    The requirement also highlights the importance of interoperability. Counter-UAS packages need to exchange tracks and alerts with base-defense teams while preserving evidence for later review. Identification and escalation procedures must account for friendly drones, contractors and civilian activity near the protected area.

    Evaluation priorities

    Field testing should examine false alerts, setup repeatability, track continuity and operator workload, not merely maximum detection range. Sustainment, software updates and training can determine whether a deployable system remains useful after the initial exercise. The solicitation adds another procurement signal in the expanding counter-UAS market.

    Sources

  • EASA Proposes New Security Rules for Drone Operations

    EASA Proposes New Security Rules for Drone Operations

    The European Union Aviation Safety Agency has issued Opinion 06/2026 proposing amendments intended to tighten the security of drone operations across Europe. The package addresses the continued growth of unmanned aviation and the need to align operational authorization with security, identification and oversight.

    From aviation safety to security assurance

    Unmanned Airspace reports that the opinion covers a broad set of changes affecting operators and authorities. EASA opinions are proposals within the European rulemaking process, not the same as rules already in force. Operators should therefore distinguish the published proposal from the legal text that may eventually be adopted.

    Security controls for drone operations can include operator identity, remote identification, protected command links, incident reporting and restrictions around sensitive locations. The practical effect depends on aircraft category, operating environment and the final implementing rules. Authorities also need systems that can consume identification data without treating every unknown aircraft as hostile.

    Implications for airspace security

    Airports, critical infrastructure operators and counter-UAS teams should follow the rulemaking because regulatory identification and operational data can improve incident assessment. They do not replace independent detection or response authority. A balanced airspace-security program must combine legal process, reliable sensor evidence and proportionate intervention.

    Sources

  • Denmark Buys Weibel Radars for Military Counter-Drone Operations

    Denmark Buys Weibel Radars for Military Counter-Drone Operations

    Denmark’s defense acquisition organization is purchasing radars from Danish manufacturer Weibel Scientific for military counter-uncrewed-aircraft operations. The procurement reflects the growing emphasis on dedicated detection as armed forces respond to small and fast-moving aerial threats.

    Detection before engagement

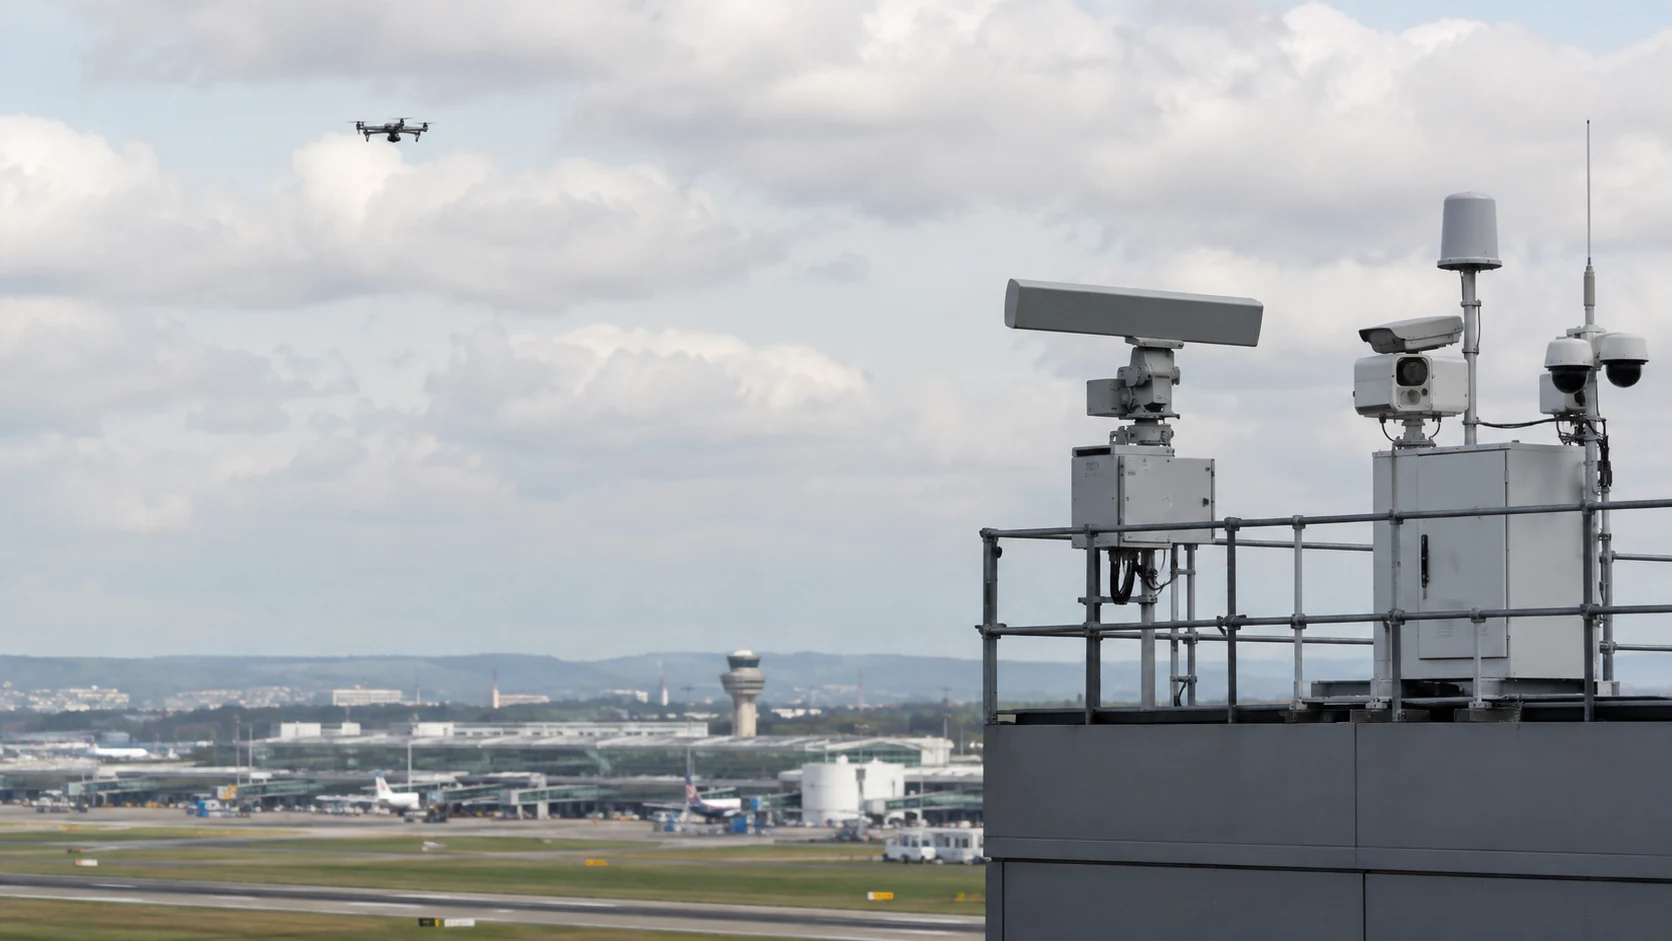
    Unmanned Airspace reported the purchase on 21 September, citing Denmark’s defense procurement authority. Radar is one part of a counter-UAS chain that may also include radio-frequency sensing, electro-optical confirmation, command-and-control software and an authorized mitigation method. The sensors must provide tracks that operators can classify and correlate before any response is selected.

    Small aircraft create difficult conditions because terrain, buildings, birds and legitimate aviation can generate clutter or competing tracks. Performance therefore depends on siting, calibration and integration as much as on the sensor specification. Military deployments also need clear procedures for transferring tracks among local units and wider air-defense networks.

    Integration is the central test

    The acquisition should be judged by field acceptance, data quality and operational fit rather than radar count alone. Track continuity, false-alert handling and identification workflows are particularly important near bases and civilian airspace. Denmark’s purchase adds to European investment in counter-UAS and airspace security amid concern about both hostile drones and ambiguous incursions.

    Sources

  • Idaho National Laboratory Introduces TOPGEAR for Cyber-Physical Influence Risk

    Idaho National Laboratory Introduces TOPGEAR for Cyber-Physical Influence Risk

    Idaho National Laboratory is developing TOPGEAR, a platform intended to show how corporate relationships and individual influence can create risk around critical infrastructure. The name stands for Technology, Organization and Person of Interest Graph Extraction, Analysis and Reporting.

    Looking beyond a conventional cyberattack

    Traditional assessments often concentrate on software vulnerabilities, network boundaries and physical hazards. TOPGEAR instead connects information about organizations, people and infrastructure assets. The objective is to reveal how investments, acquisitions, board positions or supplier relationships could create influence over facilities such as substations and data centers without a malware incident.

    Industrial Cyber reports that the platform draws on public sources including regulatory filings and energy data, then represents the information across social, infrastructure and cross-layer networks. Analysts can examine how an entity is connected to an asset and identify concentrations that may deserve additional review. The output is an aid to analysis, not proof that a relationship is malicious.

    A broader resilience model

    The project illustrates why critical-infrastructure protection requires ownership, supplier and governance data as well as technical telemetry. Organizations adopting similar methods should record source provenance, confidence and update dates so that old or ambiguous relationships do not become false accusations. TOPGEAR adds another perspective to security intelligence by treating organizational influence as a cyber-physical dependency.

    Sources

  • US Coast Guard Opens AI and Machine Learning Center

    US Coast Guard Opens AI and Machine Learning Center

    The U.S. Coast Guard is establishing a Center for Artificial Intelligence and Machine Learning at the Coast Guard Academy in New London, Connecticut. The center is intended to combine operational needs, academic research and workforce development rather than treating AI as a standalone software procurement.

    Mission-focused prototypes

    Industrial Cyber reports that the center will work with the Technology Readiness Directorate and the Office of Data and AI. Early work includes buoy-positioning analysis, cutter patrol scheduling and maritime border-security applications. The stated goal is to develop practical prototypes on shorter cycles while teaching military and civilian personnel to use approved tools responsibly.

    Partnerships with research institutions are expected to support testing and technical review. For a maritime service, however, deployment conditions can be more demanding than a laboratory benchmark. Systems may face intermittent communications, limited computing resources, sensitive operational data and the need for accountable human decisions.

    Security considerations

    Useful governance should define which data an AI system can access, what recommendations it may make and which actions always require an authorized operator. Models also need monitoring for drift and failure under unusual conditions. The center’s value will depend on whether prototypes can be integrated with existing port and maritime security workflows without weakening command responsibility.

    Sources

  • Google Cloud Publishes Secure Agentic AI Blueprint for Manufacturing

    Google Cloud Publishes Secure Agentic AI Blueprint for Manufacturing

    Google Cloud has published a blueprint for deploying agentic artificial intelligence in manufacturing while preserving physical safety, operational resilience and human authority. The framework addresses agents that can move beyond analysis to plan tasks or propose actions across enterprise, engineering and plant-floor workflows.

    Three connected operating domains

    The blueprint groups opportunities into business operations, engineering and industrial operations, and unified cybersecurity and resilience. Examples include procurement checks, predictive-maintenance analysis and the triage of security telemetry across IT and operational technology. Google emphasizes targeted pilots, data readiness, governance and access controls rather than unrestricted deployment.

    That distinction matters because an error in a factory can have physical consequences. An agent that summarizes maintenance records presents a different risk from one that can change a production schedule or interact with control infrastructure. The latter requires constrained permissions, tested rollback paths and a human decision point for consequential actions.

    Security architecture before scale

    Manufacturers should separate deterministic control from experimental AI services, validate data flows and monitor agent activity as a privileged workload. Digital twins and isolated environments can support testing without exposing production equipment. The blueprint reinforces a wider industrial monitoring principle: faster automation is valuable only when teams can explain, authorize and reverse its actions.

    Sources