Category: Industrial Safety & Monitoring

  • CISA Details Credential Exposure Flaw in Johnson Controls Simplex Incident Manager

    CISA Details Credential Exposure Flaw in Johnson Controls Simplex Incident Manager

    Cleartext Credentials Found in Memory

    The Cybersecurity and Infrastructure Security Agency published ICS advisory ICSA-26-232-01 on August 20, 2026, disclosing a vulnerability in Johnson Controls Simplex Incident Manager, a fire and life-safety incident-management application used across critical manufacturing, commercial facilities, government facilities, transportation systems and energy sites worldwide. Tracked as CVE-2026-27875, the flaw stores user credentials, including passwords and authentication tokens, in an unencrypted form in system memory while the application is running.

    CISA assigned the vulnerability a CVSS v3.1 base score of 5.8 (medium), rating it CWE-316, Cleartext Storage of Sensitive Information in Memory. A local attacker with low privileges, or an insider with memory-dumping tools, could extract the exposed credentials and use them for unauthorized access to the application and connected systems. Exploitation requires local access to the host, and CISA rates the attack complexity as high.

    Patch Available

    Johnson Controls has released version v2.01.01 to address the flaw and published Product Security Advisory JCI-PSA-2026-28 with mitigation guidance. CISA and the vendor recommend upgrading affected Simplex Incident Manager deployments (v2.01 and earlier), restricting local system access to authorized personnel, deploying endpoint monitoring to detect memory-dumping activity, enforcing least-privilege access controls, and using full-disk encryption and secure boot to reduce the risk of offline memory analysis.

    Johnson Controls reported the vulnerability to CISA. No public evidence of active exploitation has been disclosed.

    Sources

  • CISA, NSA and FBI Warn of Active AI-Assisted Reconnaissance Against Siemens S7 PLCs

    CISA, NSA and FBI Warn of Active AI-Assisted Reconnaissance Against Siemens S7 PLCs

    Joint Advisory Warns of Active Targeting

    The National Security Agency, the Cybersecurity and Infrastructure Security Agency, the FBI, the Department of Energy and the Environmental Protection Agency released a joint cybersecurity advisory on August 19, 2026, warning that threat actors are actively targeting Siemens S7 Series programmable logic controllers (PLCs) that are exposed to the internet or insufficiently segmented from it. The advisory, designated AA26-231A, covers the S7-200, S7-300, S7-400, S7-1200 and S7-1500 controller families, including the F-series safety variants.

    According to the agencies, the activity spans several critical infrastructure sectors, with Critical Manufacturing, Energy, Water and Wastewater, Chemical, Food and Agriculture, and Commercial Facilities named as the most-targeted. Siemens S7 controllers are also used in the Defense Industrial Base, which the advisory says could be affected as well. CISA describes the threat as “not a theoretical risk” and says exploitation of poorly protected PLCs could disrupt industrial processes, damage equipment, trigger safety incidents through manipulation of interlocks or emergency shutdown systems, and cause cascading effects across interconnected systems.

    AI-Generated Scripts and the Snap7 Library

    The advisory says the threat actors are combining publicly available industrial automation tooling with AI-assisted scripting to build custom software that mimics legitimate operational-technology monitoring tools. Specifically, the agencies describe adversaries using internet-scanning services such as Censys and ZoomEye to locate exposed S7 controllers, then deploying AI-generated Python scripts built on the open-source snap7 library to read and write PLC memory, configuration data and ladder-logic programs over the S7comm protocol on TCP port 102. CISA characterizes the use of AI to generate this exploitation code as “an evolution in threat actor capabilities” that lowers the technical bar for building working industrial-control exploitation tools and speeds adversaries’ ability to adapt to defenses.

    The agencies assess the pattern observed so far as consistent with reconnaissance and capability development — testing techniques against specific PLC models and using read access to understand target environments — rather than a confirmed disruptive attack. The advisory maps the observed techniques to the MITRE ATT&CK for ICS and Enterprise frameworks and to MITRE D3FEND countermeasures.

    A Distinct Threat From the Iran-Linked Water Sector Warning

    AA26-231A is separate from an earlier joint advisory, AA26-097A, which described confirmed Iran-linked exploitation of PLCs at a U.S. water-sector victim, including modification of ladder logic that disabled safety shutdown and alarm functions. The new Siemens-specific advisory does not attribute the reconnaissance activity it describes to any named nation-state or group, and it explicitly frames the observed activity as pre-attack staging rather than a confirmed disruptive incident. CISA also cautions that PLC targeting more broadly extends beyond Siemens equipment, and that the Siemens-specific guidance in the advisory should be treated as one subset of a wider threat landscape facing internet-exposed industrial controllers.

    Mitigations Recommended by the Authoring Agencies

    The agencies are urging asset owners to inventory all Siemens S7 controllers in their environments, apply available firmware and engineering-software patches, verify that PLCs are not reachable from the internet, and block TCP port 102 at perimeter firewalls. Additional recommendations include restricting engineering-workstation access through IP or MAC allowlisting, enabling PLC password protection and configurable read/write protection levels, deploying ICS-aware intrusion detection, and monitoring for anomalous S7comm traffic patterns, unauthorized write operations, and use of the snap7 library outside approved engineering systems. The advisory also recommends organizations that rely on third-party systems integrators or managed service providers share the guidance with those parties directly, since asset owners may not always be aware that PLCs accessible to vendors are also exposed to the wider internet.

    Sources

  • Integrated DAS and DTS: Combining Acoustic and Thermal Intelligence

    Integrated DAS and DTS: Combining Acoustic and Thermal Intelligence

    DAS and DTS observe different physical phenomena, but together they can provide a richer view of critical infrastructure. Acoustic events may indicate movement or mechanical activity while temperature changes reveal thermal stress, fire or abnormal operating conditions.

    Complementary sensing

    DAS detects vibration and acoustic signatures; DTS measures distributed temperature. Combining both allows the same corridor to be monitored for security events and asset-condition changes.

    Power and cable networks

    DTS can identify thermal loading while DAS detects nearby digging, disturbance or unusual vibration. The combination supports both reliability and physical protection.

    Pipeline corridors

    DAS can classify activity and acoustic events while DTS contributes thermal context where product temperature or leak-related effects are relevant.

    Unified analytics

    The challenge is turning two large data streams into usable alarms. Edge processing, event correlation and GIS visualization can help operators focus on meaningful anomalies.

    Procurement implications

    Buyers should evaluate integration at the data and workflow level, not simply whether two interrogators can be installed in the same cabinet. Shared timing, location mapping, APIs and alarm management are central to real operational value.

    Conclusion

    Integrated DAS and DTS for Critical Infrastructure Monitoring should be evaluated as part of a broader operational architecture. The strongest deployments combine suitable sensing technology, resilient communications, clear procedures and measurable performance rather than relying on a single device or headline specification.

  • Electrical Substation Security and Condition Monitoring

    Electrical Substation Security and Condition Monitoring

    Substations are compact but high-consequence sites. Physical intrusion, equipment failure, overheating and fire can all disrupt the grid, so security and condition monitoring increasingly converge.

    Layered physical protection

    Fences, gates, access control and intrusion detection form the basic security perimeter. Radar, thermal and video analytics can provide earlier awareness around remote or unmanned substations.

    Thermal condition monitoring

    Transformers, connectors, switchgear and cable terminations can develop abnormal heat before failure. Fixed thermal cameras and temperature-sensing systems help operations teams identify trends before they become outages.

    Fiber sensing opportunities

    DTS can monitor power cables and long routes for thermal anomalies, while DAS can detect vibration, digging or physical disturbance near critical lines. Together they create a continuous sensing layer beyond the fence.

    Cyber-physical integration

    Modern substations contain networked protection and control equipment. Physical security events should therefore be correlated with network and operational alarms rather than handled in a separate silo.

    Resilience as the design goal

    The purpose of substation security is not simply to detect trespass. It is to protect continuity of service. Redundant communications, backup power, secure remote access and tested response procedures are therefore core design requirements.

    Conclusion

    Electrical Substation Security and Condition Monitoring should be evaluated as part of a broader operational architecture. The strongest deployments combine suitable sensing technology, resilient communications, clear procedures and measurable performance rather than relying on a single device or headline specification.

  • Thermal Runaway Detection in Lithium-Ion Battery Facilities

    Thermal Runaway Detection in Lithium-Ion Battery Facilities

    Lithium-ion battery facilities require a fire-safety strategy built around the chemistry of the cells themselves. One of the most important hazards is thermal runaway: a self-accelerating process in which internal heat generation drives further chemical reactions and can eventually produce venting, fire or propagation to neighboring cells.

    What can be detected before flames appear? Early indicators may include abnormal cell voltage, temperature rise, pressure changes and the release of volatile gases. Battery management systems provide valuable electrical and temperature data, but they should not be the only source of warning. Independent gas, smoke and thermal sensing can create a second layer of protection.

    Gas detection During cell decomposition, gases can be released before visible smoke or flame. Properly selected gas sensors can therefore provide valuable pre-fire warning. Their performance depends on airflow, sensor location, battery chemistry and alarm thresholds.

    Thermal monitoring Point temperature sensors, distributed temperature sensing and infrared thermal imaging can identify unusual heating. In large installations, the advantage of distributed monitoring is the ability to observe temperature trends across many racks, cables or zones rather than relying on a few isolated measurement points.

    Smoke and aspirating detection Very early warning smoke detection can identify small concentrations of aerosols. Aspirating systems are particularly useful where air movement is controlled and where conventional point detectors might not sample the most relevant airflow path quickly enough.

    From alarm to action Detection is only useful if it drives a defined response. A facility should specify what happens when a battery warning, off-gas alarm, elevated temperature or confirmed fire condition occurs. Possible responses include isolating a rack, stopping charge or discharge, controlling ventilation, initiating suppression, notifying emergency teams and increasing separation from adjacent equipment.

    The most resilient approach is multi-layered. Electrical telemetry sees one part of the problem, gas sensing another, thermal monitoring another and fire detection another. Correlating those signals can provide earlier and more reliable warning than relying on a single technology.

  • BESS Fire Detection: Early Warning for Battery Energy Storage Systems

    BESS Fire Detection: Early Warning for Battery Energy Storage Systems

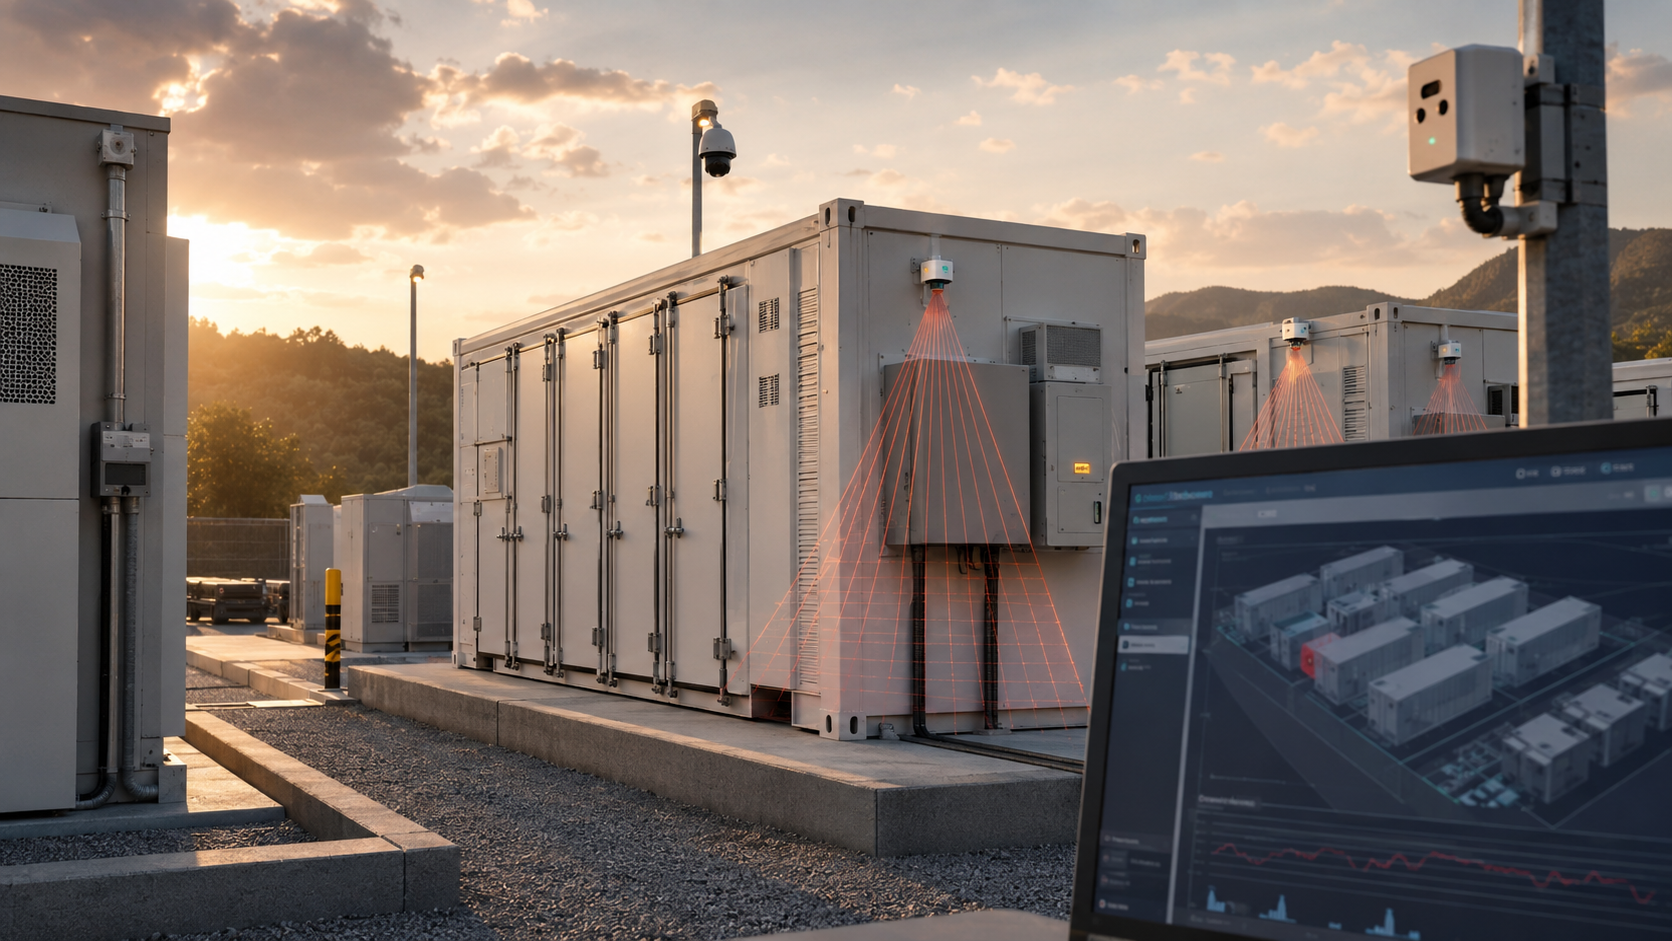
    Battery energy storage systems are expanding rapidly because they help stabilize grids, support renewable energy and provide backup power. Their fire-safety challenge is different from that of conventional buildings: lithium-ion cells can fail internally, generate heat and flammable gases, and progress into thermal runaway before visible flames appear.

    Why early warning matters A traditional smoke detector may only respond after decomposition has advanced. BESS protection therefore benefits from layered detection. Battery management systems can track abnormal voltage, current and temperature. Gas sensors can identify characteristic off-gassing. Aspirating smoke detection can reveal very small combustion aerosols, while thermal sensors and infrared monitoring can highlight localized heating.

    Thermal runaway is a process, not a single event Thermal runaway occurs when heat generation inside a cell exceeds its ability to dissipate heat. The rising temperature can accelerate chemical reactions, release gases and transfer heat to neighboring cells. A key engineering objective is to detect abnormal conditions early enough to isolate equipment, reduce propagation risk and give operators useful time to respond.

    Detection architecture A robust BESS design combines cell- and rack-level telemetry with room or container-level fire detection. Alarm thresholds should be coordinated so operators can distinguish equipment warnings, confirmed fire conditions and emergency states. Integration with ventilation, shutdown logic, suppression systems and remote monitoring is essential.

    Avoiding a single-sensor strategy No single sensing technology provides a complete picture. Temperature alone can miss early off-gassing; gas detection can be affected by airflow; smoke detection may respond later than internal battery diagnostics. Combining independent indicators reduces blind spots and improves confidence.

    Commissioning and maintenance Detector placement, airflow modelling, sensor calibration and alarm verification are critical. Battery layouts change, firmware evolves and ventilation patterns can be modified during maintenance. Fire detection should therefore be reviewed whenever the storage system is reconfigured.

    The direction of the industry is toward integrated battery intelligence: BMS data, gas detection, thermal monitoring and fire systems feeding a common operational view. In BESS safety, the most valuable alarm is usually the one that arrives before a visible fire begins.

  • Gas Detection in Industrial Facilities

    Gas Detection in Industrial Facilities

    Industrial gas detection protects people, processes and facilities by identifying hazardous concentrations before they cause poisoning, fire or explosion. The system design depends on the gas, process conditions and the physical behavior of a potential release.

    Combustible gas detectors monitor flammable vapors or gases and are commonly used around fuel systems, process equipment and storage areas. Toxic gas detectors target substances that can harm personnel at relatively low concentrations. Oxygen sensors are used where depletion or enrichment can create danger.

    Several sensing technologies are available, including catalytic bead, infrared, electrochemical and semiconductor methods. Each has different strengths, cross-sensitivities, maintenance requirements and expected service life.

    Placement is one of the hardest engineering decisions. Gas density, ventilation, wind, leak sources and enclosure geometry influence where a cloud may travel. Detectors should therefore be positioned using hazard analysis rather than simple spacing rules.

    Fixed systems can be complemented by portable instruments worn by workers or used during maintenance. Wireless detectors may provide temporary coverage during shutdowns, construction or changing process conditions.

    Gas detection should connect to alarms and, where appropriate, ventilation, shutdown or emergency-isolation systems. Calibration, bump testing and sensor replacement are critical because a detector that is installed but not maintained can create false confidence.

    The strongest gas-detection programs combine correct sensor technology, risk-based placement, disciplined maintenance and clear response procedures. Detection is only valuable when the organization knows what action should follow the alarm.

  • Flame Detection Technologies: UV, IR and Multispectrum

    Flame Detection Technologies: UV, IR and Multispectrum

    Flame detectors are designed for hazards where open combustion may develop rapidly and waiting for smoke or heat to travel to a ceiling detector would be too slow. They are widely used in oil and gas, petrochemical plants, fuel storage, turbines, aircraft hangars and other high-risk industrial environments.

    Ultraviolet detectors respond to UV radiation produced by many flames. They can react quickly but may require careful management of other UV sources. Infrared detectors monitor characteristic IR wavelengths associated with combustion and can be effective over longer distances.

    Dual- and multispectrum detectors compare several wavelength bands to improve discrimination. By analyzing the relationship between bands and the flicker characteristics of fire, modern detectors can reject many false-alarm sources while maintaining fast response.

    Coverage is line-of-sight. A flame detector cannot see through equipment, walls or dense smoke, so field of view and mounting geometry are essential design factors. Multiple detectors may be required around complex process equipment.

    Environmental conditions also matter. Sunlight, welding, hot machinery, reflections and weather can influence performance depending on detector type. Selection should be based on the expected fuel and credible fire scenario, not simply maximum advertised range.

    Flame detection is most effective when integrated with process shutdown, alarm and suppression logic. In high-hazard facilities, a few seconds of earlier detection can materially change the outcome of an incident.

  • Tethered Drones for Industrial Site Monitoring

    Tethered Drones for Industrial Site Monitoring

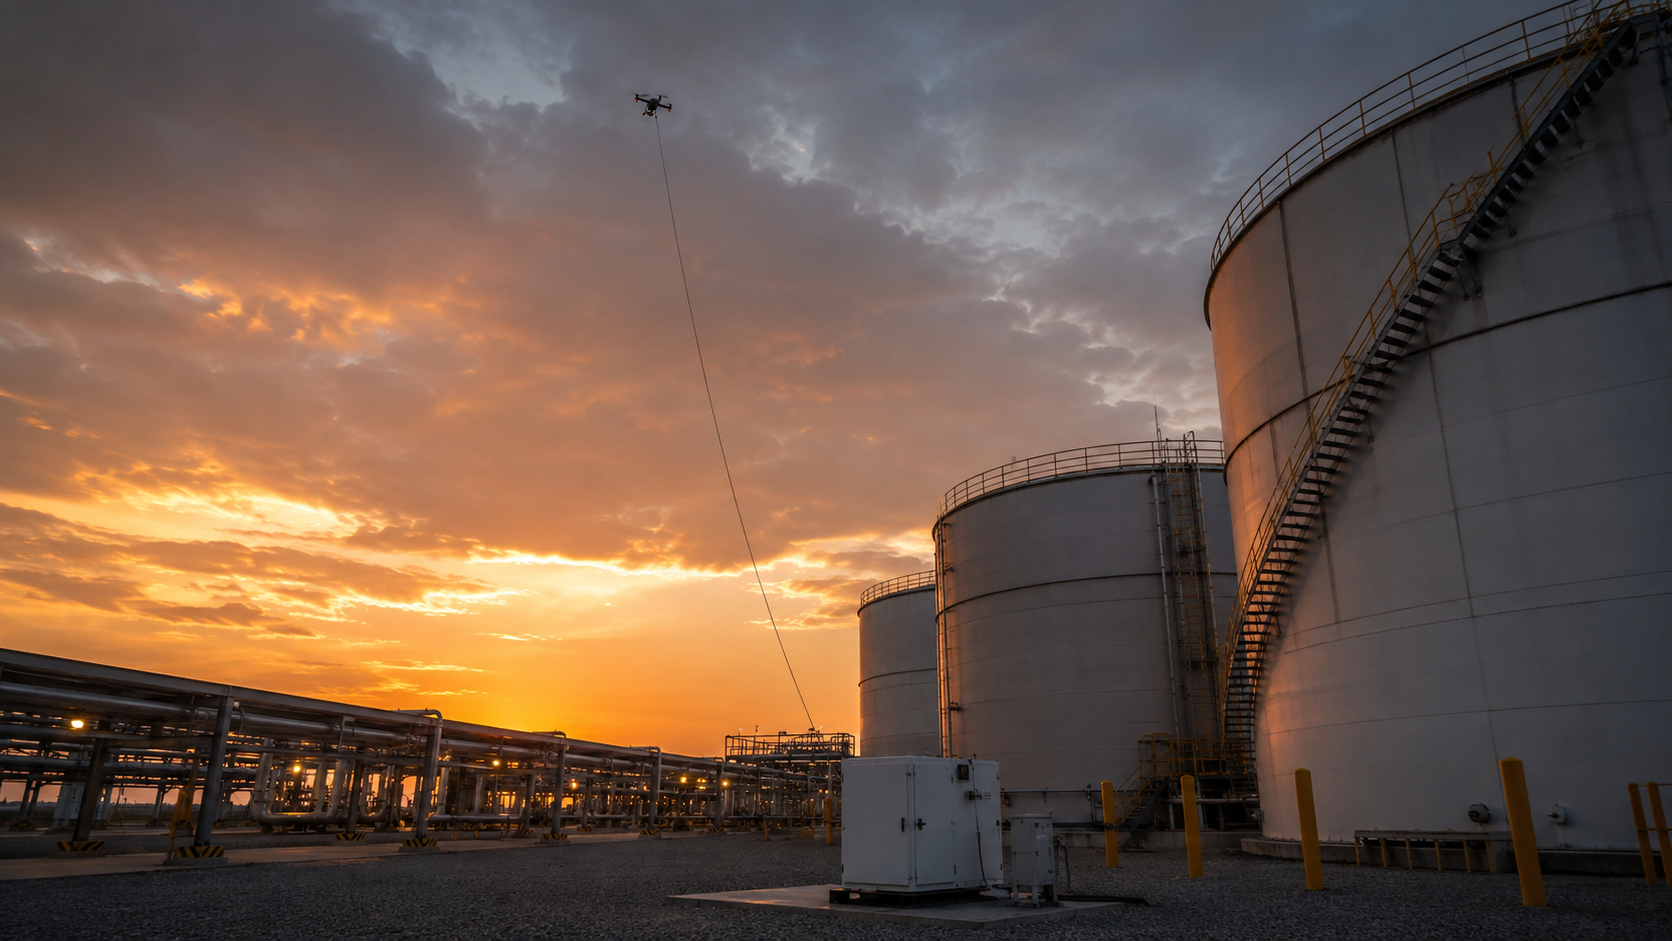
    Tethered drones occupy an unusual position between fixed surveillance towers and free-flying unmanned aircraft. Connected to the ground by a cable that can provide power and communications, a tethered drone can remain airborne for extended periods while carrying cameras, thermal sensors, communications equipment or other payloads.

    For industrial security, the main advantage is persistent elevated observation. A drone positioned tens of meters above a refinery, port, mine, pipeline construction zone or temporary event can see over fences, buildings and terrain that would block ground cameras. Because power is supplied from the ground, endurance can be measured in hours or days rather than the battery life of a conventional drone.

    The tether can also provide a secure high-bandwidth data path, reducing dependence on wireless links. This is useful where video quality, cyber security or RF congestion is a concern.

    Tethered systems still have operational limits. Wind, lightning, aviation restrictions, tether management and safe operating areas must be considered. They are not suitable everywhere, and the aircraft remains a visible physical asset that requires maintenance and procedures.

    Their strongest use case is usually temporary or semi-permanent overwatch: construction projects, incident response, large industrial shutdowns, border posts, temporary perimeter expansion or remote facilities where installing a tower would take longer.

    Tethered drones should be integrated with the wider security system rather than treated as standalone cameras in the sky. Video can feed the VMS, analytics can monitor defined zones and command-center operators can correlate aerial views with ground sensors.

    As industrial sites seek flexible surveillance coverage, tethered drones provide a middle ground between permanent infrastructure and mobile airborne patrol.

  • AI Data Center Growth Expands Power, Safety and Security Risk Planning

    AI Data Center Growth Expands Power, Safety and Security Risk Planning

    2025–2026 — Rapid AI data-center construction is forcing operators to treat power availability, fire safety, physical protection and cyber resilience as one connected risk program.

    What happened

    AI workloads are accelerating demand for high-density computing facilities and the energy systems that support them. The International Energy Agency’s Energy and AI work describes the growing relationship between data centers and electricity systems, while large infrastructure announcements show that the buildout is already moving into physical delivery.

    Why it matters

    The risk is not simply higher electricity consumption. Dense compute changes cooling, backup power, battery, fire-detection and business-continuity requirements. New sites also add construction-stage access, supplier and commissioning risks before normal operations begin.

    Security and infrastructure impact

    A defensible design connects cyber and physical controls: segmented building and OT networks, managed contractor identities, layered perimeter detection, validated fire scenarios and a command process that can correlate facility, security and IT alarms.

    Sources

    ← Back to Technology News