Tag: Video Surveillance

  • Edge Recording and Video Backfill: Closing Gaps After Network Outages

    Edge Recording and Video Backfill: Closing Gaps After Network Outages

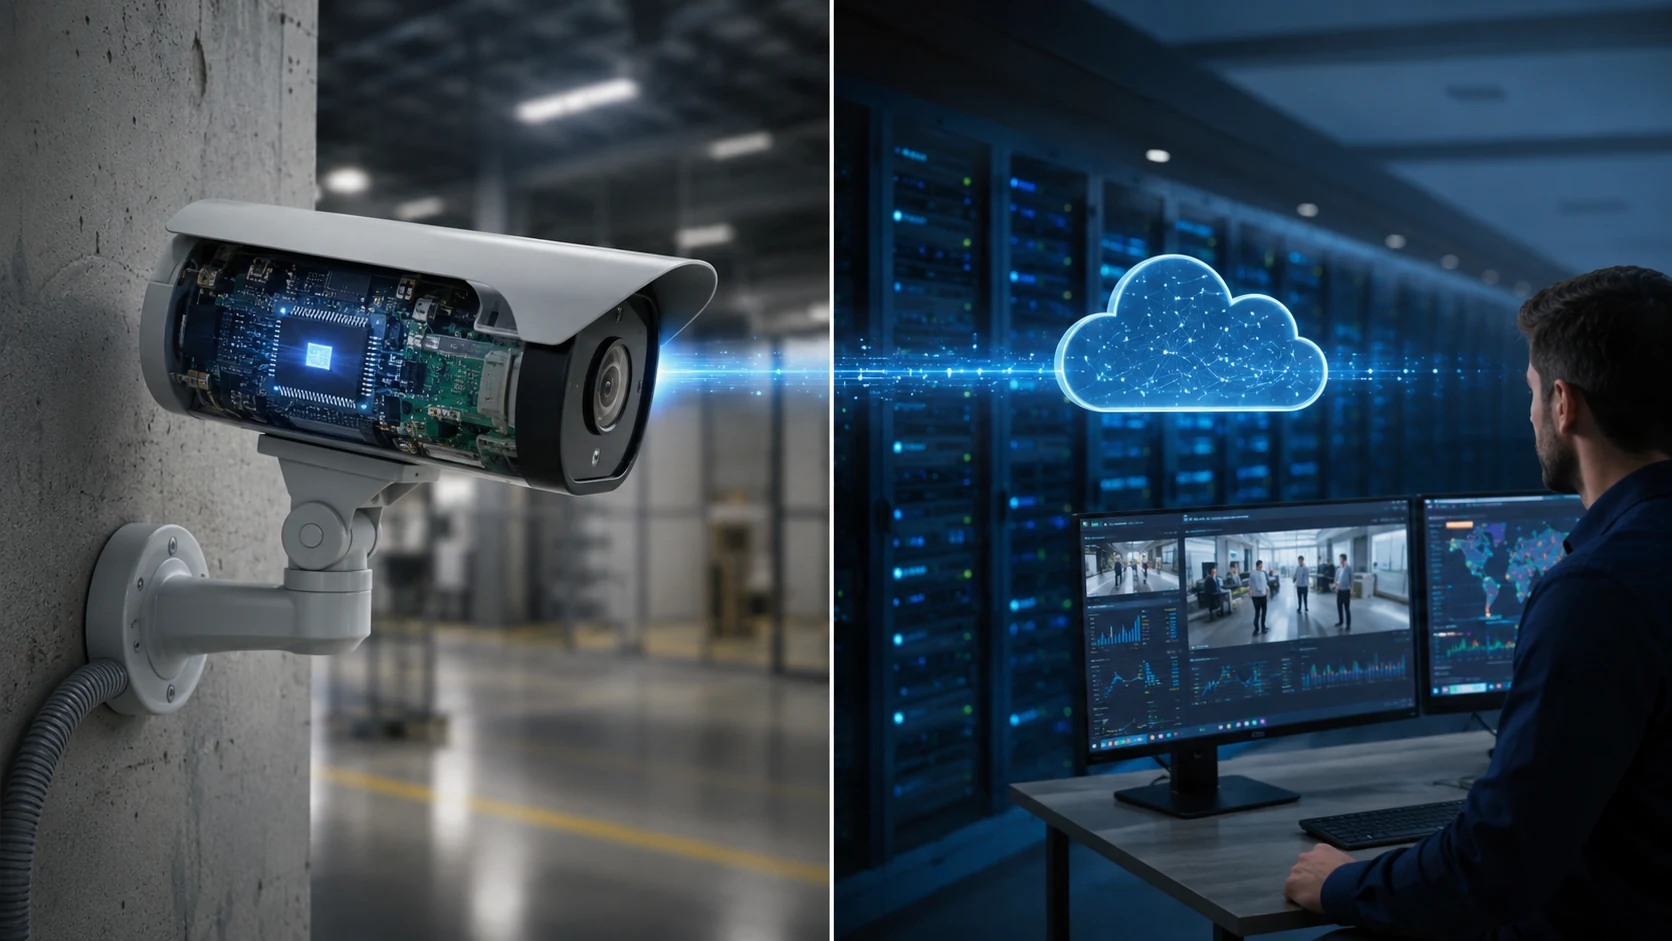
    A network video system can lose its connection to the recorder without losing the event itself. Cameras with supported edge storage can continue recording locally and later return missing footage to a video management system. That recovery process is often called video backfill, failover recording or edge-storage synchronization.

    The idea is simple, but dependable operation requires coordinated camera, storage, time, network and VMS behavior. An SD card in a camera does not automatically guarantee that footage will be discovered, transferred and presented correctly after an outage.

    What Edge Recording Protects Against

    Local recording is useful when the camera remains powered but temporarily loses its route to the central recorder. Common causes include switch failure, uplink interruption, recorder maintenance or a WAN outage at a remote site. It does not protect against every failure: loss of camera power, physical destruction, storage-card failure or theft can still remove the local evidence.

    Designers should define the failure modes they intend to cover and avoid describing edge storage as a universal backup. Power resilience and physical protection remain separate requirements.

    How Backfill Works

    During normal operation, the VMS receives live streams and records them centrally. If the connection fails, the camera records to approved local media. When communication returns, the VMS identifies the missing time range, requests the stored recording and merges or indexes it in the evidence timeline.

    ONVIF Profile G defines standardized functions for configuring, requesting and controlling recording from conformant devices. Conformance can improve interoperability, but buyers still need to verify the exact camera, firmware, storage medium and VMS combination. Optional features and vendor-specific behavior can affect the result.

    Time Synchronization Determines Evidence Quality

    Backfill depends on accurate timestamps. If a camera clock drifts during isolation, returned footage may overlap, leave apparent gaps or appear out of order. Cameras, recorders and supporting infrastructure should use a monitored time source, with alerting for excessive drift.

    Commissioning should include a deliberate network interruption long enough to create a visible recording gap, followed by reconnection and timeline review. Operators should confirm that search, export and evidentiary timestamps remain coherent.

    Control Recovery Bandwidth

    When many cameras reconnect together, simultaneous uploads can compete with live video and other operational traffic. Recovery policies should limit concurrency or bandwidth, prioritize critical cameras and consider site uplink capacity. A remote location with a narrow WAN path may require staged transfer over hours rather than immediate synchronization.

    The retention window at the edge must be long enough for the expected outage plus recovery delay. High resolution, high frame rate and complex scenes consume local storage faster, so capacity should be calculated from measured or conservatively estimated bitrates.

    Storage Media Is a Maintained Component

    Use media approved for the camera and expected write workload. Continuous video recording can wear consumer-grade cards quickly, particularly in hot enclosures. Systems should report missing, read-only or failed storage where supported, and maintenance teams should verify those alarms reach a monitored workflow.

    Encryption, card removal and evidence handling also deserve attention. Locally stored footage may contain the same sensitive material as the central recorder, so access control and disposal procedures should cover edge media.

    Commissioning and Operations Checklist

    • Confirm the supported camera, firmware, storage and VMS combination.
    • Measure usable edge retention under representative video settings.
    • Interrupt the network and verify continued local recording.
    • Reconnect and confirm backfill, timestamps, search and export.
    • Test simultaneous recovery without degrading live video.
    • Alert on storage failure, clock drift and prolonged disconnection.
    • Repeat the test after major firmware or VMS upgrades.

    Edge storage should be part of a documented continuity plan, not an unchecked feature box. NIST contingency-planning guidance similarly emphasizes defined recovery requirements, testing and maintenance. For the wider camera, VMS and storage architecture, see SectechMedia’s video surveillance systems guide.

    References

  • ViewScan Expands AI Monitoring Platform and Relaunches Customer-Facing Website

    ViewScan Expands AI Monitoring Platform and Relaunches Customer-Facing Website

    ViewScan, Inc. has released an update to its ViewScan Protect AI-powered monitoring platform alongside a redesigned website built to give partners and customers easier access to supporting resources. The refreshed site adds real-world AI event videos, case studies, white papers, client testimonials and an FAQ section.

    Positioning around privacy and continuous monitoring

    “We pride ourselves on staying at the forefront of AI technology and keeping our customers’ privacy protected with flexible and cost-effective solutions that monitor their facilities 24/7 for total peace of mind,” said David Antar, president at ViewScan. The company frames the update as a continuation of its focus on AI-driven analytics for continuous facility monitoring rather than a one-time camera-plus-recorder deployment model.

    A crowded but growing category

    ViewScan’s refresh lands in an AI video-monitoring market where new entrants and established security integrators alike are racing to differentiate on detection accuracy, false-alarm reduction and ease of integration with existing camera infrastructure. Clearer documentation and case-study evidence, the kind the new site promises, is increasingly what separates vendors in AI-powered security from being judged on marketing claims alone.

    Sources and further reading

  • Private Equity Firm GTCR Acquires Cellular Camera Maker Tactacam

    Private Equity Firm GTCR Acquires Cellular Camera Maker Tactacam

    Private equity firm GTCR has acquired Tactacam, a maker of cellular-connected cameras for the outdoor and security markets, from Bertram Capital and the company’s founders. The deal closed September 28; terms were not disclosed, though people familiar with the transaction told the Wall Street Journal it was valued well north of $1 billion.

    Cellular cameras beyond Wi-Fi range

    Tactacam’s Reveal and Defend product lines rely on cellular connectivity rather than Wi-Fi, letting cameras operate for property and perimeter monitoring in locations without a reliable local network — a use case that overlaps with rural and remote-site physical security as much as with the outdoor recreation market the company built its name in. Billings, Montana-based Tactacam was founded in 2013; CEO and co-founder Jeff Peel will continue leading the company and retain a significant ownership stake alongside co-founder Ben Thorud.

    Another security bet for GTCR

    The acquisition adds Tactacam to a GTCR security portfolio that already includes commercial systems integrator Everon and residential provider SimpliSafe, continuing a pattern of consolidation in camera-based security products and companies as private equity firms build connected-monitoring platforms spanning both consumer and commercial markets.

    Sources and further reading

  • Vendor Proposal Would Add Facial Recognition to Exported Flock Camera Data

    Vendor Proposal Would Add Facial Recognition to Exported Flock Camera Data

    A surveillance software vendor has proposed combining exported Flock Safety imagery with facial-recognition capabilities in a separate evidence platform, according to reporting based on a sales approach to a Tennessee police department. The proposal highlights how data can acquire new analytical uses after it leaves the system that originally collected it.

    The proposed integration is not a deployed Flock feature

    VIDIZMO described bringing Flock data, body-camera footage and other evidence into its Intelligence Hub for search and analysis. The company’s chief executive told reporters that it had not used facial recognition on Flock footage and had not built the specific export tool required for the proposed workflow.

    Flock states that its cameras do not use facial recognition and that its license-plate system searches vehicle characteristics rather than identity. The proposed biometric analysis would therefore occur downstream in another vendor’s environment, not inside Flock cameras or Flock’s own recognition process.

    Data-governance boundaries must survive export

    Agencies evaluating video integrations should define allowed analytics, retention, audit logging and approval requirements before moving evidence between platforms. Procurement controls should address downstream processing as well as the capabilities of the original camera system. SectechMedia follows related developments in its video surveillance and imaging coverage.

    Sources

  • Perimeter Lighting and Camera Co-Design Audit

    Perimeter Lighting and Camera Co-Design Audit

    Perimeter lighting and video surveillance are often designed by different teams, yet their performance is tightly coupled. More light does not automatically produce better evidence. Poor aiming can create glare, deep shadows, reflections and rapid exposure changes that reduce recognition and destabilize analytics. A co-design audit evaluates the camera, luminaire and scene as one sensing system.

    Define the operational task

    For each camera, state whether the objective is detection, observation, recognition or identification. Record the target area, expected movement, required retention and operator response. Lighting criteria should follow that task rather than a generic site-wide brightness value.

    Document camera position, lens, field of view, mounting height, day/night mode, infrared capability and analytics zones. For lighting, record luminaire type, beam pattern, color characteristics, controls, power source and maintenance condition.

    Measure the scene after dark

    Inspect the perimeter under representative night conditions. Evaluate horizontal and vertical illumination, uniformity, contrast and the transition between bright and dark areas. Camera targets are three-dimensional, so a well-lit ground plane may still leave faces or vehicle markings in shadow.

    Observe direct glare into the lens, reflections from fencing or wet surfaces and backlighting from roads or adjacent properties. Test with foliage, gates and parked vehicles in their realistic positions. CISA physical-security guidance emphasizes layered assessment rather than dependence on one control.

    Test camera response and analytics

    Review live and recorded video while a representative target moves through the scene. Check shutter behavior, motion blur, noise, white balance, infrared cutover and compression. Confirm that illumination changes do not wash out nearby targets or hide distant ones.

    Run analytics acceptance tests across the full zone and at boundary conditions. Headlights, insects, rain and moving shadows can create nuisance alarms. SectechMedia’s guide to video analytics recommissioning provides a structured method for validating zones after scene changes.

    Coordinate resilience and controls

    Determine what happens during utility failure, generator transfer and lighting-control network loss. Critical cameras may require emergency illumination or independent infrared coverage. Avoid a single control command that can disable both lighting and surveillance without an alarm.

    Access to lighting controls should be restricted and logged. Time schedules, photocells and central management commands need consistent clocks and documented overrides.

    Document corrective action and seasonal change

    Use annotated images to record glare, shadows, dead zones and recommended aiming or equipment changes. Re-test after vegetation growth, construction, fence modifications or luminaire replacement. Clean lenses and fixtures, verify mounts and trend failed lamps. A successful audit proves that the combined system delivers usable evidence and stable detection under actual night conditions.

    Sources

  • Camera Privacy Mask Persistence and Configuration Drift Testing

    Camera Privacy Mask Persistence and Configuration Drift Testing

    Privacy masks are intended to prevent operators, recordings and downstream analytics from viewing protected areas. A mask that appears correct during commissioning can drift after a lens adjustment, electronic stabilization change, camera replacement, firmware update or preset modification. Persistence testing proves that protection remains aligned throughout the camera’s real operating modes.

    Define the protected scene and policy

    Document the reason for every mask, the protected geometry and the views in which it must apply. Record camera model, firmware, lens position, resolution, orientation and image-correction settings. Use fixed scene references such as wall edges, windows or structural markers rather than movable furniture or vehicles.

    Screenshots alone are insufficient because they do not describe what happens during zoom, day/night transition or restart. Identify the approved owner and the change process for every mask.

    Test every relevant video path

    Verify the mask in live view, recorded playback, secondary streams, mobile clients, video wall decoders and exported clips. Confirm that snapshots, thumbnails and analytics previews do not reveal the protected region. If the camera generates metadata outside the masked image, determine whether coordinates or classifications still expose sensitive activity.

    Test each supported resolution and aspect ratio. A mask defined in one coordinate system may shift when a stream is cropped or rotated. SectechMedia’s guide to video analytics zone recommissioning provides a related method for checking scene geometry.

    Exercise movement and operating modes

    For PTZ cameras, test every preset, patrol and manual limit. Confirm whether masks are tied to absolute pan, tilt and zoom coordinates and remain stable during movement. For fixed cameras, exercise optical zoom, electronic stabilization, dewarping, corridor mode and day/night switching.

    Observe transitions rather than only final positions. A protected window should not become briefly visible while a preset moves or exposure changes.

    Introduce controlled configuration changes

    Reboot the camera and recorder, restore a configuration backup on a representative device and apply a supported firmware update. Verify mask count, shape, position and enforcement after each action. Compare current configuration with an approved baseline so drift can be detected before visual inspection.

    Restrict mask editing to authorized roles and confirm that changes create an audit event. Management exports containing mask coordinates should receive the same protection as other sensitive configuration data.

    Document evidence and re-test triggers

    Retain annotated reference images from each stream and mode, configuration hashes where supported, operator identity and test timestamps. Classify failures as geometry, client, recording, analytics or change-control issues. Re-test after camera movement, lens service, firmware change, scene construction or privacy-policy revision. NIST security and privacy frameworks provide a governance basis for maintaining this evidence.

    Verify operator and recorder behavior

    Confirm that unauthorized roles cannot disable or resize masks and that recorder-side overlays do not replace camera enforcement. Review audit logs for every approved change, then compare live, recorded and exported views after the configuration is saved.

    Reference sources

  • Security Device Certificate Lifecycle and Expiration Testing

    Security Device Certificate Lifecycle and Expiration Testing

    Certificates increasingly protect communication between cameras, access-control controllers, recorders, management servers and operator clients. They can also become a hidden single point of failure. An expired certificate may block management access, interrupt event delivery or encourage operators to bypass validation during an outage. Lifecycle management must therefore be tested as an operational control, not handled as an annual spreadsheet exercise.

    Build an ownership-based inventory

    Record every certificate’s subject, issuer, serial number, validity period, key use, endpoint, trust chain and responsible owner. Include embedded devices, reverse proxies, APIs, mobile credentials and internal services. The inventory should distinguish public certificates from private-public-key-infrastructure certificates and device-generated self-signed certificates.

    Ownership matters because renewal may involve different teams. A security integrator may manage cameras, corporate infrastructure may operate the certificate authority and a vendor may control a cloud connector. Every certificate needs a named decision path before expiration.

    Test validation from the real clients

    A certificate can look correct in a management console while failing on a recorder or legacy controller that lacks the issuing chain. Test from each client class, including operator workstations, mobile applications, APIs and failover servers. Validate hostname matching, trust anchors, revocation behavior and time synchronization. NIST key-management guidance stresses that cryptographic controls depend on protected keys, defined lifecycles and accountable processes.

    Do not disable validation to make a test pass. If a client cannot support the required trust model, document the limitation and isolate the risk while planning replacement or an approved gateway.

    Exercise renewal before the deadline

    Use a non-production endpoint or canary device to rehearse certificate signing requests, approval, installation and service restart requirements. Confirm whether private keys can remain on the device and whether renewal changes fingerprints used by integrations. Test overlapping validity so a new chain can be distributed before the old one expires.

    Automated monitoring should warn at multiple thresholds, but alerts are not enough. A renewal exercise should prove that the team can obtain, deploy and validate the replacement within the available window. SectechMedia’s guide to asset inventory and configuration management shows how ownership and baseline records support this process.

    Protect keys and recovery material

    Private keys should be generated and stored according to the device’s risk and capabilities. Restrict export, protect enrollment credentials and log administrative changes. Where hardware-backed storage is unavailable, use compensating controls such as network isolation, least-privilege management and rapid revocation procedures.

    Back up certificate authority configuration and document recovery dependencies, but avoid copying private keys into general ticket systems or shared folders. Recovery tests should prove that certificates can be reissued without reusing compromised key material.

    Measure lifecycle health

    Useful metrics include unknown certificates, certificates without owners, failed validation paths, renewals completed before threshold and emergency exceptions. Review the inventory after device replacement, firmware updates and architecture changes. The objective is not merely zero expirations; it is sustained encrypted trust that survives routine maintenance and incident response.

    Reference sources

  • IP Camera Firmware Update Validation and Rollback Planning

    IP Camera Firmware Update Validation and Rollback Planning

    Firmware updates are essential to IP camera security, but an update is also a controlled change to a live sensing and evidence system. A camera that reboots successfully may still return with altered analytics, lost certificates, incorrect time, a changed stream profile or broken VMS integration. Effective update management therefore combines cybersecurity urgency with operational acceptance testing.

    Start with a precise asset baseline

    Record the camera model, hardware revision, current firmware, bootloader where exposed, configuration export, certificates, stream settings, analytics rules, time source and VMS association. Confirm that the vendor package applies to the exact device variant and read every intermediate-version requirement. NIST’s enterprise patch-management guidance emphasizes risk-based planning, inventory and verification rather than treating updates as a single technical event.

    The baseline should include current image quality, frame rate, bitrate, event generation and recording behavior. For critical cameras, retain representative clips and screenshots so the team can compare performance after the change.

    Use a representative canary group

    Select cameras that reflect the deployed fleet without placing the highest-risk coverage point first. Include at least one device using each important integration pattern, such as edge analytics, external I/O, encrypted streaming or local storage. Apply the update during a defined window and keep the rest of the fleet unchanged until the canary completes observation.

    Check whether the firmware resets credentials, disables protocols, regenerates certificates or changes default security behavior. These may be intentional improvements, but they must be incorporated into the deployment plan before scale-up.

    Validate function, security and evidence

    Acceptance testing should cover live and recorded video, stream negotiation, low-light transitions, analytics events, alarm metadata, audio where authorized, local storage, health monitoring and VMS failover. Confirm NTP synchronization and compare timestamps across camera, recorder and operator client. Test authentication with intended roles and verify that deprecated services remain disabled.

    Network monitoring should confirm the expected destinations and ports after update. Unexpected outbound connections, changed DNS behavior or management services on new interfaces require investigation. SectechMedia’s video-surveillance network hardening guide provides a broader control framework for this review.

    Design rollback before deployment

    Rollback may mean a supported downgrade, restoration of a configuration export, replacement with a staged spare or temporary service from an adjacent camera. Do not assume that firmware can be downgraded; verify vendor support and signing restrictions. Define the stop conditions that trigger rollback, the decision owner and the maximum acceptable loss of coverage.

    Keep packages, hashes, configuration backups and test evidence under change control. A completed update record should identify every device, result, exception and follow-up action. This creates an auditable link between vulnerability remediation and continued security coverage.

    Close the change with monitored evidence

    After rollout, monitor reboots, dropped streams, storage gaps, analytics error rates and certificate warnings for a defined period. Reconcile the final firmware inventory against the approved scope. Update documentation and vulnerability records only after operational evidence confirms that the fleet is both patched and functioning.

    Reference sources

  • CISA Warns VIVOTEK Camera Firmware Flaw Could Enable Root Command Execution

    CISA Warns VIVOTEK Camera Firmware Flaw Could Enable Root Command Execution

    CISA has published an industrial control systems advisory for a vulnerability affecting multiple VIVOTEK V Series camera models. The agency says successful exploitation may allow remote command execution, potentially with root privileges, creating a path to full compromise of an affected camera.

    Camera compromise can extend beyond lost video

    The issue is tracked as CVE-2026-22755 and affects listed FD9187, FD9189, FD9365, FD9387, FD9389 and FD9391 models. CISA’s advisory identifies affected firmware and directs operators to vendor-provided updates. A compromised camera can become more than an unavailable sensor: it may expose credentials, provide a foothold into a surveillance network or undermine confidence in recorded evidence.

    Update with inventory and rollback controls

    Operators should first identify exact models and firmware versions, confirm supported upgrade paths and test the update on a representative unit. Network exposure should be minimized, management access restricted and camera traffic segmented from general business systems. After deployment, teams should verify video, analytics, recording, time synchronization and certificate behavior rather than treating a successful reboot as proof of completion. SectechMedia’s guide to camera and VMS cybersecurity hardening provides additional controls for reducing surveillance-network risk.

    Sources

  • Radar-to-Camera Cueing Latency and Handover Validation

    Radar-to-Camera Cueing Latency and Handover Validation

    Perimeter radar can detect and track movement beyond a camera’s fixed view, while a PTZ camera supplies visual verification. The integration is useful only when the camera receives the correct track, arrives quickly enough and keeps the target in view. Acceptance testing should measure the entire handover from detection to operator presentation.

    Define the latency budget

    Break the workflow into radar detection, track confirmation, network delivery, integration processing, PTZ movement, focus and video display. Measuring only the camera’s preset time hides delays elsewhere. Record timestamps from each component using synchronized clocks.

    The acceptable total depends on target speed, range and response purpose. A delay that is acceptable for a walking person may lose a fast vehicle before useful video appears.

    Test geometry and calibration

    Verify radar coordinates, camera location, height, orientation and field of view. Small calibration errors become larger at distance. Test targets at the center and edges of coverage, near zone boundaries and at elevations that differ from the calibration path.

    Confirm how the system chooses between cameras and how it handles overlapping coverage. The nearest camera may not provide the clearest view if structures, vegetation or lighting obstruct the line of sight.

    Exercise track handover

    Use representative people and vehicles moving toward, across and away from the perimeter. Record whether the PTZ reaches the target, how long it maintains the track and what happens when two targets are present. Check transitions between radar sectors or camera responsibility zones.

    Operator displays should preserve track identity when the camera changes. If identifiers are reassigned or merged, responders may follow the wrong target. Video bookmarks and alarm records should retain enough metadata to reconstruct the sequence.

    Validate degraded operation

    Remove a camera, delay metadata or interrupt the radar connection using an approved test. Confirm that the platform reports the degraded state and uses a defined fallback instead of silently showing an unrelated preset. Manual operator control should remain available where the response plan requires it.

    Store accepted latency, calibration data, routes and environmental conditions as a baseline. Repeat after firmware, network, mast or landscape changes. Radar-camera handover belongs within Physical Security assurance because detection, visualization and response must function as one chain.

    Monitor performance after acceptance

    Trend cueing latency, lost tracks, manual overrides and camera-unavailable events. A rising delay can indicate network congestion, integration processing load or mechanical PTZ wear. Establish thresholds that trigger investigation before operators stop trusting automatic handover.

    Preserve representative test routes and target speeds for periodic checks. Seasonal vegetation, new structures and lighting changes can alter visibility even when radar coverage is unchanged. A repeatable route allows the team to distinguish environmental change from software or calibration drift.

    Review representative recorded incidents with operators. Their observations can expose framing or handover problems that automated health monitoring cannot identify.

    Reference sources